Malware Analysis
Learn techniques for analyzing malicious software, including document analysis, .NET and Java reverse engineering, debugging with IDA Pro, and understanding remote access tools and botnets.

Malware Analysis and Reverse Engineering Course
Learn techniques for analyzing and reverse engineering malware to understand its behavior and protect systems from threats.
IDA Pro, Malware Analysis, and Python Libraries for Cybersecurity - Episode 4
Explore IDA Pro, assembly language for malware analysis, and Python libraries for penetration testing in this informative cybersecurity discussion with experts from HackerSploit.
Tracing Stack Usage and Stack Frames in a Debugger
Explore stack usage and stack frames in a debugger, tracing function calls to understand stack operations, calling conventions, and frame unwinding during program execution.
Walking the PEB, Enhancing IDA's Output with Structures, and Unlocking Runtime-Linking - Lecture 4
Explore PEB usage in malware, learn runtime DLL location techniques, and enhance IDA analysis with custom structures for improved reverse engineering.
TLS Callbacks in PE Files - Detection and Analysis
Explore TLS callbacks in PE files, their use in malware, and detection methods. Learn to identify and analyze these anti-debugging techniques using various tools and Yara rules.
Performing Basic Triage Analysis and Unpacking with x64dbg - Ransomware Analysis - Part 2
Perform basic triage analysis on ransomware binaries, compare obfuscated and unobfuscated versions, and learn to unpack using x64dbg and Scylla for effective malware analysis.
Keeping Your Tools Safe IDA
Explore techniques for safeguarding IDA tools and enhancing reverse engineering security in this concise presentation from REcon Brussels 2017.
Automation Techniques in C++ Reverse Engineering
Explore automated dynamic analysis techniques for C++ reverse engineering, focusing on structure usage, function argument types, and inheritance relationships through DLL injection.
IDA Synergy - Collaborative Reverse Engineering
Explore IDASynergy: a collaborative reverse engineering tool combining IDAPython Plugin and version control for efficient team-based analysis of complex software systems.
Python - The Wonder Woman of Embedded Device Reversing
Explore Python's power in embedded device reverse engineering, covering triage, scripting, analysis, and IDA integration for efficient vulnerability research.
Static Binary Analysis - The Essentials
Dive into reverse engineering and static malware analysis essentials with Igor Kuznetsov. Learn visual inspection, disassembly techniques, and structure analysis using IDA Pro and Ghidra.
Extracting an ELF From an ESP32
Detailed exploration of extracting ELF files from ESP32 firmware images, covering binary format analysis, conversion processes, and tools for reverse engineering IoT device firmware.
Augmenting Static Analysis Using Pintool - Ablation
Extracts runtime information to enhance static analysis, resolving virtual calls in C++ binaries and visually comparing samples for efficient vulnerability research and code auditing.
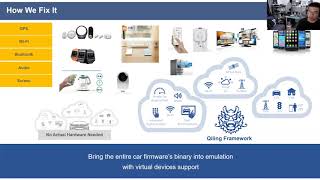
Qiling Framework with IDA Pro
Explore Qiling Framework's sandbox emulation capabilities with IDA Pro for cross-platform binary analysis, fuzzing, and dynamic MBR analysis. Learn to build custom analysis tools using Python APIs.
fn_fuzzy - Fast Multiple Binary Diffing Triage With IDA
Efficient binary diffing tool for IDA Pro, using fuzzy hashes to quickly compare and import function data from multiple IDBs, enhancing malware analysis productivity.
Digging for IE11 Sandbox Escapes Part 1
Explore IE11 sandbox vulnerabilities, focusing on logic bugs and Enhanced Protected Mode. Learn techniques to investigate, analyze, and exploit sandbox weaknesses in Windows 8.1.
Digging for IE11 Sandbox Escapes Part 2
Explore IE11 sandbox vulnerabilities, focusing on logic bugs and Enhanced Protected Mode. Learn to investigate, analyze, and exploit sandbox escapes discovered during a bug bounty program.
Persist It - Using and Abusing Microsoft's Fix It Patches
Explore Microsoft's Fix It patches, their analysis, and potential for system persistence through reverse engineering and exploitation techniques.
Hit Them Where It Hurts - Finding Holes in COTS Software
Explore techniques for identifying vulnerabilities in commercial software, focusing on legal considerations, input tracing, and assembly analysis.
A Deep Look at Stack Buffer Overflows and Format String Vulnerabilities
Explore stack buffer overflows and format string vulnerabilities through hands-on examples, reverse engineering techniques, and debugging tools. Learn essential skills for identifying and exploiting common software weaknesses.