Cantact - An Open Tool for Automotive Exploitation
Explore CANtact, an open-source tool for automotive network analysis. Learn to view, decode, and manipulate CAN bus traffic for reverse engineering and security testing of vehicle systems.
SGX Secure Enclaves in Practice - Security and Crypto Review
Explore Intel's SGX technology for secure remote computation, including its implementation, development environment, cryptographic aspects, and potential applications in secure storage and delegation.
Hacking the Wireless World with Software Defined Radio 2.0
Explore diverse wireless systems using software-defined radio. Learn to analyze, reverse engineer, and exploit RF signals for applications ranging from space probes to aircraft tracking and RFID systems.
We Can Still Crack You - General Unpacking Method for Android Packer - No Root
Discover a novel method for unpacking protected Android applications without root access. Learn to bypass anti-analysis techniques and reveal hidden code in packed apps.
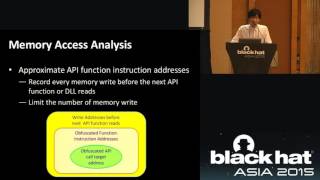
API Deobfuscator - Identifying Runtime-Obfuscated API Calls Via Memory Access Analysis
Unveils a resilient API deobfuscation technique using memory access analysis, overcoming limitations of pattern-based approaches to identify runtime-obfuscated API calls in malware and obfuscated code.
Even The LastPass Will Be Stolen, Deal With It!
Uncover vulnerabilities in LastPass password manager, including methods to steal master passwords, bypass 2FA, and access encrypted vaults, highlighting the importance of robust security measures.
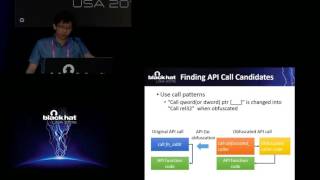
API Deobfuscator - Resolving Obfuscated API Functions in Modern Packers
Uncover obfuscated API functions in modern packers using memory access analysis and iterative run-until-API methods. Learn techniques to deobfuscate Themida 32/64 packed binaries for effective malware analysis.
Reverse Engineering Flash Memory for Fun and Benefit
Explore Flash memory reverse engineering techniques, including direct interaction, reprogramming, and file system analysis. Learn to handle meta information, deal with bad blocks, and leverage journaling file systems for deeper insights.
Feeding Gophers to Ghidra
Improve Golang binary analysis in Ghidra with Java-based scripts. Recover strings, functions, and types for efficient malware research and vulnerability detection.
Reverse Engineering a DOS PC FMV Game from 1994
Explore the intricacies of reverse engineering a 1994 DOS PC FMV game, uncovering techniques and challenges in dissecting vintage software architecture.
Advanced Return Address Discovery Using Context-Aware Machine Code Emulation
Explore advanced techniques for return address discovery using context-aware machine code emulation in cybersecurity research and exploitation.
When the Tables Turn
Explore cybersecurity tactics and strategies as experts discuss defensive techniques, threat analysis, and emerging trends in information security at this Black Hat conference session.
Break Me00 - The MoVfuscator - Turning mov into a Soul Crushing RE Nightmare
Explore a groundbreaking obfuscation technique that transforms code into a challenging reverse engineering puzzle using only 'mov' instructions.
Reverse Engineering the Wetware - Understanding Human Behavior to Improve Information Security
Explore behavioral sciences to enhance information security by understanding human behavior, overconfidence, and cognitive biases. Learn to design better systems and improve communication.
Exploring Emotet, An Elaborate Everyday Enigma
Dive into the intricacies of Emotet, the notorious and evolving malware family. Learn about its sophisticated operation, components, and the investigative techniques used to reverse engineer this digital threat.
Abusing Over-The-Air Client Provisioning
Uncovers vulnerabilities in major phone brands' network settings, allowing attackers to manipulate user data. Demonstrates attack flows and discusses vendor mitigations for these security risks.
Perfidious - Make PE Backdooring Great Again
Explore PErfidious, a Python tool for PE file manipulation and shellcode injection. Learn about its capabilities in bypassing endpoint detection systems and its potential as a modern PE file analysis library.
Car Hacking Made Easel
Demonstrating a systematic approach to reverse engineer and exploit car systems through CAN bus communication protocol analysis, packet spoofing, and payload crafting within a month-long prototype build.
How to Hack Radios - RF Physical Layers
Hands-on workshop exploring Software Defined Radio for reverse engineering wireless protocols in IoT devices. Learn digital radio fundamentals and practical techniques to examine proprietary modulations.
Even More Tamagotchis Were Harmed in the Making of This Presentation
Explore Tamagotchi hacking techniques, code execution, and microcontroller internals. Uncover virtual pet secrets and discover innovative projects using modified Tamagotchis in this engaging presentation.
Extracting an ELF From an ESP32
Detailed exploration of extracting ELF files from ESP32 firmware images, covering binary format analysis, conversion processes, and tools for reverse engineering IoT device firmware.