Banjo - An Android Disassembler for Binary Ninja
Explore Banjo, a Binary Ninja plugin for interactive Smali disassembly, enhancing Android app reverse engineering with features like references, graph mode, and Python 3 API.
Reversing SR IOV For Fun and Profit
Explore PCIe device reverse engineering, focusing on SR-IOV standard. Learn techniques to analyze vulnerabilities and extract valuable information from these interconnected components.
Ground Truth - 18 Vendors, 6000 Firmware Images, 2.7 Million Binaries, and a Flaw in the Linux-MIPS Stack
Presentation of data from analysis of 6000+ firmware images, revealing trends in software hardening and a critical flaw in Linux/MIPS stack affecting security across embedded devices.
Patchwerk - Kernel Patching for Fun and Profit
Explore techniques for patching and securing Linux kernels on IoT devices without source code. Learn to inspect, compile, and apply patches to vendor OEM kernels for vulnerability mitigation and reverse engineering.
Pages from a Sword-Maker's Notebook Part II
Explore covert intelligence gathering techniques, from anti-virus evasion to counter-intelligence, with practical code examples in Golang. Learn methodologies and technical solutions for long-term surveillance operations.
AFL-Unicorn - Fuzzing the 'Unfuzzable'
Explore afl-unicorn, a tool bridging manual research and AFL's automation for vulnerability discovery in complex systems, with practical workflow insights for various targets.
Cyborg Self Hacking
Explore cyborg self-hacking techniques, including implant parts, noise simulation, reverse engineering, and decoding methods. Learn about RTLSDR, waterfall diagrams, and oscilloscopes in this technical presentation.
Challenges on Reversing Layered Malware
Explora los desafíos de la ingeniería inversa de malware en capas, analizando técnicas avanzadas para descifrar y comprender el funcionamiento de software malicioso complejo.
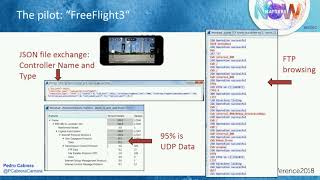
Parrot Drones Hijacking
Explore drone architecture, communication protocols, and reverse engineering techniques. Learn to assess security, develop new methodologies, and implement best practices for securing drone environments.
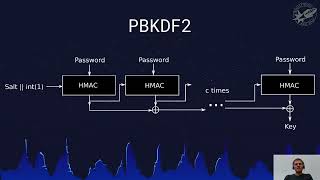
Practical Brute Force of Military Grade AES-1024
Analyse von Sicherheitslücken in der DataVault-Verschlüsselungssoftware für USB-Sticks und Festplatten. Aufdeckung schwerwiegender Mängel bei Schlüsselableitung und Verschlüsselung trotz starker Sicherheitsversprechen.
MTV Reboot - My Super Sweet 16-Bit Malware - MS-DOS Edition - TSR Remix
Deep-dive analysis of MS-DOS malware, exploring infection techniques, stealth mechanisms, and persistence methods. Highlights technical complexity and graphical displays in 16-bit DOS malware through reverse-engineering.
Reversing Web Assembly
Explore techniques for reversing Web Assembly (wasm) in this offensive security talk. Learn key strategies and tools for analyzing and understanding wasm code.
Hardware befreien - Briefbeschwerer, oder gehört die Hardware wirklich mir?
Entdecken Sie, wie Reverse Engineering und Community-Engagement Ihre Geräte von Herstellerabhängigkeit befreien können. Lernen Sie, wie jeder zur Nachhaltigkeit von Hardware beitragen und deren Lebensdauer verlängern kann.
Grand Pwning Unit - Accelerating Microarchitectural Attacks with the GPU
Explores how integrated GPUs can accelerate microarchitectural attacks, bypassing mitigations and compromising mobile browsers. Demonstrates novel reverse engineering techniques for GPU cache architecture.
SoK - The Art of War - Offensive Techniques in Binary Analysis
Comprehensive overview of binary analysis techniques for vulnerability detection, comparing approaches and discussing their effectiveness using a standardized framework and dataset.
All Your -Data-base Are Belong To Us
Explore vulnerability research in office applications through fuzzing, code review, and reverse-engineering. Learn to discover and exploit zero-days, with insights on binary exploitation for curious researchers.
Witchcraft Compiler Collection - Towards Self Aware Computer Programs
Explore innovative reverse engineering techniques to create self-aware binary code through relinking, binary reflection, and automated API prototyping, enhancing code reuse and debugging capabilities.
Augmenting Static Analysis Using Pintool - Ablation
Extracts runtime information to enhance static analysis, resolving virtual calls in C++ binaries and visually comparing samples for efficient vulnerability research and code auditing.
What's the DFIRence for ICS?
Explore digital forensics for industrial control systems, focusing on embedded devices in critical infrastructure. Learn data collection and analysis techniques for RTUs in electric substations.
Pindemonium - A DBI-Based Generic Unpacker for Windows Executable
Explore a generic unpacking algorithm for Windows executables using Dynamic Binary Instrumentation. Learn to detect and defeat popular packing techniques, reconstruct working PEs, and handle IAT obfuscation.
Keystone Engine - Next Generation Assembler Framework
Explore Keystone, a multi-architecture assembler engine with clean API, native support for various platforms, and bindings for multiple programming languages. Ideal for reverse engineering and security research.