
Breaking the IIoT - Hacking Industrial Control Gateways
Comprehensive exploration of security vulnerabilities in industrial control gateways, from protocol attacks to firmware reverse engineering, with live demonstrations on real devices.
Security Research on Mercedes-Benz - From Hardware to Car Control
Explore Mercedes-Benz car security research, from hardware analysis to gaining control. Learn about attack surfaces, reverse engineering, and cloud control in modern connected vehicles.
Emulating Samsung's Baseband for Security Testing
Explore Samsung baseband security through emulation, enabling scalable vulnerability research and debugging for cellular network protocols.
Breaking Through Another Side - Bypassing Firmware Security Boundaries from Embedded Controller
Reverse engineering Embedded Controller firmware to bypass Intel BIOS Guard on Lenovo Thinkpads, exploring hardware security boundaries and firmware update processes.
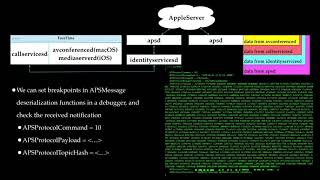
Towards Discovering Remote Code Execution Vulnerabilities in Apple FaceTime
Explore FaceTime's vulnerabilities through reverse engineering, focusing on call initialization, connection processes, and potential attack surfaces for remote code execution.
iOS Dual Booting Demystified
Explore iOS dual booting, secure boot process, and custom firmware loading. Learn reverse engineering techniques and system components for advanced iOS understanding.
Breaking Bad - Stealing Patient Data Through Medical Devices
Explore risks of connected healthcare devices, including attack surfaces, data vulnerabilities, and real-world case studies of medical IoT security breaches and their implications.
Deep Dive into ART - Android Runtime for Dynamic Binary Analysis
Explore Android Runtime's evolution, optimization techniques, and structure. Learn to analyze apps by modifying ART to extract real-time information and develop effective analysis techniques without code access.
Exploiting Android Messengers with WebRTC
Explore WebRTC vulnerabilities in Android messaging apps, their exploitation, and mitigation strategies. Learn about security research techniques and mobile application security.
HackIM CTF - Do's and Don'ts
Explore CTF competitions: learn security through challenges in web, crypto, reverse engineering, and more. Gain insights on dos and don'ts for successful participation in HackIM CTF.
The Art of Bootloader Unlocking - Exploiting Samsung Sboot
Explore Samsung bootloader security, uncovering hidden protocols and vulnerabilities. Learn about anti-tamper mechanisms, memory corruption, and techniques for unlocking Android devices.
SMS to Meterpreter - Fuzzing USB Modems
Explore innovative attacks on USB data modems, including fuzzing techniques and SMS payload execution. Learn about vulnerabilities, reverse engineering, and USB sniffing for offensive security research.
Python - The Wonder Woman of Embedded Device Reversing
Explore Python's power in embedded device reverse engineering, covering triage, scripting, analysis, and IDA integration for efficient vulnerability research.
Aiding Static Analysis - Discovering Vulnerabilities in Binary Targets through Knowledge Graph
Explore advanced techniques for vulnerability detection in binary targets using knowledge graphs, static analysis, and specialized tools like Binary Ninja and Kraken.
Pushing Security Left by Mutating Byte Code
Explore techniques for building secure software through bytecode mutation, including obfuscation, encryption, and cross-compilation to protect against reverse engineering and enhance product security.
Aviation Cybersecurity - Technology and Teamwork
Explore aviation cybersecurity challenges, vulnerabilities in aircraft systems, and industry efforts to manage risks through technology and partnerships.
Hunting Linux Malware for Fun and Flags
Explore Linux server malware analysis techniques, from basic artifact examination to advanced memory dumping and network capture, enhancing your cybersecurity skills.

The Future of RE - Dynamic Binary Visualization
Explore dynamic binary visualization for reverse engineering, enhancing analysis through innovative visual techniques and software tools like cantor.dust.
Reverse Engineering a Classic Video Game
Explore reverse engineering techniques using a classic 90s game as an example. Learn about file structures, compression, graphics, and audio while rebuilding the game in C#.
Reverse Engineering a Legacy Software in a Complex System - A Systems Engineering Approach
Explore a systems engineering approach to reverse engineer legacy software in complex systems, focusing on understanding development reasoning and creating roadmaps for incremental improvements.
Erays - Reverse Engineering Ethereum's Opaque Smart Contracts
Reverse engineering tool for Ethereum smart contracts, providing insights into code complexity, reuse, and linking contracts to public source code. Demonstrates applications in high-value wallets, arbitrage bots, and popular games.