When CAN CANT
Explore CAN bus vulnerabilities and CANT software for automotive security research. Learn error handling, selective attacks, and advanced techniques for vehicle hacking and defense.
Opening Closed Systems With GlitchKit
Explore GlitchKit, an open-source solution for fault injection in closed systems. Learn techniques to bypass firmware protection and extract secrets through hardware hacking and reverse engineering.

STOCHFUZZ - Sound and Cost-effective Fuzzing of Stripped Binaries by Incremental and Stochastic Rewriting
Explore innovative techniques for efficient fuzzing of stripped binaries, including incremental and stochastic rewriting, static writing, and delta debugging.
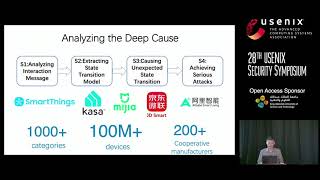
Discovering and Understanding the Security Hazards in the Interactions between IoT Devices, Mobile Apps, and Clouds on Smart Home Platforms
Exploring security vulnerabilities in smart home platforms through reverse engineering and phantom device testing, revealing unexpected state transitions and potential attacks.
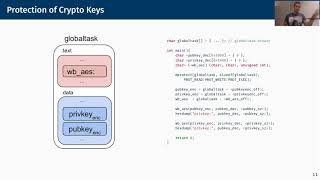
Unearthing the TrustedCore - A Critical Review on Huawei’s Trusted Execution Environment
Unveils critical security flaws in Huawei's TrustedCore, exposing vulnerabilities in trusted execution environments and demonstrating weaknesses in hardware-backed cryptography on mobile devices.
Lost in the Loader - The Many Faces of the Windows PE File Format
Explore Windows PE file format intricacies, parser differentials, and a custom language for modeling loaders. Learn analysis techniques to aid reverse-engineering tasks.
Reverse Engineering Compliance
Explore reverse engineering techniques applied to compliance standards, shifting from checkbox mentality to understanding the spirit of requirements for more effective security practices.
Bypassing NGAV for Fun and Profit
Explore methodologies to reverse engineer and bypass next-generation anti-virus (NGAV) models, focusing on adversary learning techniques and challenges in cybersecurity.
Hacking the DevOps Butler - From Nothing to Admin
Explore Jenkins vulnerabilities and exploitation techniques, focusing on two critical flaws that allow unauthenticated attackers to gain admin access and control entire infrastructures.
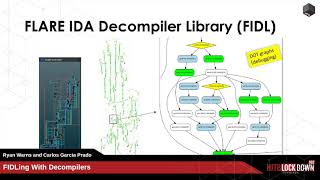
FIDLing with Decompilers
Explore decompilation basics, popular tools, and the Hex-Rays Decompiler. Learn about FIDL, a new library simplifying decompiler API usage, with practical examples and demos.
Secret Flaws of In-DRAM RowHammer Mitigations
Unveiling secret flaws in DRAM RowHammer mitigations, exploring Target Row Refresh implementation, and introducing TRRespass: a RowHammer fuzzer for creative hammering patterns to bypass protections.
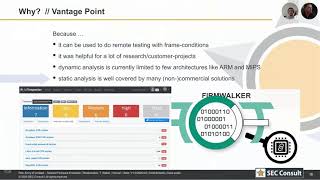
Army of Undead - Tailored Firmware Emulation
Explore automated firmware emulation techniques for embedded systems, covering root filesystem location, architecture identification, and emulation methods using open-source tools and scripts.
Analyzing Recent Evolutions in Malware Loaders
Análisis detallado de la evolución reciente de los cargadores de malware, sus técnicas de evasión y distribución, y métodos para detectarlos y analizarlos en entornos corporativos.
Reimplementing Local RPC in .Net
Reimplementing Windows RPC in .NET for privilege escalation, covering ALPC implementation, NDR parsing, and PowerShell integration. Includes bug discovery and tooling demonstration.
Faster, Wider, Greater - Modern Pentest Tricks
Explore modern pentesting techniques, tools, and procedures for efficient data processing and analysis. Learn about Jython, PyInstaller, CSVKit, Impacket, Frida, and GNU Parallel to enhance your security auditing skills.
Reverse Engineering Swift Applications
Exploring Swift app reverse engineering: class info extraction, Objective-C bridging, runtime manipulation, and function hooking for security professionals and pentesters.
Using the Observer Effect and Cyber Feng Shui - Jacob Torrey
Explore techniques for detecting system monitoring and creating secure environments. Learn about architectural "tells", physical unclonable functions, and strategies for evading analysis in computer systems.
Car Hacking - Practical Guide to Automotive Security
Practical guide to automotive security, focusing on CAN bus hacking. Learn to reverse-engineer packets, identify arbitration IDs, perform replay attacks, and explore hardware tools for vehicle network security.
Exploiting Zoom on MacOS
Exploración detallada de una vulnerabilidad de ejecución remota de código en el cliente Zoom para macOS, incluyendo técnicas de ingeniería inversa y explotación aplicables a otras aplicaciones.
Researching New Attack Interfaces on iOS and OSX
Exploración de nuevas interfaces de ataque en iOS y OSX, revelando vulnerabilidades del kernel y controladores mediante ingeniería inversa, análisis estático/dinámico y fuzzing mejorado.
Overcoming Fear - Reversing With Radare2
Comprehensive guide to reversing with Radare2, covering installation, basic commands, visual modes, configuration, and practical applications. Suitable for beginners and professionals in computer security.