Sleight of ARM- Demystifying Intel Houdini - Brian Hong - Ekoparty 2021- Hardware Hacking Space
Explore Intel's Houdini binary translator for running ARM on x86, its inner workings, security weaknesses, and potential exploits. Gain insights into cross-architecture execution and its implications for Android security.
Anatomy of a Gopher - Binary Analysis of Go Binaries - Alex Useche - Ekoparty Security Conference - 2020
Explore Go binary analysis for IoT and edge computing, covering Go assembler, tools, and language constructs to enhance reverse engineering skills.
Hackeando Aplicaciones móviles de ¿Seguridad?
Demostración de vulnerabilidades en aplicaciones móviles de seguridad mediante ingeniería inversa e instrumentación dinámica, con casos de estudio reales de applockers, control parental y anti-robo.
All Your GPS Trackers Belong to Us - C. Kasmi, P. Barre - Hack in Paris - 2019
Explore security vulnerabilities in GPS trackers, including traffic analysis, SMS configuration exploitation, protocol reverse engineering, and GPS signal spoofing. Learn about privacy risks and potential attack scenarios.
From Printed Circuit Boards to Exploits: Pwning IoT Devices Like a Boss - Damien Cauquil - Hack in Paris - 2018
Explore hardware hacking of a Bluetooth smartlock, from circuit board analysis to exploit development, covering electronics basics, reverse engineering, and mobile app vulnerabilities.
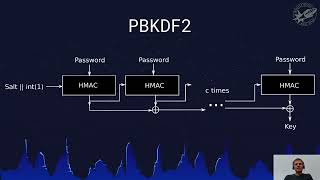
Practical Brute Force of Military Grade AES-1024 - Sylvain Pelissier, Boi Sletterink
Análisis de vulnerabilidades en el software de cifrado DataVault, revelando fallas en la derivación de claves y encriptación que comprometen la seguridad de productos de almacenamiento de Sony, SanDisk y Lexar.
Case Studies in Embedded VR - Silvio Cesare - Ekoparty Security Conference - 2022
Explore cutting-edge techniques in embedded VR security, focusing on router vulnerabilities, reverse engineering, and exploit development through real-world case studies.
Modern Secure Boot Attacks - Alex Matrosov - Ekoparty Security Conference - 2019
Explore modern Secure Boot attacks, focusing on bypassing Intel Boot Guard in enterprise systems. Learn about hardware Root of Trust, Embedded Controllers, and UEFI Firmware vulnerabilities.

The Advanced Threats Evolution- REsearchers Arm Race - Alex Matrosov - Ekoparty Security Conference - 2019
Explore the evolution of advanced threats and defensive software, focusing on persistent methods at hardware and firmware levels. Gain insights into modern security gaps and potential solutions.
Exploitation of a Hardened MSP430-Based Device - Braden Thomas - Ekoparty Security Conference - 2014
Reverse-engineering and exploiting a hardened MSP430 device: techniques for firmware extraction, analysis, and data retrieval from RAM, with focus on overcoming JTAG security measures.
Reversing Web Applications
Explore web application reverse engineering techniques, from information gathering to active testing, to understand behavior, analyze code, and improve security assessments.
Hacking .NET Applications - The Black Arts
Explore techniques for hacking .NET applications, including malware analysis, code review, and penetration testing. Learn to build keygens, cracks, and overcome security measures in .NET environments.
Introduction to Reverse Engineering
Explore techniques used by crackers to bypass security, access firmware, and find vulnerabilities in hardware and software. Learn to protect your products from reverse engineering.
OpenOCD - Beyond Simple Software Debugging
Explore advanced OpenOCD applications beyond debugging, including boundary scan testing, hardware troubleshooting, and reverse engineering techniques for embedded systems and firmware.
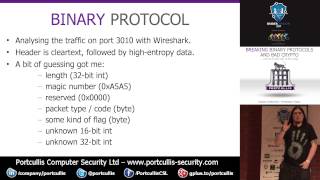
Breaking Binary Protocols and Bad Crypto
Explore reverse-engineering techniques for binary protocols and cryptography, focusing on methodologies to uncover vulnerabilities in network devices through real-world examples.
Owning the Smart Home with Logitech Harmony Hub
Explore reverse engineering of Logitech's Harmony smart home hub, uncovering vulnerabilities and discussing their implications for device security and potential exploitation.
Detecting Access Token Manipulation
Demystifying Windows access token manipulation attacks and providing effective detection strategies for defensive practitioners in enterprise environments.
Finding New Bluetooth Low Energy Exploits via Reverse Engineering Multiple Vendors' Firmwares
Explore Bluetooth Low Energy vulnerabilities through firmware reverse engineering, uncovering remote code execution exploits at the protocol's lowest levels without authentication or pairing.
Fatal Fury on ESP32 - Time to Release Hardware Exploits
Methodical exploration of defeating ESP32 security features using low-cost hardware techniques, including voltage glitching and analog side-channels, with implications for IoT device security.

Exploiting Qualcomm WLAN and Modem Over The Air
Explore Qualcomm WLAN and Modem vulnerabilities, focusing on firmware exploitation, isolation breaches, and over-the-air control techniques. Gain insights into real-time debugging and mitigation strategies.
BluePill - Neutralizing Anti-Analysis Behavior in Malware Dissection
Explore BluePill, a customizable tool for neutralizing anti-analysis techniques in malware. Learn how it defeats evasive samples and executable protectors, enhancing malware dissection capabilities.