The Long Journey to a Multi-Architecture Disassembler
Explore multi-architecture disassembly techniques, from intuitive strategies to advanced concepts like non-returning calls, type libraries, and identifying library routines.
All Software is Open Source - An Introduction to Reverse Engineering
Explore reverse engineering fundamentals, tools, and strategies for information security. Learn legal aspects, safe practices, and real-world applications through war stories and CTF challenges.
OO RE with HexraysCodeXplorer
Explore object-oriented reverse engineering techniques for modern malware analysis, focusing on C++ code reconstruction and tools like HexRaysCodeXplorer for tackling complex malware frameworks.
Introduction to Reversing and Pwning
Explore reverse engineering and exploitation techniques, covering low-level programming, memory vulnerabilities, and essential tools for cybersecurity enthusiasts and professionals.
High-Assurance Crypto Software
Exploración de criptografía de alta seguridad: ataques de tiempo, software de tiempo constante y herramientas de ingeniería inversa para verificar implementaciones criptográficas.
Intel Management Engine Deep Dive
Explora el Intel Management Engine: arquitectura, firmware, seguridad y desarrollo de un emulador. Análisis profundo de su funcionamiento interno y posibilidades de reemplazo de código abierto.
Messenger Hacking- Remotely Compromising an iPhone through iMessage - Deutsche Übersetzung
Detaillierte Einblicke in die Ausnutzung einer iMessage-Sicherheitslücke zur Kompromittierung von iPhones ohne Nutzerinteraktion. Beleuchtet Techniken, Gegenmaßnahmen und Empfehlungen für verbesserte mobile Sicherheit.
Cyber Necromancy - Reverse Engineering Dead Protocols - DefCamp - 2014
Explore reverse engineering of defunct protocols, focusing on Sony's Dynamic Network Authentication. Learn techniques for packet analysis, cryptography, and overcoming challenges in reviving obsolete online systems.
Investigating Windows Graphics Vulnerabilities - A Reverse Engineering & Fuzzing Story - DefCamp - 2019
Explore Windows graphics vulnerabilities through reverse engineering and fuzzing techniques, focusing on GDI components, patch analysis, EMF format, and effective fuzzing strategies.
Reversing a Polymorphic File-Infecting Ransomware - DefCamp - 2016
Explore techniques for reversing polymorphic file-infecting ransomware, covering debugging tools, malware types, and decryption methods in this hands-on cybersecurity talk from DefCamp 2016.
The Three Billion Dollar App
Explore messaging app vulnerabilities, reverse engineering techniques, and security implications in this in-depth analysis of a high-profile data breach and exploit delivery.
Bluetooth - Does It Spark Joy?
Explore Bluetooth firmware reverse engineering, security insights, and bug-finding techniques in this deep dive into wireless technology vulnerabilities.
IoT Processor and Binary Breakdown - The Good the Bad and the Ugly
Explore IoT processor architecture, binary analysis, and firmware vulnerabilities. Gain insights into hardware, Linux deployment, and virtualization for secure IoT development.
Mobile App Security Fails and How To Survive Them
Explore mobile app security vulnerabilities and defense strategies, covering platform misuse, insecure communication, authentication flaws, and real-world case studies for improved protection.
When Virtual Hell Freezes Over - Reversing C++ Code
Explore advanced C++ code reversing techniques, focusing on dynamic object creation, vtables, and multiple inheritance. Learn automated methods for efficient analysis.
Reverse Engineering a Digital Two-Way Radio
Explore digital two-way radio reverse engineering, covering bootloader dumps, firmware patching, and USB analysis for the Tytera MD380 device.
The Challenges of Designing a Secure Encrypted Hard Drive
Explore the complexities of designing secure encrypted hard drives, covering security models, components, encryption methods, potential vulnerabilities, and protective measures against various attack vectors.
HARES - Hardened Anti Reverse Engineering System
Explore HARES, an advanced anti-reverse engineering system. Learn about TLB splitting, program verification, and security implications for Windows kernel protection.
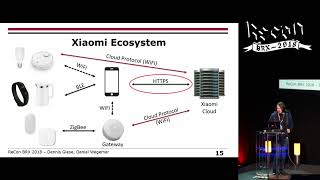
Reversing IoT - Xiaomi Ecosystem
Explore Xiaomi IoT ecosystem security, firmware extraction, and cloud communication. Learn to modify devices, implement new functions, and gain independence from proprietary cloud services.
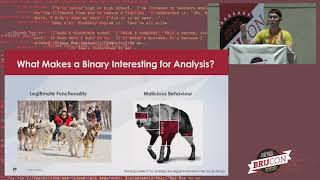
Chasing the White Whale of Malware
Exploring techniques to identify and analyze operational technology malware, focusing on unique challenges and methods for filtering OT binaries without advanced reverse engineering skills.
Automating Binary Analysis with Ghidra's P-Code
Explore automated binary analysis using Ghidra's P-Code, an intermediate language that enables architecture-independent scripting for reverse engineering and vulnerability research.