The Mysterious Life of an Exception
Explore exception handling mechanics, from throw to catch, uncovering runtime interactions, DWARF unwinding, and LSDA. Introduces a Binary Ninja plugin for extracting exception info from binaries.
Under the Hood of Wslink Multilayered Virtual Machine
Detailed analysis of Wslink loader's advanced virtual machine obfuscator, exploring its techniques and demonstrating a semiautomatic deobfuscation approach using symbolic execution and concrete value treatment.
Pulling MikroTik into the Limelight
Explore MikroTik's RouterOS internals, including IPC protocols, message formats, and cryptography. Learn about a new remote jailbreak and gain insights to accelerate RouterOS security research.
Hacking Toshiba Laptops
Unveiling Toshiba laptop vulnerabilities: BIOS password recovery exploitation and EC firmware signing key extraction, enabling stealth rootkit implantation. Implications for newer models discussed.
Neurosurgery for Industrial Routers - Security of Sarian OS
Explore vulnerabilities in industrial routers, focusing on Digi WR21 and Sarian OS. Uncover internal workings, network protocols, and security features of critical infrastructure devices.
Linux Vulnerabilities, Windows Exploits - Escalating Privileges with WSL
Explore WSL vulnerabilities and Windows kernel exploitation techniques. Learn about reverse engineering, syscall manipulation, and bypassing modern anti-exploitation defenses to achieve privilege escalation.
Decompiler Internals - Microcode
Explore the intermediate language used in Hex-Rays Decompiler, its simplicity and power in representing programs, and plans for publication and programmatic access.
When Virtual Hell Freezes Over - Reversing C++ Code
Automated techniques for reversing complex C++ code, focusing on rebuilding inheritance, identifying templates, and tracing program flow to simplify the reverse engineering process.
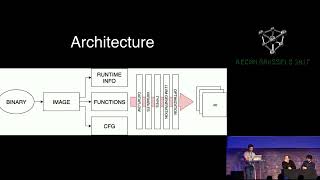
Analyzing iOS Apps - Road from AppStore to Security Analysis Report
Toolset for detecting vulnerabilities in iOS apps: download and decrypt, decompile, statically analyze, and present results. Focuses on high-level semantics reconstruction and common mobile app security flaws.
Hackable Security Modules - Reversing and Exploiting a FIPS 140-2 Lvl 3 HSM Firmware
Exploring vulnerabilities in Hardware Security Modules (HSMs) through firmware analysis and reverse engineering of the TMS320C64x DSP architecture, with focus on the Utimaco SecurityServer.
Recon 2017 Brussels - r2m2 by Guillaume "guedou" Valadon
Presentation on r2m2, a radare2 plugin leveraging miasm2 for reversing rare CPU architectures. Demonstrates integration of powerful reverse engineering tools and simplifies implementation of new architectures.
A Little Less Conversation, A Little More ActionScript
Techniques for in-depth reverse engineering of Flash, mapping ActionScript to undocumented counterparts, and analyzing vulnerabilities in Adobe Flash Player for improved exploit research.
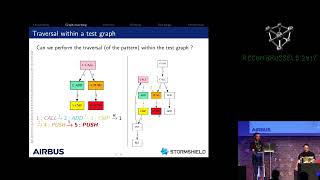
GRAP - Define and Match Graph Patterns Within Binaries
Herramienta para detectar patrones en código binario mediante coincidencia de grafos. Permite definir firmas personalizadas para identificar variantes de malware y extraer información valiosa.
Burned in AshesBaseband Fairy Tale Stories
Exploring remote protocols in Baseband, reverse engineering methodologies, and bug discovery in mobile communication systems.
The Road to Qualcomm Trust Zone Apps Fuzzing
Explore Trusted Execution Environment vulnerabilities in Qualcomm's TEE, reverse engineering techniques, and fuzzing methods for TrustZone apps in mobile device security research.
Attacking Hexagon Security Analysis of Qualcomm's ADSP
Explore Qualcomm's Hexagon ADSP security, architecture, and exploitation techniques. Learn reverse engineering methodologies for proprietary systems and mitigations bypass on Android devices.
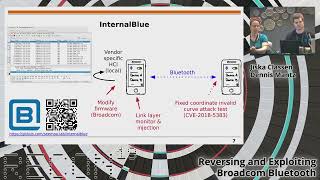
Reversing and Exploiting Broadcom Bluetooth
Insights into reverse engineering Broadcom Bluetooth firmware, including InternalBlue framework, patching techniques, and discovered vulnerabilities CVE-2018-19860 and CVE-2019-6994.
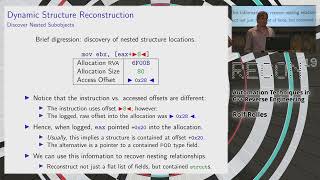
Automation Techniques in C++ Reverse Engineering
Explore automated dynamic analysis techniques for C++ reverse engineering, focusing on structure usage, function argument types, and inheritance relationships through DLL injection.
The Path to the Payload - Android Edition
Uncover sophisticated Android malware techniques: obfuscation, anti-analysis, encrypted configs, and fake commands. Learn to reverse-engineer and reveal hidden payloads in this advanced security deep-dive.
The ROM Matrix Revolution - Unscrambling Bits
Explore ROM encryption vulnerabilities and decryption techniques using visual analysis and software tools, with insights applicable to various chip families.
SiliVaccine - North Korea's Weapon of Mass Detection
Explore North Korea's SiliVaccine, a secretive national antivirus solution. Uncover its architecture, origins, and peculiarities through reverse engineering, revealing insights into DPRK's closed digital landscape.