Zooming in on Zero Clicks Exploits
Dive into Zoom's security analysis, exploring reverse engineering challenges, large system understanding, and fuzzing techniques for non-relocatable binaries in video conferencing software.
Instrumenting System Applications on Android Images
Instrumenting Android system apps on stock images using Frida for dynamic analysis. Explores various approaches, their limitations, and a successful method for analyzing Google Play Protect Services.
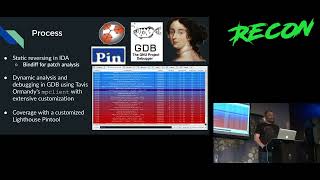
Reverse Engineering Windows Defender Part II
Deep dive into Windows Defender's binary emulator, exploring its internals, virtual environment, and integration with antivirus features. Gain insights on reverse engineering techniques for advanced malware analysis.
Breath of the RF Field
Explore Amiibo technology, reverse engineering, and NFC protocol vulnerabilities in Nintendo consoles using software-defined radio and a custom simulator for security research.
Meet Salinas - The First Ever SMS-Commanded Car Infotainment RAT
Discover how researchers created the first SMS-controlled malware for car infotainment systems, exploring vulnerabilities and potential threats in modern vehicle technology.
Pwning Intel PIN
Exploring vulnerabilities in Intel PIN's dynamic binary instrumentation framework, challenging assumptions of isolation and stealthiness, and demonstrating potential security risks in instrumented programs.
Building a Damned Good Watch
Cloning a calculator watch with added radio capabilities for Morse code transmission, frequency detection, and remote control signal replication. Includes practical insights and open-source code.
Discovering the iOS Instruments Server
Reverse-engineering of iOS privileged server providing sensitive data to Apple's debugging tools. Explores techniques used to uncover and analyze this critical system component.
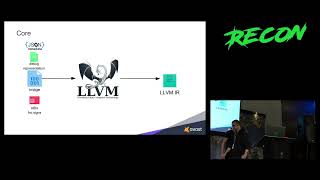
An Open-Source Machine-Code Decompiler
Explore RetDec, an open-source machine-code decompiler for analyzing binary applications. Learn about its components, applications in reverse engineering, and real-world examples demonstrated by Avast developers.
Malware Analysis and Automation using Binary Ninja
Explore malware analysis automation using Binary Ninja platform. Learn to adapt quickly to evolving threats, perform basic analysis, and utilize API for configuration data extraction from real-world samples.
Reverse Engineering of Blockchain Smart Contracts
Explore reverse engineering of blockchain smart contracts, focusing on Ethereum, Neo, and EOS platforms. Learn about virtual machines, assembly languages, and tools for security analysis.
Keeping Your Tools Safe IDA
Explore techniques for safeguarding IDA tools and enhancing reverse engineering security in this concise presentation from REcon Brussels 2017.
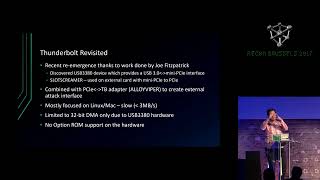
Getting Physical with USB Type-C - Windows 10 RAM Forensics and UEFI Attacks
Explore embedded microcontrollers in modern devices, focusing on the Surface Aggregator Module. Learn about security, firmware updates, and potential hardware implants in this deep dive into low-level system architecture.
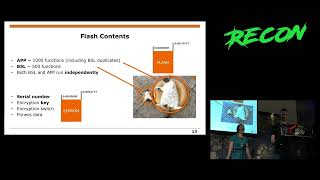
Create Your Own Fitness Tracker Firmware
Reverse-engineering Fitbit Flex firmware: exploring encryption, BLE communication, and protocols. Demonstrating wireless custom firmware flashing and enabling raw accelerometer readings.
Sum Total of ISA Knowledge - Analyzing Your Binary Analysis Tools
Explore techniques to measure and verify architecture support in binary analysis tools, enhancing firmware reverse engineering through selective application of dynamic analysis methods.
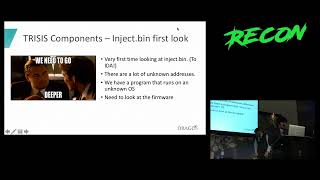
Analyzing TRISIS - The First Safety Instrumented System Malware
Detailed analysis of TRISIS malware targeting safety systems, blending hardware and software reverse engineering. Explores PowerPC payloads, Triconex firmware, and discusses implications for industrial control security.
Recovering Software Architecture from Embedded Binaries
Discover techniques for recovering software architecture from large binaries using CodeCut and local function affinity, with applications in automated module-to-module call graphs and section naming.
Sandbagility - Reverse Engineering Framework for Windows Dynamic Analysis
Hybrid framework for Windows malware analysis combining dynamic and sandbox approaches. Offers stealthy, adaptive solution to reduce analysis time, demonstrated with WannaCry case study.
Rattle - An Ethereum EVM Binary Analysis Framework
Explore Rattle, an innovative framework for analyzing Ethereum smart contracts, enhancing auditability and security in blockchain interactions through advanced binary analysis techniques.
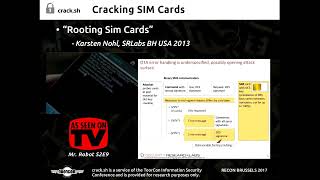
Legacy Crypto Never Dies
Explore legacy cryptography vulnerabilities and the crack.sh API for breaking DES-based protocols, with insights from David Hulton's research on widely used services still relying on outdated encryption.
Under the Hood of Wslink Multilayered Virtual Machine
Análisis detallado de la máquina virtual multicapa Wslink, explorando técnicas de ofuscación avanzadas y presentando un enfoque semiautomático para desobfuscar el malware de forma eficiente.