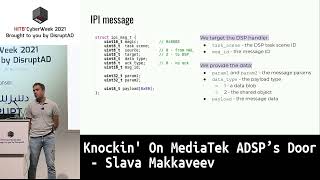
Knockin' On MediaTek ADSP's Door
Reverse engineering MediaTek's audio DSP firmware reveals vulnerabilities in RTOS and Android HAL, potentially enabling local privilege escalation and eavesdropping on user conversations.
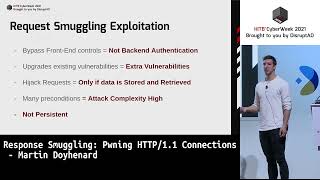
Response Smuggling - Pwning HTTP/1.1 Connections
Explore advanced HTTP response smuggling techniques, including protocol vulnerabilities, session hijacking, and response scripting, with real-world demonstrations on major ERP systems.
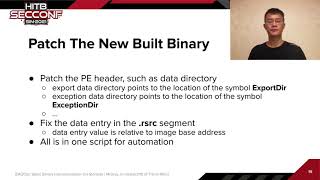
IDA2Obj - Static Binary Instrumentation on Steroids
Explore static binary instrumentation with IDA2Obj, a tool for dumping object files from executables. Learn implementation, challenges, and integration with fuzzing engines for efficient code coverage collection.
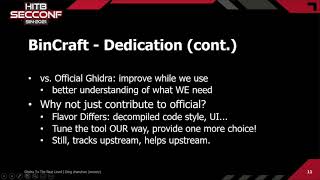
Taking Ghidra to the Next Level
Enhancing Ghidra: BinCraft's modernization efforts, improved decompilation, and integration of advanced techniques like GraalVM for a more powerful reverse engineering tool.

Is Attestation All We Need? Fooling Apple's AppAttest API
Exploración detallada de la API AppAttest de Apple, sus vulnerabilidades y limitaciones como solución anti-manipulación, con ejemplos de implementaciones débiles y escenarios de bypass.
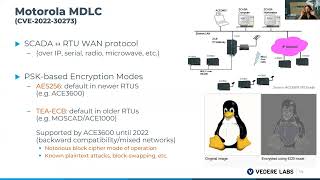
ICEFALL - Revisiting A Decade Of OT Insecure-By-Design Practices
Revisiting insecure-by-design practices in OT devices, highlighting persistent security issues across industries and critical infrastructure, with technical deep-dives and implications for risk management.
WhyMI So Sexy? WMI Attacks, Realtime Defense & Advanced Forensic Analysis
Explore WMI attacks, defense strategies, and forensic analysis techniques to enhance cybersecurity skills and protect against sophisticated threats in Windows environments.
Virtual Breakpoints for x86/64
Explore virtual breakpoints for x86/64 architectures, enhancing debugging capabilities and gaining deeper insights into system behavior and software execution.
Malware Analysis - Red Team Edition
Explore advanced malware analysis techniques from a Red Team perspective, enhancing your cybersecurity skills and understanding of malicious software behavior.
CTF or WTF?
Compara desafíos CTF con pruebas de penetración reales, explorando similitudes y diferencias en habilidades, escenarios y lecciones aprendidas para profesionales de ciberseguridad.
Hacking K-12 School Software in a Time of Remote Learning
Análisis de vulnerabilidades en software educativo durante la pandemia, explorando ataques potenciales y sus implicaciones para la seguridad de dispositivos escolares y domésticos.
Reversing Android Malware for the Smart and Lazy
Learn efficient techniques for analyzing Android malware, focusing on smart and time-saving approaches to reverse engineering and threat assessment.
Reversing Android Malware for the Smart and Lazy
Learn efficient techniques for analyzing Android malware, focusing on smart and time-saving approaches to reverse engineering and threat assessment.
Dynamic Data Resolver IDA Plugin - Extending IDA with Dynamic Data
Extending IDA with Dynamic Data Resolver plugin for improved malware analysis. Instrumenting binaries using DynamoRIO to resolve dynamic values, find jump locations, and patch anti-analysis functions.
Applying DevOps Principles for Better Malware Analysis
Leveraging DevOps principles to streamline malware analysis, automate lab setup, and enhance collaboration among security researchers for more efficient threat detection and response.
CANtact - An Open Tool for Automotive Exploitation
Explore CANtact, an open-source tool for automotive network analysis. Learn to view, decode, and manipulate CAN traffic for reverse engineering and security testing of vehicle systems.
xRAT - Monitoring Chinese Interests Abroad With Mobile Surveillance-ware
Explore mobile surveillance-ware xRAT, used for monitoring Chinese interests abroad. Learn about threat detection, reverse engineering, and emerging mobile security challenges.
Beyond AlphaGolang
Exploring advanced techniques for reverse engineering Golang binaries, leveraging AlphaGolang to automate malware analysis, and introducing new approaches for hunting and clustering Go-based threats.
Researching the Unisoc Baseband
Exploring Unisoc baseband security: reverse-engineering and fuzzing LTE protocol stack to uncover vulnerabilities in budget smartphone chipsets, disrupting radio communication.
Reversing an M32C Firmware - Lessons Learned from Playing with an Uncommon Architecture
Explore techniques for reversing firmware on unfamiliar architectures, focusing on M32C. Learn about interrupt handlers, special registers, and flash handling in embedded systems.
Reverse Engineering of Black Box Binaries with Symbolic and Concolic Execution Technique
Explore symbolic and concolic execution techniques to simplify reverse engineering of complex binaries. Learn to use the angr framework for efficient crackme solving and deobfuscation.