Cutting Edge - Microsoft Browser Security — From People Who Owned It
Deep dive into Microsoft Edge security architecture, exploring sandbox initialization, browser broker implementation, and renderer security isolation.
Devils Are in the File Descriptors - It Is Time To Catch Them All
Explore vulnerabilities in Linux kernel file descriptor operations, focusing on high-risk scenarios in exporting and importing, and learn to identify and address these security concerns.
EBPF ELFs JMPing Through the Windows
Explore eBPF for Windows: capabilities, security model, design, and attack surface. Uncover vulnerabilities, witness fuzzing demos, and discuss exploitation challenges in Windows Protected Process.
Unix Domain Socket - A Hidden Door Leading to Privilege Escalation in the Android Ecosystem
Explore Unix domain socket vulnerabilities in Android, revealing potential privilege escalation risks and security implications for third-party applications and vendor implementations.
Windows Kernel Graphics Driver Attack Surface
Explore the attack surface of Windows graphics drivers, including exposed ioctl's, driver internals, and security implications for researchers and developers.
Understanding TOCTTOU in the Windows Kernel Font Scaler Engine
Explore TOCTTOU vulnerabilities in Windows Kernel Font Scaler Engine, covering basic double fetch issues, stealthy design flaws, and their impact on system security. Learn about font file manipulation and exploit techniques.
Counterfeiting the Pipes with FakeNet 2.0
Explore network simulation for malware analysis using FakeNet 2.0. Learn to mimic protocols, configure settings, and capture network signatures efficiently in this hands-on workshop.
Social Engineering the Windows Kernel - Finding and Exploiting Token Handling Vulnerabilities
Explore Windows kernel token handling vulnerabilities, learn to identify and exploit them for privilege escalation, and understand patterns for conducting security reviews.

The Return of Stack Overflows in the Linux Kernel
Exploiting Linux kernel vulnerabilities: techniques for bypassing security controls, leveraging nftables bugs, and achieving code execution. Includes mitigation strategies and a novel per-softirq stack randomization implementation.
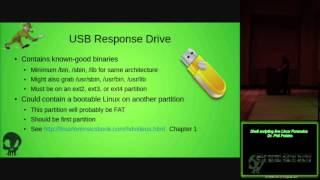
Shell Scripting Live Linux Forensics
Learn shell scripting for live Linux forensics, covering USB response drives, mounting binaries, network data transfer, log handling, and automated data collection for effective system analysis.
Future C++1x Proposals
Explore upcoming C++ features, including concepts, transactions, and concurrency enhancements, with insights on compiler implementation status and future language extensions.
A Newbie's Talk On Mobile Dangers Through The Looking Glass
Explore vulnerabilities in rooted Android devices and potential attacks using Raspberry Pi and USB-OTG accessories. Discusses programmatic rooting, charging port risks, and past iOS vulnerabilities.
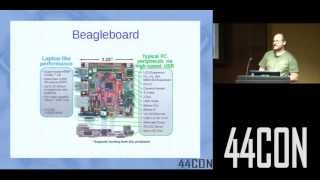
Hacking and Forensics on the Go
Explore mobile hacking and forensics techniques using BeagleBoard. Learn platform selection, OS building, compilation methods, and hardware accessories for on-the-go security operations.
Exploiting Linux Capabilities
Explore Linux capabilities exploitation techniques, enhancing your understanding of system security vulnerabilities and potential attack vectors in Unix-like environments.

Locking and Concurrency Control
Explore database locking, concurrency control, and data integrity in RDBMS. Learn about locks, MVCC, deadlocks, transactions, and isolation levels, with practical examples using MySQL 5.6.
Breaking BHAD - Abusing Belkin Home Automation Devices
Exploración de vulnerabilidades en dispositivos de automatización del hogar Belkin WeMo, revelando fallas de seguridad y demostrando ataques potenciales en la infraestructura IoT.

The Linux Kernel Hidden Inside Windows 10
Explore the Linux kernel in Windows 10, its implementation, security implications, and potential vulnerabilities. Learn about system calls, process management, and attack surfaces in this unique OS integration.
Measuring Adversary Costs to Exploit Commercial Software
Quantitative analysis of software security across platforms, revealing surprising insights for informed decision-making in product selection and vulnerability assessment.
Exploiting IPC With New Desynchronization Primitives
Exploración de vulnerabilidades críticas en SAP, demostrando técnicas avanzadas de explotación HTTP y desincronización para comprometer sistemas empresariales. Incluye demostraciones prácticas y análisis de impacto en la seguridad global.
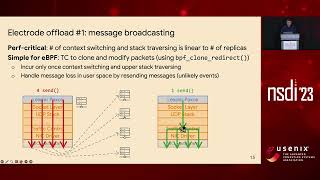
Electrode - Accelerating Distributed Protocols with eBPF
Accelerating distributed protocols using eBPF-based optimizations to improve performance by reducing user-kernel crossings and networking stack traversal, demonstrated with significant throughput and latency improvements in Multi-Paxos.
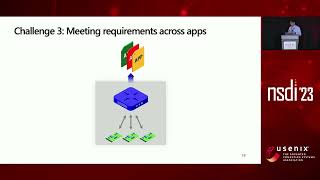
ExoPlane - An Operating System for On-Rack Switch Resource Augmentation
Innovative operating system for augmenting programmable switches with additional hardware, enabling concurrent stateful applications in network computing. Addresses resource limitations and offers scalable, low-latency solutions.