Finding Functions from Export Directory and Using Seeds for API Checksums - Part 6
Explore Lockbit's runtime-linking techniques, including EXPORT_DIRECTORY usage and DLL name seed for API checksum computation. Learn to debug and find APIs efficiently.
Walking the PEB, Enhancing IDA's Output with Structures, and Unlocking Runtime-Linking - Lecture 4
Explore PEB usage in malware, learn runtime DLL location techniques, and enhance IDA analysis with custom structures for improved reverse engineering.
Building a Canarytoken to Monitor Windows Process Execution - Track 2
Explore building Canarytokens to monitor Windows process execution, creating alerts for unexpected commands and strengthening defense against potential attacks.

Lockbit's DLL Name Seeding Technique for API Hashing - Part 5
Explore Lockbit's runtime-linking technique, focusing on DLL name usage for API hashing seed creation and its impact on reverse engineering efforts.
Windows Agentless C2 - Abusing the MDM Client Stack
Unveils innovative research on exploiting Windows MDM stack for agentless C2 systems. Explores vulnerabilities, custom C2 server creation, and remote device control techniques, inspiring new defensive strategies.
Practical Exploitation of Registry Vulnerabilities in the Windows Kernel
Explore practical exploitation techniques for Windows kernel registry vulnerabilities, enhancing your understanding of system security and potential attack vectors.
All About RPC, LRPC, ALPC, and LPC in Your PC
Comprehensive exploration of Windows inter-process communication mechanisms, including RPC, LRPC, ALPC, and LPC, detailing their architecture, security implications, and practical applications.
A View into ALPC-RPC - Advanced Local Procedure Call and Remote Procedure Call
Explore ALPC-RPC in Windows, including core structures, API, and vulnerability research. Learn about UAC bypass and Local Privilege Escalation discovered during the investigation.
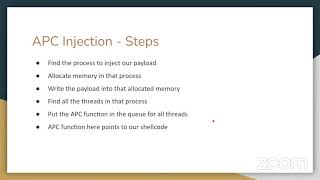
Advanced Process Injection Techniques
Hands-on workshop exploring APT tactics for privilege escalation and persistence. Learn to develop stealthy implants through 7 labs on Windows process injection techniques.
Hypervisors in Your Toolbox - Monitoring and Controlling System Events with HyperPlatform
Explore HyperPlatform, a thin hypervisor for Windows, enabling flexible handling of system events and rapid implementation of hypervisor-based tools with high compatibility and efficiency using Intel VT-x technology.
Indicators of Compromise - From Malware Analysis to Eradication
Explore malware analysis techniques, from detection to eradication, using free tools. Learn to identify indicators of compromise and effectively remove threats from enterprise networks.
Battle of Windows Service - A Silver Bullet to Discover File Privilege Escalation Bugs Automatically
Discover file privilege escalation bugs automatically in Windows services using Advanced Local Procedure Call analysis and process monitoring techniques for enhanced system security.
Counterfeiting the Pipes with FakeNet 2.0
Explore network simulation for malware analysis using FakeNet 2.0. Learn to mimic protocols, configure settings, and capture network signatures efficiently in this hands-on workshop.
Counterfeiting the Pipes with FakeNet 2.0 - Part 2
Learn to simulate networks for malware analysis using FakeNet 2.0. Capture network signatures, mimic protocols, and defeat malware through hands-on challenges with real-world samples.
The Sandbox Roulette - Are You Ready For The Gamble?
Explore application sandbox vulnerabilities and evasion techniques through a "Sandbox Roulette" demonstration, comparing various commercial solutions and their effectiveness against different exploit vectors.

Internals of Exceptions
Explore internal exception mechanisms in Windows, C++, and C#, from low-level details to high-level constructs. Gain insights into advanced exception handling techniques and CLR implementation.
Indirect Syscalls: A Journey From High to Low
Dive into the mechanics of system calls, exploring both direct and indirect implementations while understanding their journey from high-level to low-level programming concepts and security implications.
Kernel Games: The Ballad of Offense and Defense in Rootkit Methodologies
Dive into advanced kernel rootkit techniques for red team operations and defense strategies, covering stealthy persistence, EDR evasion, and practical detection methods with hands-on demos.