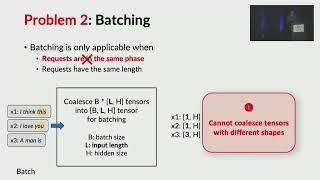
Orca - A Distributed Serving System for Transformer-Based Generative Models
Explore Orca, a distributed serving system for transformer-based generative models, featuring iteration-level scheduling and selective batching to enhance performance and efficiency in large-scale language model inference.
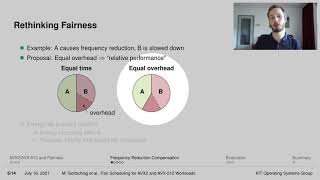
Fair Scheduling for AVX2 and AVX-512 Workloads
Explore fair CPU scheduling for AVX2 and AVX-512 workloads, addressing power-limited CPUs and frequency reduction impacts. Learn techniques to improve performance isolation and fairness in multi-task environments.
Whitelisting LD PRELOAD for Fun and No Profit
Explore LD_PRELOAD process injection, its audit system, and whitelisting challenges. Learn about built-in protection vs. bolt-on solutions for Linux security.
EBPF - The Next Power Tool of SREs
Explore eBPF, a revolutionary Linux kernel technology for infrastructure observation and protection. Learn its capabilities, use cases, and implementation for enhanced system reliability and security.
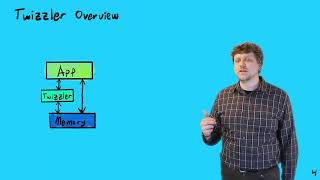
Twizzler - A Data-Centric OS for Non-Volatile Memory
Explore Twizzler, an innovative OS redesign for non-volatile memory, offering efficient data persistence, simplified programming, and improved performance over traditional systems.
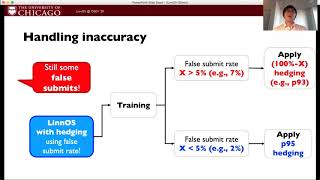
LinnOS - Predictability on Unpredictable Flash Storage with a Light Neural Network
Explore LinnOS, an OS using neural networks to predict SSD performance, enhancing storage application efficiency and outperforming industrial mechanisms with minimal overhead.
Latency Distributions and Micro-Benchmarking to Identify and Characterize Kernel Hotspots
Explore kernel hotspots using latency distributions and micro-benchmarking. Learn techniques to identify and address OS scale limits for improved system performance on bare metal hardware.
A Titan M Odyssey
Explore Google's Titan M chip: its architecture, security features, and potential vulnerabilities through reverse engineering and dynamic analysis techniques.
Achieving Linux Kernel Code Execution Through a Malicious USB Device
Explore Linux kernel exploitation via malicious USB devices, focusing on CVE-2016-2384 vulnerability. Learn about USB-based attacks, payload delivery, and mitigation strategies.
Man in the Binder - He Who Controls IPC, Controls the Droid
Explore Android's Binder IPC mechanism and its security implications, including potential vulnerabilities in keylogging and banking apps.
Bootstrapping Systems With Open Source Firmware
Explore open-source firmware for enhanced physical security and data protection. Learn about Heads, a custom firmware and OS configuration that combines hardware hardening with secure boot processes.
Kernel Exploit Hunting and Mitigation
Explore kernel exploit hunting and mitigation techniques, focusing on identifying and analyzing malware that leverages Windows kernel vulnerabilities for system compromise and evasion of security measures.
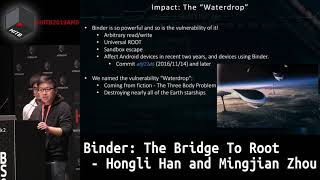
Binder - The Bridge To Root - Hongli Han and Mingjian Zhou
Exploración detallada de la vulnerabilidad "Waterdrop" en el controlador Binder de Android, que permite escalar privilegios y obtener acceso root en dispositivos populares, incluyendo los Pixel más recientes.
Overcoming Fear - Reversing With Radare2
Comprehensive guide to reversing with Radare2, covering installation, basic commands, visual modes, configuration, and practical applications. Suitable for beginners and professionals in computer security.

SSRF PWNs - New Techniques and Stories
Découvrez de nouvelles techniques d'attaques SSRF, leurs impacts sur la sécurité des applications web et des exemples concrets d'exploitation, présentés par deux experts en sécurité informatique.
Important Technologies of Kaspersky Endpoint Security Cloud
Explore key technologies in Kaspersky Endpoint Security Cloud for Windows, macOS, and smartphones, including threat protection, encryption, and device control features.
Mobile Security and Legacy Infrastructure Integration
Explore mobile security challenges, BYOD policies, and integration with legacy systems in enterprise environments. Learn about current trends and solutions in cybersecurity.
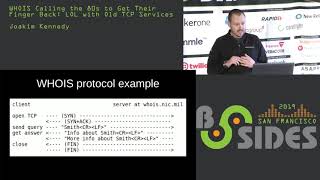
WHOIS Calling the 80s to Get Their Finger Back
Explore creating a remote access trojan using TCP services like Whois and Finger, discussing implementation, detection, and mitigation strategies for this Live Off the Land technique.
With Friends Like eBPF, Who Needs Enemies?
Explore eBPF's evolution from network monitoring to a powerful Linux kernel observability tool, its security implications, and potential misuse by attackers.
Battle of Windows Service - A Silver Bullet to Discover File Privilege Escalation Bugs Automatically
Discover file privilege escalation bugs automatically in Windows services using Advanced Local Procedure Call analysis and process monitoring techniques for enhanced system security.
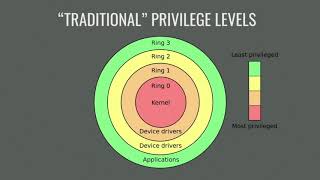
Why so Spurious? Achieving Local Privilege Escalation on Operating Systems
Explore a critical x86 architecture vulnerability exploitable for local privilege escalation across Windows, macOS, and Linux. Learn about this widespread security issue and its implications.