Using Sharable Mempools for Zero-copy Data Sharing Between DPDK Processes
Delve into advanced techniques for efficient inter-process communication using sharable mempools, focusing on zero-copy data sharing and high-performance packet processing optimization.
Integrating CI Pipeline as a Gate - Challenges, Roadblocks, and Implementation Strategy
Explore the journey of DPDK's CI pipeline integration, from its history and current challenges to future implementation strategies for improved patch acceptance criteria and testing frameworks.
Introducing UACCE Bus in DPDK - Unified Accelerator Framework Integration
Discover how UACCE bus enables seamless integration of accelerator devices in DPDK, exploring Shared Virtual Addressing implementation and its potential to enhance application performance.
Lessons Learnt from Reusing QDMA NIC to Base Band PMD
Discover key insights and practical lessons from converting AMD Xilinx FPGA NIC PMD to BBDEV PMD, exploring technical challenges and implementation strategies for efficient hardware adaptation.
Booting Your OS Across the NVMe-oF Transport - NVMe Boot Specification
Dive into standardized network booting solutions using NVMe-oF transport, exploring the new NVM Express Boot Specification and its UEFI implementation for large-scale deployments.
Booting Over NVMe/TCP Transport Using UEFI Implementation - Timberland Update
Explore the standardized NVMe® Boot Specification and its implementation for network-based OS booting, featuring NVMe-oF™ technology and UEFI integration for large-scale deployments.
Supporting an Upstream First Kernel Driver for HPC Fabrics
Explore the evolution and improvements of the HPC fabric driver hfi1, from its staging phase to mainline kernel integration, focusing on upstream development and open-source delivery methods.
When to Use Threads - Understanding IO Blocking, CPU Intensive, and High Volume Tasks
Discover when and why to implement threading in applications, from handling IO blocking tasks to managing CPU-intensive operations and processing high-volume tasks efficiently.
Bypassing EDR Detection: Userland Hooking Techniques and New Approaches
Explore advanced techniques for bypassing EDR solutions, including a new approach with Proof of Concept for understanding userland hooking and detection mechanisms.
Insecure Remote Operations: Windows Living Off the Land Techniques - Session 8
Dive into Windows remote operations security, exploring protocols, APIs, and admin tools through real-world examples. Learn powerful techniques for both defensive and offensive security operations.

Busting Red Team Trends with Style - Building a Custom ETW-Based Sysmon Replacement
Dive into advanced threat hunting with a custom ETW-based Sysmon replacement, exploring enhanced telemetry capabilities for detecting sophisticated red team techniques and threat actor fingerprinting.
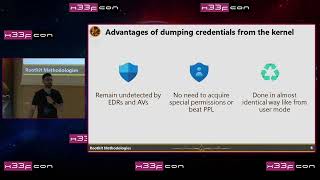
Kernel Games: The Ballad of Offense and Defense in Rootkit Methodologies
Dive into advanced kernel rootkit techniques for red team operations and defense strategies, covering stealthy persistence, EDR evasion, and practical detection methods with hands-on demos.
The Tortoise and the Hare - Avoiding Technical Debt in a Cloud Native World
Discover strategies to minimize technical debt in cloud-native environments through standards and loose coupling, focusing on sustainable development practices and long-term project success.
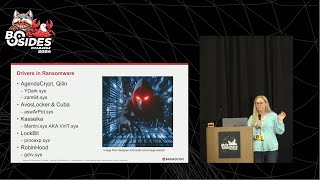
Driver Risk Scores: Threat Detection System for Vulnerable Device Drivers
Discover how Driver Risk Scores (DRS) system evaluates device driver vulnerabilities through seven key traits, enabling informed security decisions for system administrators and security teams.
Driving Your Own Vulnerability: How to Navigate the Road of BYOD Attacks
Explore Windows driver vulnerabilities and BYOD attack prevention through real-world case studies, understanding threat categories and security implications for effective system protection.
Retro Exploitation - Vintage Computing as a Vulnerability Research Playground
Explore vulnerability research and exploit development through vintage computing, focusing on the Commodore Amiga platform and practical demonstrations of retro software exploitation techniques.
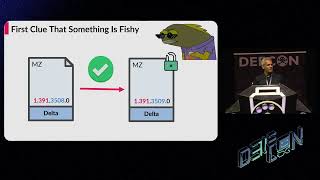
When Windows Defender Updates Become a Security Risk
Dive into Windows Defender's architecture and signature update vulnerabilities, exploring how unprivileged users can exploit security flaws to compromise Windows systems and manipulate EDR functionality.
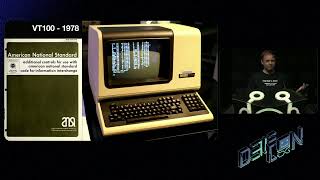
Terminally Owned - 60 Years of Terminal Escape Code Vulnerabilities
Explore terminal security vulnerabilities across platforms, from ASCII's escape character origins to modern exploit techniques, revealing critical remote code execution risks and defense strategies.
Bootsquad: Introduction to Secure Boot Exploitation and Defense
Dive into the world of cybersecurity and virtual reality as Joe Mast presents Bootsquad, exploring innovative security concepts and challenges in the DCGVR Village at DEF CON 31.
HookChain: A New Perspective for Bypassing EDR Solutions
Discover a sophisticated EDR bypass technique combining IAT Hooking, dynamic SSN resolution, and indirect system calls to redirect Windows subsystem execution flow while remaining undetected by traditional security measures.
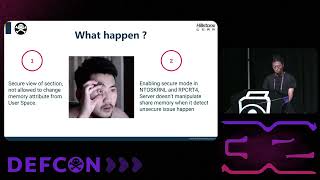
Using ALPC Security Features to Compromise RPC Services
Dive into Windows kernel security through ALPC and RPC services, exploring vulnerability exploitation techniques, security bypass methods, and system privilege escalation strategies.