The Future of Incident Response - Network Security Challenges
Bruce Schneier explores the future of incident response in cybersecurity, emphasizing the need for human-centric approaches and systems theory to effectively combat inevitable network attacks.

Cloud-based Detection Techniques for Botnets and Malware - AppSecEU 2014
Explores cloud-based techniques for detecting botnets and malware, highlighting limitations of traditional methods and discussing traffic analysis for pre-infection detection in cloud environments and virtual infrastructures.
Wi-Fi Hacking for Web Pentesters
Explore Wi-Fi vulnerabilities and learn to leverage web pentesting skills for designing and deploying malicious access points. Gain insights into attacking clients, hijacking accounts, and stealing sensitive information.
API Authentication's Poorly Implemented - Security Issues in Web APIs
Explore real-world API security issues, focusing on authentication and authorization problems across various platforms. Learn from examples ranging from online payment systems to embedded device infrastructures.
AppSec is Eating Security - The Future of Information Security
Explore the future of application security with insights on containerization, hardware security, and user-centric approaches. Learn about emerging trends and strategies for building safer digital ecosystems.
Attack-Driven Defense: Countering Real-World Attack Behaviors
Explore new network defense techniques from an attacker's perspective, focusing on detecting initial compromise, persistence, and lateral movement. Learn practical methods for effective alerting and traffic analysis.
DIY Command and Control for Fun and No Profit
Hands-on exploration of Command & Control botnets, providing insight into cybercriminal operations. Includes live malware demonstration for a realistic glimpse into this dark corner of the internet.
The Perilous Future of Browser Security
Explore browser security challenges, tradeoffs, and solutions. Learn about critical vulnerabilities, secure browser design, and balancing security with user experience in the face of evolving threats.
SSH and the Command Line
Master SSH and essential command-line skills for efficient server management, process monitoring, and file operations in Linux environments.
Building Secure Terabit Network Services with FD.io Technologies
Explore FD.io's role in building secure Terabit NaaS cloud networking, focusing on VPP and CSIT projects for high-performance, scalable, and robust cloud VPNs with encrypted overlays.
How Web Authentication Works: TLS, Password Hashing, OpenID Connect, OAuth 2, and JSON Web Tokens
Explore the inner workings of web authentication, covering TLS, password hashing, OpenID Connect, OAuth 2, and JSON Web Tokens in this comprehensive overview.

Netdiscover - An Open Source Tool for Finding Device IPs on Your Network Regardless of Subnet
Discover device IPs on your network with Netdiscover, an open-source tool that works across subnets. Learn installation, usage, and how to parse results in this practical tutorial.

Security Onion 2 Release Announcement and Live Demo
Discover the latest features and improvements in Security Onion 2 through an in-depth release announcement and live demonstration, showcasing advanced capabilities for network security monitoring and threat detection.
Security Onion 2.1 - Import Node and so-import-pcap Tutorial
Explore Security Onion 2.1's new Import Node feature and so-import-pcap tool for easy setup and PCAP analysis. Learn how to get started with minimal hardware requirements.
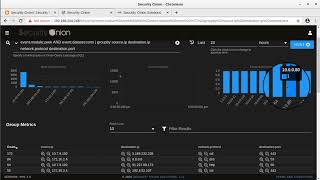
Security Onion Hybrid Hunter Beta 2 - New Hunt Interface Overview
Explore Security Onion's new Hunt interface in Hybrid Hunter Beta 2, enhancing threat detection and investigation capabilities for enterprise security teams.
Installing Security Onion Hybrid Hunter Beta 1 in a Virtual Machine
Step-by-step guide to installing Security Onion Hybrid Hunter Beta 1 in a virtual machine, demonstrating the setup process for this network security monitoring platform.
Building a Minimal Security Onion VM with sosetup-minimal
Learn to set up a minimal Security Onion virtual machine with dual NICs, focusing on Evaluation Mode installation and basic configuration for network security monitoring.

Building a Security Onion Virtual Machine for so-import-pcap
Learn to build a Security Onion virtual machine and use so-import-pcap to analyze network traffic. Gain hands-on experience with this powerful open-source security tool for network monitoring and threat detection.

Pcaps Ahoy! Commodity Malware Infections on Windows Hosts - Security Onion Conference 2018
Explore commodity malware infections on Windows hosts through packet capture analysis, enhancing your network security skills and threat detection capabilities.

Save Time with Modern Filtering Techniques - Stop Searching Like It's 1999
Explore modern filtering techniques to enhance security analysis efficiency, moving beyond outdated search methods for faster threat detection and response.

State of the Onion - Security Onion 2017
Comprehensive overview of Security Onion's latest developments, features, and future roadmap, presented by Doug Burks at the 2017 conference. Gain insights into this powerful network security monitoring platform.