Blue Team Hacking - Intrusion Detection with Snort
Learn to implement Snort, a leading open-source intrusion detection system. Covers installation, configuration, rule creation, and practical usage for effective network security monitoring.
Intrusion Detection With Snort
Learn to use custom and community Snort rules for effective intrusion detection. Discover how to capture network traffic, identify malicious activity, and set up logging and notifications for enhanced security.
Kali Linux Installation and Demo
Learn to install and use Kali Linux for ethical hacking, including VirtualBox setup, network configurations, and tools like NMAP, SQLMap, and Snort for cybersecurity tasks.
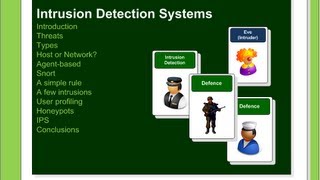
Introduction to Security and Network Forensics - Intrusion Detection Systems
Explore intrusion detection systems, security agents, and network forensics techniques. Learn about policy definition, user profiling, and honeypots in this comprehensive security overview.
Digital Investigator: Introduction to Intrusion Detection Systems (IDS)
Learn essential IDS concepts, network security terminology, and threat detection techniques. Explore network-based IDS and simple Snort rules for effective log analysis and intrusion prevention.
Introduction to Security and Network Forensics - Intrusion Detection Systems
Explore intrusion detection systems, network threats, and security policies. Learn about snort, policy violations, port scans, and user profiling in this comprehensive network forensics overview.
Cyber & Data - Intrusion Detection Systems
Explore intrusion detection systems, attack patterns, and practical rules for network security. Learn to create alerts and detect various threats using Snort and other tools.
Basic Setup of Security-Onion Snort, Snorby, Barnyard, PulledPork, Daemonlogger
Learn to set up a comprehensive Network Security Monitoring Server using Security-Onion, integrating tools like Snort, Snorby, Barnyard, PulledPork, and Daemonlogger for enhanced network protection.
Forwarding Snort Logs to Splunk
Learn to forward Snort logs to Splunk for powerful data analysis and monitoring. Explore Splunk's web interface to search, analyze, and visualize machine-generated data, enhancing your cybersecurity capabilities.

Installing & Configuring Snort
Learn to install and configure Snort 2 for intrusion detection. Explore the process of capturing network traffic, identifying malicious activity based on predefined rules, and setting up logging and notifications.
Software Defined Snort With Barnyard & Pulled Pork For NIDPS
Explore software-defined networking for enhanced network security, focusing on DDoS defense and traffic programming using Snort and its dependencies to mitigate WAF bypass attempts.
Leveraging Cloud SDNs to Solve OWASP Top Ten
Explore cloud SDN implementation for OWASP Top Ten security, featuring virtualized controls, service chains, and open-source technologies. Learn practical solutions for web security in virtual networks.
OpenAppID Open Source Next Gen Firewall with Snort - Adam Hogan
Learn about OpenAppID, an open-source next-generation firewall technology using Snort. Explore application control, custom detectors, and file inspection in network security.

Snort - History and Vision
Explore Snort's evolution and future in network security with Joel Esler. Gain insights into its development, key features, and upcoming innovations for effective threat detection and response.
Black Hat USA 2001 - Snort
Comprehensive exploration of Snort, a powerful open-source intrusion detection system. Learn its architecture, capabilities, and practical applications in network security.
Snort OpenAppID - How to Build an Open Source Next Generation Firewall
Learn to build an open-source next-generation firewall using Snort OpenAppID. Explore advanced network security techniques and gain hands-on experience in implementing cutting-edge protection for your systems.
Snort Beyond IDS - Open Source Application and File Control
Explore Snort's advanced features for application control, file inspection, and custom detectors. Learn to write rules, analyze output, and leverage Snort beyond traditional IDS capabilities.
Its Too Funky In Here - IDS - IPS Choices Benefits Drawback and Configurations ForgottenSec
Explore IDS/IPS systems, their benefits, drawbacks, and configurations. Learn about security engineering, deployment strategies, and future steps in network security monitoring.
Security Instrumentation - Be the Hero Getting Value from Security
Explore security instrumentation techniques to enhance organizational defenses, measure effectiveness, and demonstrate value in cybersecurity investments.
Deconstructing Firewalls - Automated Rules in Distributed SDN Networks
Explore automated firewall management through Software Defined Networking and SMT solvers, enabling scalable security solutions that integrate with IDS systems without compromising network performance.