Wiresharking All Protocols
Dive deep into network protocols using Wireshark, exploring CURL, WebSockets, TLS, RabbitMQ, PostgreSQL, HTTP/2, Server-Sent Events, MongoDB, SSH, and NodeJS HTTP Server for enhanced understanding.

CCNA - IPv4 Header - Complete Course
Comprehensive exploration of IPv4 header fields, including their functions and practical application, with Wireshark demonstrations and quizzes to reinforce understanding.
Wireshark
Master packet analysis and ethical hacking with Wireshark. Explore installation, filters, network protocols, and security vulnerabilities through hands-on tutorials and practical examples.
Wireshark
Learn to use Wireshark for network analysis, from installation to advanced features like capture filters, display filters, statistics, and expert information.
Wireshark Live Streams
Live streams covering Wireshark usage, network troubleshooting, TCP analysis, malware detection, and expert insights on packet analysis and network fundamentals.
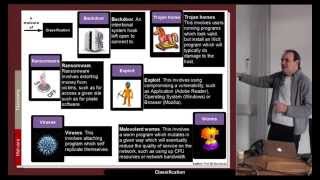
Malware Creation and Detection - Lecture 2 April 2015
Explore malware types, analysis methods, and detection techniques in this comprehensive lecture on cybersecurity threats and defenses.
Digital Investigator - Intrusion Detection Examples
Explore real-world intrusion detection scenarios, from P2P communications to various scanning techniques, enhancing your digital investigation skills.
CeH Unit 2 - Technical Foundations of Hacking
Explore technical hacking foundations: protocols, headers, addressing, fragmentation, and security issues. Gain insights into network communication and potential vulnerabilities.
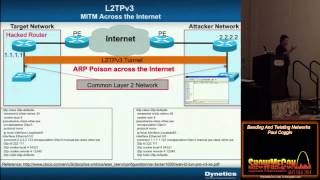
Bending and Twisting Networks - Exploiting Vulnerabilities in Routing and Infrastructure
Explore network manipulation techniques including policy routing, sniffing, IPv6/IPv4, L2 TPV3, and lawful intercept, with insights on potential vulnerabilities and critical infrastructure protection.

Diagnosing and Dealing with One-Sided Network Traffic
Diagnose and address one-sided traffic issues in network security. Learn to identify incomplete data collection and its impact on threat detection and hunting efforts.
Port Scanning Techniques and Tools for Network Security
Comprehensive overview of port scanning techniques, tools, and countermeasures for cybersecurity professionals and ethical hackers. Covers TCP flags, banner grabbing, and popular scanning software.
Scapy for Packet Manipulation and Sniffing
Learn to use Scapy for packet manipulation and sniffing in this hands-on tutorial. Gain practical skills in network analysis and security testing with this powerful Python library.
Traffic Capture and Analysis with tcpdump
Learn to capture and analyze network traffic using tcpdump, a powerful command-line packet analyzer. Gain practical skills for network monitoring, troubleshooting, and security analysis.
Deploying and Debugging HTTP/3 - Challenges and Solutions
Explore QUIC and HTTP/3 deployment challenges, debugging techniques, and real-world case studies. Learn about encryption, load balancing, and troubleshooting tools for modern networking protocols.
Deconstructing Kubernetes Networking - Fundamentals and Troubleshooting
Explore Kubernetes networking fundamentals, including components, troubleshooting, and packet flow analysis, to gain practical insights for effective container orchestration.
Digital Investigation: Ethernet, IP, TCP and UDP Protocols
Explore Ethernet, IP, TCP, and UDP protocols through hands-on Wireshark analysis. Learn network layers, addressing, headers, and potential vulnerabilities in digital investigations.
Advanced Cryptography - Tunnels and Network Security Lab
Explore advanced cryptography concepts through hands-on lab exercises focusing on tunnels, network captures, and OpenSSL implementation.
Extending Cilium with eBPF for Exposing HTTP/1 Golden Metrics
Explore eBPF-based HTTP/1 golden metrics retrieval in sidecarless environments, focusing on request count, response code, and latency. Learn implementation challenges and Prometheus integration for existing infrastructures.
Enforcing Network Policies for Host Processes via eBPF
Innovative approach using eBPF to identify and secure network traffic from host processes and pods using host network, enhancing Kubernetes network security beyond traditional methods.
Reverse Engineering Satellite Based IP Content Distribution
Reverse engineering satellite IP content delivery: from reception to packet analysis, error correction, and high bitrate handling. Culminates in creating a Linux-based client mimicking commercial versions.
Building a DDoS Mitigation Pipeline
Explore CloudFlare's automated DDoS mitigation pipeline, featuring real-time threat detection, attack categorization, and centralized iptables management for efficient and rapid response to common attacks.