Scaling Security Onion to the Enterprise - Lecture 102
Scaling Security Onion for enterprise-level network security monitoring: challenges, strategies, and tips for effective implementation and management.
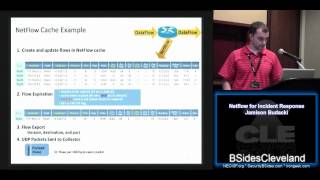
Netflow for Incident Response
Learn to leverage Netflow data for effective incident response, enhancing network security and threat detection capabilities.
Security Onion - Network Security Monitoring in Minutes
Learn to set up and utilize Security Onion for efficient network security monitoring, exploring its features and capabilities to enhance your organization's cybersecurity posture.
Basic Setup of Security-Onion Snort, Snorby, Barnyard, PulledPork, Daemonlogger
Learn to set up a comprehensive Network Security Monitoring Server using Security-Onion, integrating tools like Snort, Snorby, Barnyard, PulledPork, and Daemonlogger for enhanced network protection.

Security Onion 2 Release Announcement and Live Demo
Discover the latest features and improvements in Security Onion 2 through an in-depth release announcement and live demonstration, showcasing advanced capabilities for network security monitoring and threat detection.
Installing Security Onion Hybrid Hunter Beta 1 in a Virtual Machine
Step-by-step guide to installing Security Onion Hybrid Hunter Beta 1 in a virtual machine, demonstrating the setup process for this network security monitoring platform.

State of the Onion, Q&A, and Closing Remarks - Security Onion 2016
Explore the latest developments, insights, and future directions of Security Onion through an engaging Q&A session and closing remarks by Doug Burks at the 2016 conference.

Tuning NIDS Rules in Security Onion
Learn to effectively tune Suricata NIDS rules in Security Onion, enhancing your network intrusion detection capabilities and optimizing alert management for improved security monitoring.

Tuning NIDS Rules in Security Onion
Learn to optimize Suricata NIDS rules in Security Onion for enhanced network intrusion detection. Practical guidance on managing and fine-tuning alerts for improved security monitoring.
Quick Data Exfiltration Exercise with Security Onion
Hands-on exercise using Security Onion to analyze data exfiltration in a PCAP file. Learn to detect and investigate network security threats with practical tools and techniques.
Installing and Configuring Suricata for Intrusion Detection
Learn to install and configure Suricata, a powerful open-source threat detection engine combining IDS, IPS, and network security monitoring for enhanced cybersecurity protection.
Defeating Cognitive Bias and Developing Analytic Technique - T100
Explore cognitive biases in cybersecurity analysis, learn techniques to overcome them, and develop stronger analytical skills for more effective network security monitoring and incident response.
Bro - A Flexible Open-Source Platform
Explore Bro's open-source platform for network security monitoring, featuring packet capture, protocol analysis, and intelligence integration for enhanced threat detection.
Finding the Best Threat Intelligence Provider
Explore threat intelligence providers, focusing on data quality, formats, and alignment to enhance network security monitoring and defend against advanced persistent threats.
Sweet Security - Deploying a Defensive Raspberry Pi
Explore open-source tools and inexpensive hardware like Raspberry Pi to monitor, protect, and mitigate threats in IoT environments, addressing security challenges of outdated devices.
Peel Back the Layers of Your Enterprise and Make Your Adversaries Cry
Explore enterprise security with Security Onion, an open-source platform offering comprehensive visibility. Learn about intrusion detection, network monitoring, and incident response techniques to detect and interrupt adversaries quickly.
Building an Effective Intrusion Detection Program
Learn to build an effective intrusion detection program using affordable tools. Covers cloud apps, endpoints, network security monitoring, and crowdsourced incident response to catch breaches quickly.
Network Defender Archeology - An NSM Case Study in Lateral Movement with DCOM
Explore DCOM as a lateral movement technique from attacker and defender perspectives, addressing knowledge gaps and providing methodical insights for network security professionals.

State of the Onion - Security Onion Conference 2021
Comprehensive overview of Security Onion's latest developments, features, and future roadmap, presented by Doug Burks at the annual conference.

The Investigators Labyrinth - A Data-Driven Perspective
Explore data-driven perspectives on digital forensics and incident response, focusing on cognitive challenges, investigation processes, and analytical strategies for security professionals.

Security Onion Hybrid Hunter Beta 3 - Community ID and Sysmon Integration
Explore Security Onion Hybrid Hunter Beta 3, Community ID, and Sysmon features for enhanced network security and threat detection in enterprise environments.