Robots with Pentest Recipes - Automating Security Testing in DevOps
Explore automated security testing using Robot Framework to integrate tools like OWASP ZAP and Nmap. Learn to create easy-to-write test recipes for continuous delivery pipelines, enabling cross-team collaboration in application security.
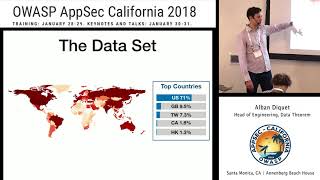
SSL Traffic Interception on Mobile Devices - Analysis and Protection
Análisis detallado de incidentes SSL en aplicaciones móviles, revelando patrones globales, casos notables y soluciones para desarrolladores contra la interceptación de tráfico.
Radio Hacking - Cars, Hardware, and More
Explore radio hacking techniques for wirelessly controlled devices like gates, garages, and cars. Learn about tools, vulnerabilities, and protective measures in this comprehensive introduction to RF security.
HTTPS Everywhere: Improving Web Security and Usability
Exploring Chrome's efforts to enhance HTTPS adoption: tools for debugging, reporting mechanisms for safe rollout, and strategies to improve web security.
ClickOnce Exploitation: One-Click Network Foothold - AppSec California 2016
Explore ClickOnce deployment vulnerabilities and learn a new methodology for establishing network footholds through minimal user interaction and phishing techniques.
Barbarians at the Gateway - DDoS and Web Attacks Against Cloud Platforms
Explore DDoS and web attacks on cloud platforms, examining tools, methods, and attacker motivations. Learn to identify patterns for better protection against evolving cyber threats.
Systematically Breaking and Fixing OpenID Connect
Explore systematic vulnerabilities and fixes in OpenID Connect, covering attack types, threat models, and countermeasures for improved authentication security.
Enterprise-wide SSL Automation with Lemur and CloudCA
Explore enterprise-wide SSL automation using Lemur and CloudCA, enabling developers to easily manage SSL certificates and enhance security across applications.
Calm Down: HTTPS Is Not a VPN
Explore HTTPS limitations, privacy concerns, and security implications in web communications. Learn about packet capture, fingerprinting, and potential vulnerabilities in encrypted connections.
OCSP Stapling in the Wild - Lecture
Explore OCSP stapling in the wild with experts Devdatta Akhawe and Emily Stark. Learn about TLS security, browser implementations, and real-world challenges in HTTPS ecosystems.
HTTPS and TLS Security Practices - Front Line Insights 2016
Comprehensive overview of modern HTTPS and TLS security practices, covering protocol vulnerabilities, certificate fundamentals, and best practices for implementing strong encryption in web services.
SQLViking - Pillaging Your Data
Explore SQLViking, a tool for passive SQL query logging and active TCP injection attacks on databases. Learn about network security vulnerabilities and potential countermeasures.
Medical Device Security: An Infectious Disease - Risks and Vulnerabilities
Explore vulnerabilities in medical devices and healthcare systems, examining potential risks to patient safety and discussing strategies for improving security in the healthcare landscape.
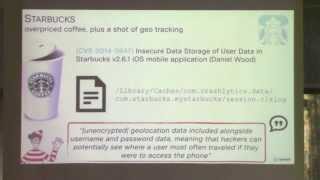
When Geo Goes Wrong - A Case Study of Geolocation Vulnerabilities in Mobile Apps
Exploring geolocation vulnerabilities in mobile apps, focusing on a dating app case study. Discusses common bugs, attack methods, and best practices for secure location-aware app development.
Everything You Need to Know About Certificate Pinning - AppSecEU 2016
Comprehensive guide to certificate pinning: implementation, benefits, and potential pitfalls. Essential knowledge for enhancing mobile app security and protecting against man-in-the-middle attacks.
Finding Bad Needles on a Worldwide Scale - Application Security
Explore techniques for identifying and locating malicious elements across global networks, enhancing cybersecurity practices and threat detection capabilities.
Shameful Secrets of Proprietary Network Protocols
Reverse engineering proprietary protocols: case studies revealing security flaws in financial software, home automation, and embedded systems. Techniques for uncovering hidden vulnerabilities in undocumented binary protocols.

Lessons from Trusting JavaScript Cryptography - Biting into the Forbidden Fruit
Exploring real-world JavaScript cryptography implementations, debunking myths, and providing an updated perspective on JS crypto security through vulnerability analysis and practical examples.
Getting a Handle on Mobile Security
Comprehensive overview of mobile security challenges and best practices, covering encryption, data protection, and platform-specific concerns for developers building secure mobile applications.
Owning the Message Oriented Middleware - Security Analysis and Attacks
Explore enterprise messaging security from JMS API, ActiveMQ vulnerabilities, and JMSDigger tool perspectives. Learn offensive techniques and live demonstrations for assessing messaging applications.
Mantra OS - Penetration Testing Tools and Methodologies
Explore Mantra OS's penetration testing tools for web application security, including DDoS, SQL injection, and man-in-the-middle attacks. Learn practical methodologies and controlled environment testing techniques.