DisLog: A Separation Logic for Disentanglement
Explore DisLog, a novel separation logic for verifying disentanglement in parallel programs. Learn about its applications, benefits, and case studies in concurrent programming.
VST-A: A Foundationally Sound Annotation Verifier for Imperative Programs
Explore VST-A, a foundationally sound annotation verifier combining automation with rich assertion language and formal soundness proofs for imperative program verification.
Logical Foundations - Session Preview
Explore logical foundations in programming languages with Emanuele D'Osualdo's preview of the POPL'24 session, offering insights into cutting-edge research and developments.
Algorithmic Verification - Session Preview
Explore algorithmic verification techniques in this concise POPL'24 session preview, focusing on cutting-edge research and advancements in the field.
Synthesis 2 - Session Preview
Explore cutting-edge research in program synthesis with Hila Peleg's preview of the Synthesis 2 session at POPL'24, highlighting recent advancements in the field.
Automated Verification - Session Preview
Explore automated verification techniques and advancements in program analysis with expert Viktor Kunčak at POPL'24's session preview.
Evolving Weak Memory Models for Evolving Architectures
Explore evolving weak memory models for modern architectures, focusing on advancements and challenges in concurrent programming and hardware design.
Mostly Automated Verification of Liveness Properties for Distributed Protocols with Ranking Functions
Explore a novel framework for mostly automated verification of liveness properties in distributed protocols using ranking functions, reducing complex problems to simpler safety property verifications.
Deadlock-Free Separation Logic: Linearity Yields Progress for Dependent Higher-Order Message Passing
Explore LinearActris, a novel logic ensuring deadlock and leak freedom in message-passing concurrency, combining session types and separation logic for higher-order program verification.
The Logical Essence of Well-Bracketed Control Flow
Explore the logical foundations of well-bracketed control flow in programming, introducing a Hoare-style program logic for reasoning and verification, with formalized results in the Iris framework and Coq.
Logic Against Sneak Obfuscated Malware
Explore SMT solvers for binary analysis and code deobfuscation in IT security. Learn practical applications, limitations, and solutions for enhancing malware analysis capabilities.
Chat with Hillel Wayne about TLA+
Explore TLA+, a formal specification language, with Hillel Wayne. Learn about its applications, benefits, and the upcoming TLA+ Conference, gaining insights into this powerful tool for software design and verification.
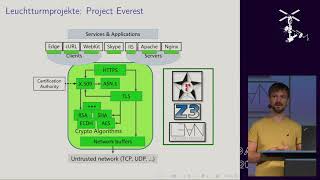
Beweisbar sichere Software
Überblick über verifizierbare Programmiersprachen und Theorembeweiser zur Entwicklung beweisbar sicherer Software. Vergleich verschiedener Ansätze anhand von Beispielen.
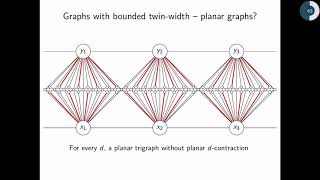
Twin-width I - Tractable FO Model Checking
Explore tractable FO model checking using twin-width, covering trigraphs, contraction sequences, and dynamic programming for efficient graph analysis.
Verifying the LLVM
Explore LLVM's intermediate representation, its complexities, and the Vellvm project's approach to formal verification using Coq, aimed at ensuring compiler reliability and security.
Building Confidence in Concurrent Code with a Model Checker
Explore model-checking techniques to detect concurrency errors in system designs. Learn how TLA+ can improve confidence in concurrent code and save time during development.
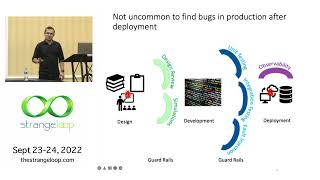
Formal Modeling and Analysis of Distributed Systems
Explore formal methods for distributed systems using P programming framework. Learn to model, specify, and verify complex systems across development phases, from design to production.
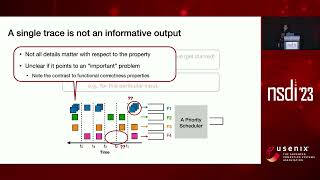
Formal Methods for Network Performance Analysis
Explores using formal methods for network performance analysis, offering a more exhaustive approach than simulation. Demonstrates effectiveness in analyzing packet scheduling algorithms and generating problematic workloads.
Designing Distributed Systems with TLA+
Learn to design and test distributed systems using TLA+, a powerful specification language that complements unit testing and type systems for catching complex concurrency bugs and validating system designs.
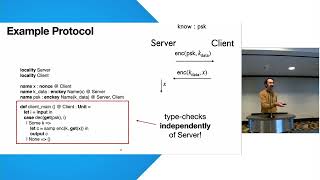
OWL - Compositional Verification of Security Protocols via an Information-Flow Type System
Explore a novel approach to verifying security protocols using an information-flow type system, offering insights into compositional verification techniques and their practical applications.
WebSpec - Towards Machine-Checked Analysis of Browser Security Mechanisms
Explore machine-checked analysis of browser security mechanisms, focusing on WebSpec's approach to enhancing web security through formal verification and automated reasoning techniques.