
Safety and Liveness of Robot Behaviors
Explore formal methods for designing robots, guaranteeing behavior, and identifying potential issues. Learn about safety and liveness properties in robotic systems, including multi-robot and human-robot interactions.
The Human Factors of Formal Methods - Stanford Seminar
Exploring human-centered approaches to improve formal methods' usability in software development, addressing cognitive challenges and misconceptions to enhance adoption by non-experts.
Privacy-preserving Automated Reasoning
Explore privacy-preserving formal reasoning techniques, including ppSAT solver and zero-knowledge protocols for Boolean formula unsatisfiability, advancing automated verification while maintaining data privacy.
Context-Bounded Analysis for Systematic Testing of Concurrent Programs - CAV Award 2023
Discover groundbreaking research on context-bounded analysis and its impact on testing concurrent programs in this CAV Award 2023 presentation.
Robbing the Bank with Automated Reasoning - Using Formal Methods for EMV Payment Protocol Security
Uncover critical vulnerabilities in EMV payment protocols using automated reasoning. Learn how formal methods can expose security flaws in widely-used smartcard payment systems.
Formalisierung der Mathematik - Wann führen Computer die Beweise?
Experten diskutieren die Zukunft formaler mathematischer Beweise durch Computer, deren Potenzial, Herausforderungen und Auswirkungen auf die mathematische Forschung und Gemeinschaft.
Translating HOL-Light Proofs to Coq
Découvrez la traduction des preuves HOL-Light vers Coq, explorant les défis et solutions pour la vérification formelle entre systèmes logiques différents.
SMT Solvers in IT Security - Deobfuscating Binary Code with Logic
Explore SMT solvers for deobfuscating binary code in IT security. Learn practical applications, theoretical limitations, and solutions for enhancing malware analysis and vulnerability identification.
Engineering for Privacy in Mixed Reality
Explore Mozilla's approach to user privacy in mixed reality, focusing on empowering users through secure immersive web browsing and social VR platform development.
Formal Synthesis for Robots - Leveraging Formal Methods in Robotic Design
Explore how formal methods and synthesis techniques can design, explain, and guarantee robot behavior, with examples of modular robots, swarms, and human-robot interaction.
Security Under the BEAM - Building Trustworthy Isolation in Operating Systems
Explore the Kry10 Secure Platform, combining BEAM VM isolation, seL4 Microkernel, and formal methods to build trustworthy, fault-tolerant systems for IoT and next-gen software development.
Complete First-Order Reasoning for Properties of Functional Programs - OOPSLA 2023
Explore complete first-order reasoning for functional program properties, uncovering theoretical foundations of verification tools and explaining their efficacy, limitations, and user assistance role.
Logic and Decidability in Programming Languages - Session Preview II
Explore logic and decidability in programming languages. Gain insights into theories of arithmetic, linear real rings, and state machines. Discover new minimization algorithms and their applications.
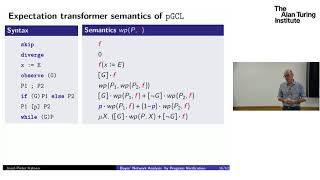
Bayesian Inference by Program Verification - Joost-Pieter Katoen, RWTH Aachen University
Explore Bayesian inference through program verification, learning how weakest precondition reasoning can be applied to exact inference and analyzing expected sampling times in Bayesian networks.
Building Measure Theory Using Hierarchy Builder
Explore the Hierarchy Builder DSL for Coq and its application in constructing measure theory and Lebesgue measure, with insights for potential adaptations to other proof assistants.
Mario Carneiro: System Introductions I - Lean
Explore the Lean theorem prover with Mario Carneiro in this introductory talk, covering its key features and applications in mathematical formalization.
Branch Cuts and Formal Methods in Mathematics
Explore branch cuts in complex analysis and their role in formal methods, focusing on mathematical challenges and computational applications.
From 100 to 1000+ Theorems - Advancements in Mathematical Proof Verification
Explore the journey of formalizing mathematics, from initial proofs to extensive theorem libraries, and discover the challenges and progress in this field.
Flexiformal Math Libraries - Collecting and Organizing Beyond Definitions, Theorems, and Proofs
Explore innovative approaches to organizing mathematical knowledge beyond traditional definitions, theorems, and proofs in this insightful presentation on flexiformal math libraries.
Univalent Double Categories - Formalization and Applications in Category Theory
Explore univalent double categories in category theory, their formalization in Coq, and applications in mathematics and computer science.
Reasoning About Hilbert's Choice Operator in SMT
Explore implementing Hilbert's ε-terms in SMT solvers, gaining access to a new logical choice primitive for enhanced reasoning capabilities.