Privacy-preserving Automated Reasoning
Explore privacy-preserving formal reasoning techniques, including ppSAT solver and zero-knowledge protocols for Boolean formula unsatisfiability, advancing automated verification while maintaining data privacy.
SMT Solvers in IT Security - Deobfuscating Binary Code with Logic
Explore SMT solvers for deobfuscating binary code in IT security. Learn practical applications, theoretical limitations, and solutions for enhancing malware analysis and vulnerability identification.
Complete First-Order Reasoning for Properties of Functional Programs - OOPSLA 2023
Explore complete first-order reasoning for functional program properties, uncovering theoretical foundations of verification tools and explaining their efficacy, limitations, and user assistance role.
Reasoning About Hilbert's Choice Operator in SMT
Explore implementing Hilbert's ε-terms in SMT solvers, gaining access to a new logical choice primitive for enhanced reasoning capabilities.
Counterexample Driven Quantifier Instantiations with Applications to Distributed Protocols
Explore a novel interactive verification methodology using relational abstraction to tackle quantifier reasoning challenges in infinite-state systems, with applications to distributed protocols.
Mostly Automated Verification of Liveness Properties for Distributed Protocols with Ranking Functions
Explore a novel framework for mostly automated verification of liveness properties in distributed protocols using ranking functions, reducing complex problems to simpler safety property verifications.
Logic Against Sneak Obfuscated Malware
Explore SMT solvers for binary analysis and code deobfuscation in IT security. Learn practical applications, limitations, and solutions for enhancing malware analysis capabilities.
Jumping the Fence - Comparison and Improvements for Existing Jump Oriented Programming Tools
Explore Jump Oriented Programming, comparing tools and discussing improvements. Covers gadget search, comprehension strategies, and architecture support for various platforms including ARM and AVR.
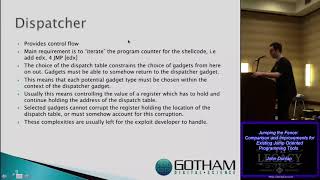
Jumping the Fence - Comparison and Improvements for Existing Jump Oriented Programming Tools
Exploring Jump Oriented Programming tools, comparing techniques, and discussing improvements. Covers dispatcher gadgets, functional gadgets, and AVR support with demos and practical insights.
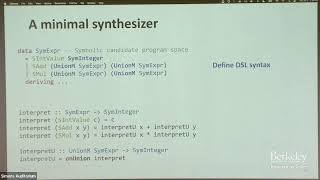
Grisette: Symbolic Compilation as a Functional Programming Library
Explore symbolic compilation techniques in functional programming with Grisette, enhancing model and system synthesis capabilities for advanced software development.
Deconstructing Firewalls - Automated Rules in Distributed SDN Networks
Explore automated firewall management through Software Defined Networking and SMT solvers, enabling scalable security solutions that integrate with IDS systems without compromising network performance.
Explicit Refinement Types - A Type Theory with Embedded Proofs
Explore λert, a type theory with explicit proof refinement types. Learn about its soundness, denotational semantics, and formalization in Lean 4.
Trustworthy Runtime Verification via Bisimulation - Experience Report
Explore trustworthy runtime verification using bisimulation in the Copilot framework. Learn how CopilotVerifier generates correctness proofs for compiled monitors, enhancing safety-critical system assurance.
Trust but Verify: Scaling Deductive Verification with Abstract Interpretation - N40AI'24
Explore scaling deductive verification for smart contracts using abstract interpretation. Learn about pointer analysis algorithms, program simplifications, and challenges in low-level code analysis.
Liquid Type Systems - Understanding Type Theory and SMT Solvers
Explore the innovative Liquid Types system, combining traditional type theory with SMT solvers to enhance type system expressivity while maintaining practical usability in programming languages.