More Vulnerable Embedded Systems
Explore vulnerabilities in embedded systems, focusing on security flaws and potential exploits in various devices and technologies.
Battery Firmware Hacking
Explore battery firmware vulnerabilities, Smart Battery System, and potential attacks. Learn about data flash signatures, boot modes, and firmware manipulation techniques for enhanced security awareness.
Finding the Needle in the Hardware Haystack - Identifying and Exploiting Vulnerabilities
Explore hardware reverse engineering for embedded systems security. Learn techniques to identify vulnerabilities, assess risks, and develop a structured testing process for comprehensive device security analysis.
Embedding Security in Embedded Systems
Explore embedded system security challenges in IoT devices, from cameras to smart buildings. Learn about vulnerabilities, coordinated disclosure, and best practices for securing interconnected systems.
Firmware Security - Why It Matters and How You Can Have It
Explore firmware security's importance, vulnerabilities, and mitigation strategies. Learn about attack surfaces, System Management Mode, and ways to enhance protection in various computing environments.

Securing Firmware - Secure and Trusted Boot in OpenBMC
Explore secure and trusted boot in OpenBMC, covering hardware root of trust, TPMs, keys, and signing while preserving user freedom to replace firmware securely.
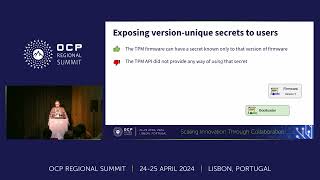
Recovery from Firmware Vulnerabilities in TPM - Securing Hardware Roots of Trust
Discover how new TPM specification APIs enable firmware vulnerability recovery and self-attestation capabilities, enhancing hardware security and trust restoration mechanisms.
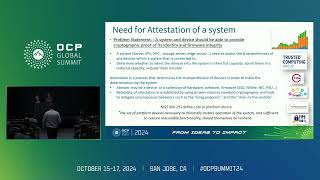
Leveraging FPGA-Based Root of Trust for Efficient, Dynamic, and Remote Platform Attestation
Discover how FPGA-based Root of Trust enables secure platform attestation, providing dynamic cryptographic proof of identity and firmware integrity in modern computing systems.
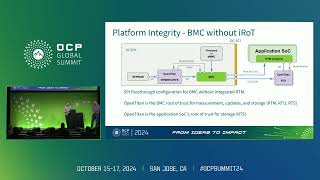
OpenTitan: Open-Source Hardware Root of Trust - Project Update
Discover the latest developments in OpenTitan's open-source hardware root of trust, including its architecture, security features, and applications for firmware protection and secret storage.
Mutual Authentication Vulnerabilities in Physical Access Control Systems
Explore physical access control system vulnerabilities, authentication weaknesses, and practical exploit techniques, featuring live demonstrations with HID readers and security tools.
Compromising Electronic Loggers and Creating Truck-to-Truck Worm - Security Vulnerabilities in ELD Systems
Discover critical security vulnerabilities in Electronic Logging Devices (ELDs) and their implications for truck network security, from reverse engineering to proof-of-concept attacks and industry-wide security reforms.
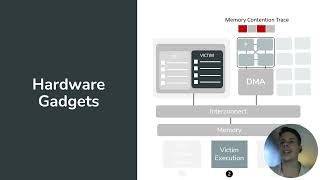
Microarchitectural Side Channel Attacks on MCU Bus Interconnect - BUSted 2024
Explore microarchitectural side channel attacks on MCU bus interconnects, focusing on vulnerabilities and potential security implications for embedded systems.
Trusted Firmware - Building Secure Firmware Collaboratively
Explore collaborative firmware security with Trusted Firmware. Learn about vulnerabilities, applications, and architecture for building robust, secure systems across various platforms.
OP-TEE is Ready - Let's Use It
Explore OP-TEE's capabilities and practical applications in secure embedded systems with expert guidance from Pengutronix e.K.'s Rouven Czerwinski.
Integrity Measurements and the Cruel World
Explore integrity measurement systems for embedded devices, overcoming challenges in security-enhanced Android and Linux to improve reliability without compromising user experience.
Rich Authorization in Resource-Constrained Devices - TPM 2.0 Design and Use Cases
Explore TPM 2.0's advanced authorization capabilities in resource-constrained devices. Learn policy design, calculation, and satisfaction, with practical use cases and a complex example.
Breaking Firmware Trust From Pre-EFI - Exploiting Early Boot Phases
Explore recent UEFI firmware security changes, focusing on Intel CPUs. Covers firmware mitigations in SMM/DXE and new attacks on Intel PPAM, offering unique insights from an offensive security perspective.
Device Security in the OCP Supply Chain - Overview of How OCP SAFE Addresses Device Firmware Challenges
Explore how OCP S.A.F.E. framework tackles device firmware security challenges and strengthens supply chain integrity through expert insights and practical solutions.
Exposing Critical Threats in Cellular Modem Security - Telit Vulnerabilities Analysis
Uncover critical security vulnerabilities in Telit cellular modems, including remote code execution flaws, SMS-based attacks, and MIDlet compromise methods that affect millions of connected devices.
Protecting Yourself From Supply Chain Attacks - Trust Is Overrated
Discover practical strategies and tools for validating hardware and software integrity, minimizing supply chain risks, and implementing effective security measures across your technology stack.
Contactless Overflow Code Execution Vulnerabilities in Payment Terminals and ATMs
Uncover critical NFC payment terminal vulnerabilities and their exploitation through contactless attacks, including ATM jackpotting techniques and firmware manipulation across major payment systems worldwide.