Protecting Bare-metal Embedded Systems with Privilege Overlays
Innovative technique for securing bare-metal embedded systems using privilege overlaying, code integrity, and randomization to prevent attacks while minimizing performance impact.
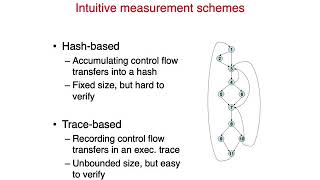
OAT - Attesting Operation Integrity of Embedded Devices
Innovative framework for attesting operation integrity of embedded devices, addressing control-flow hijacks and data-only attacks in IoT systems through lightweight measurement and verification techniques.
Ghost in the Machine: Challenges in Embedded Binary Security - Enigma 2017
Explores challenges in embedded binary security, highlighting the lag behind general-purpose systems and difficulties in adopting modern exploit mitigations due to constraints in embedded environments.
Reducing Security Risks in the Hybrid Workplace with Windows 11 and Surface
Discover how Windows-enhanced security settings on Surface devices reduce organizational security risks by 60% in hybrid workplaces, leveraging Microsoft's holistic ecosystem from chip to cloud.
Security Features for UBIFS
Explore UBIFS cryptography support, fscrypt implementation, and data authentication for embedded systems. Learn about MTD stack protection and establishing a chain of trust.
Azure Sphere - Fitting Linux Security in 4 MiB of RAM
Explore Azure Sphere's innovative approach to securing IoT devices with Linux, overcoming memory constraints and implementing robust security measures for microcontroller-powered systems.
Project Cerberus: Hardware Root of Trust for Cloud Security
Explore hardware-enforced secure boot and measured boot with Project Cerberus, a cryptographic microcontroller enhancing firmware security for cloud platforms and data centers.
Exploiting Hardware Glitches and Side Channels in Perfect Software
Uncover vulnerabilities in flawless software through hardware glitches and side-channel attacks. Learn advanced exploitation techniques for enhancing cybersecurity defenses.
Embedded Systems Security - Common Threats and Best Practices
Explore embedded system security threats, proactive controls, and best practices to protect interconnected devices from vulnerabilities and potential DDoS attacks.
TEEP Implementation on RISC-V Keystone and Arm TrustZone
Explore TEEP implementation on RISC-V Keystone and Arm TrustZone, focusing on secure provisioning techniques for trusted execution environments in embedded systems.
Boot-Time Optimization for the Real World
Explore techniques for optimizing boot time in embedded systems, balancing speed with security and functionality. Learn practical strategies for real-world implementation and hardware design.
Demystifying Intel Security Technologies in Firmware
Explore Intel's firmware security technologies, including Converged Security, Boot Guard, and Trusted Execution, with insights on implementation and platform protection mechanisms.
OP-TEE - When Linux Loses Control
Explore OP-TEE's role in secure computing, examining how it operates independently from Linux to enhance system security and protect sensitive operations.
Shhh - Stop Sharing Secrets: A Secure Mindset for Embedded Development
Explore secure embedded development practices, focusing on encryption, authentication, and trusted execution environments to protect IoT devices and data.
Secure Bootloaders and Secure Software Update Support in CIP - Civil Infrastructure Platform
Explore secure bootloaders and software updates in CIP, focusing on implementation, IEC-62443 compliance, and the collaborative efforts of CIP workgroups to enhance industrial software security.
IoT and OT Firmware Security Analysis with EMBA - From Firmware to Exploit
Automated firmware analysis for IoT and OT devices using EMBA, an open-source tool that detects vulnerabilities, identifies exploits, and supports penetration testing of embedded systems.
Design and Implementation of a Security Architecture for Critical Infrastructure Industrial Control Systems
Comprehensive security architecture for critical infrastructure, addressing nation-state cyber threats. Covers hardware roots of trust, secure boot, and integrity measures across various systems and networks.
Firmware Vulnerabilities in Critical Infrastructure - Tools and Techniques for Security Analysis
Explore firmware vulnerabilities in critical infrastructure using open-source tools. Learn techniques for deep security analysis, uncovering risks, and leveraging AI to simplify research and reverse engineering.
Embedded Threats: A Deep Dive into the Attack Surface and Security Implications of eSIM Technology
Explore the attack surface and security implications of eSIM technology through a comprehensive deep dive into embedded threats.
Hardware Security I - CHES 2024
Explore hardware security topics presented at CHES 2024, chaired by Jan Richter-Brockmann. Gain insights into cutting-edge research and developments in the field of cryptographic hardware and embedded systems.
Faults in Our Bus - Novel Bus Fault Attack to Break Trusted Execution Environments in Embedded Systems
Uncover novel bus fault attacks on Trusted Execution Environments in embedded systems, exploring vulnerabilities in SoC system buses and their implications for IoT security and TEE implementations.