Post-Quantum Cryptography - Part 3
Explore post-quantum cryptography advancements and gain insights from CHES 2021 conference closing remarks, advancing your understanding of cutting-edge cryptographic technologies.
A Canonical Event Log Structure for IMA - Optimizing Attestation Information
Explore a new Canonical Event Log structure for IMA, enhancing Linux system attestation with algorithm agility, sequence numbering, and optimized storage for improved security and efficiency.

Replace Your Exploit-Ridden Firmware with Linux
Learn how to replace vulnerable UEFI firmware with NERF, an open-source system using a tiny Linux kernel and initramfs, enhancing security and reducing exploit risks in PC and laptop firmware.
OpenPOWER Host OS Secure Boot Key Management
Explore OpenPOWER's flexible key management for Linux-based secure boot, covering architecture, ownership, updates, storage, and compatibility across firmware, kernel, and userspace.
IoT Developer's Guide to Building Secure IoT Devices
Learn essential strategies and best practices for developing secure IoT devices, focusing on key vulnerabilities and effective mitigation techniques.
Insights from Zephyr Security Audit and Vulnerability Experiences
Explore Zephyr's security evolution through vulnerability analysis and external audit findings. Gain practical insights to enhance embedded system security in your projects.
Leveraging and Managing SBAT Revocation Mechanism on Distribution Level
Explore SBAT revocation mechanisms at the distribution level, focusing on leveraging and managing these systems for enhanced security and efficiency.
Knockin' On MediaTek ADSP's Door
Reverse engineering MediaTek's audio DSP firmware reveals vulnerabilities in RTOS and Android HAL, potentially enabling local privilege escalation and eavesdropping on user conversations.
Low Level BootROM Protocol Fuzzing Secure Memory Regions
Explore low-level protocol fuzzing for secure microcontrollers, uncovering vulnerabilities in BootROM USB drivers. Learn about a custom fuzzing framework for SPI, I2C, USB, and UART, and its application in hardware security research.
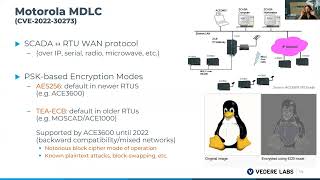
ICEFALL - Revisiting A Decade Of OT Insecure-By-Design Practices
Revisiting insecure-by-design practices in OT devices, highlighting persistent security issues across industries and critical infrastructure, with technical deep-dives and implications for risk management.
Firmware Security 101
Explore firmware security fundamentals, vulnerabilities, and protection strategies in embedded systems with expert insights and practical examples.
Researching the Unisoc Baseband
Exploring Unisoc baseband security: reverse-engineering and fuzzing LTE protocol stack to uncover vulnerabilities in budget smartphone chipsets, disrupting radio communication.
Baring the System - New Vulnerabilities in SMM of Coreboot and UEFI Based Systems
Unveiling new vulnerabilities in SMM of Coreboot and UEFI systems, exploring impacts, and discussing mitigation techniques. Includes release of CHIPSEC module for automatic detection.
Neurosurgery for Industrial Routers - Security of Sarian OS
Explore vulnerabilities in industrial routers, focusing on Digi WR21 and Sarian OS. Uncover internal workings, network protocols, and security features of critical infrastructure devices.
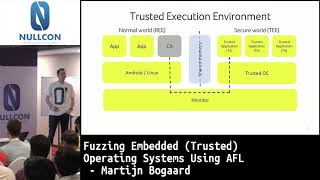
Fuzzing Embedded - Trusted Operating Systems Using AFL
Explore fuzzing techniques for Trusted Execution Environments using AFL, focusing on OP-TEE. Learn about challenges, coverage tracking, and creating initial inputs for effective embedded system security testing.
Hardware Backdooring is Possible
Demonstration of permanent hardware backdooring using Rakshasa malware, exploring BIOS vulnerabilities and implications for computer security and forensics practices.
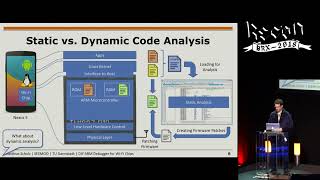
DIY ARM Debugger for Wi-Fi Chips
Explore DIY ARM debugging for Wi-Fi chips using Nexmon framework. Learn to set breakpoints, handle debugging events, and perform single-step debugging on Cortex-R4 microcontrollers in FullMAC Wi-Fi firmwares.
Static Analysis-Based Recovery of Service Function Calls in UEFI Firmware
Discover a new tool for automated recovery of service calls and EFI type info in UEFI firmware, simplifying vulnerability hunting and making firmware code resemble original source.
Breaking Firmware Trust From Pre-EFI - Exploiting Early Boot Phases
Exploración de vulnerabilidades en fases tempranas de arranque, evolución de mitigaciones de firmware y nuevos ataques en módulos de evaluación de plataformas Intel desde una perspectiva ofensiva.
Exploring the Hidden Attack Surface of OEM Routers
Descubre vulnerabilidades críticas en routers OEM y sus implicaciones para la seguridad. Análisis detallado de un caso de estudio que revela fallos en la cadena de suministro y prácticas de seguridad deficientes.
Finding 0days in Embedded Systems with Code Coverage Guided Fuzzing
Innovative fuzzing technique for embedded systems, overcoming challenges to discover critical vulnerabilities in network devices through emulation, dynamic binary instrumentation, and guided fuzzing.