TOCTOU Attacks Against Secure Boot and BootGuard
Explore TOCTOU attacks on Intel's BootGuard, learn about vulnerabilities in secure boot processes, and discover open-source tools for testing system security.
Eight Crazy Ways to Foil Hardware Attacks - For All Budgets
Explore cost-effective strategies to protect embedded devices from hardware attacks. Learn about common vulnerabilities, defense mechanisms, and design decisions for optimal security in IoT and industrial control systems.
HPE iLO5 Firmware Security - Go Home Cryptoprocessor, You're Drunk!
Explore vulnerabilities in HPE Gen10 servers' iLO5 management technology, focusing on the "silicon root of trust" and its implications for server security.
Remotely Attacking System Firmware
Explore remote attack vectors targeting system firmware, including networking and updates. Learn about exploiting UEFI vulnerabilities for installing persistent implants at scale.
ThunderStrike 2 - Sith Strike
Explore firmware vulnerabilities in Mac systems, demonstrating software-only attacks and showcasing the potential of Mac firmware malware. Learn about shared vulnerabilities and case studies.
Firmware.RE - Firmware Unpacking, Analysis and Vulnerability-Discovery as a Service
Large-scale analysis of firmware images reveals vulnerabilities across embedded systems, highlighting security challenges and the need for improved tools and techniques in firmware analysis.
Computrace Backdoor Revisited
Exposición de vulnerabilidades en software antirrobo Computrace, demostrando fallos de seguridad y posibles ataques. Incluye análisis del protocolo, comportamiento sospechoso y métodos de detección/desactivación.
Insecurity of Embedded Devices' Firmware - Fast and Furious at Large Scale
Explore embedded device firmware vulnerabilities and large-scale security challenges in this DefCamp 2015 presentation, offering insights for security specialists and developers.
Analysis of the Attack Surface of Windows 10 Virtualization-Based Security
Explore Windows 10's virtualization-based security, its implementation details, and potential vulnerabilities. Includes demonstrations of exploits against VBS and firmware, with a focus on platform complexity issues.
Green Lights Forever - Analyzing the Security of Traffic Infrastructure
Researchers expose security vulnerabilities in traffic signal systems, demonstrating potential for disruption and safety risks. Recommendations for improving embedded systems security are provided.
FirmWar - An Imminent Threat to the Foundation of Computing
Explore the overlooked risks of enterprise device firmware in IT supply chains, uncovering vulnerabilities and discussing their impact on computing security and industry practices.
How Hardware Boundaries Define Platform Security
Exploring how hardware component boundaries impact platform security, focusing on outsourced components, supply chain risks, and threat modeling gaps in modern hardware architectures.
Nifty Tricks and Sage Advice for Shellcode on Embedded Systems
Clever tricks for writing exploits on embedded systems, including tiny shellcode for ARM, memory corruption on 8-bit micros, and developing without debuggers or firmware images.
Random Walk Through A Few Million Things
Explore IoT security challenges in enterprises, examining millions of devices to reveal vulnerabilities, default credentials, and outdated firmware. Gain insights into the current state of IoT security.
Colorful Like a Chameleon - Security Nightmares of Embedded Systems
Explore security vulnerabilities in embedded systems, focusing on real-world examples and practical attack scenarios. Learn about potential risks and strategies for enhancing embedded system security.

Secure Boot Under Attack - Simulation to Enhance Fault Attacks & Defenses
Explore fault injection attacks on Secure Boot, their impact on embedded systems, and strategies for enhancing defenses through simulation techniques.
Checking BIOS Protections Offline With Just the Firmware Updates
Explore system firmware vulnerabilities and their impact on security. Learn about offline analysis of UEFI firmware updates to identify protection gaps and potential risks in modern systems.
How the BIOS Assures Its Handling of Inputs
Explore BIOS input handling, firmware interfaces, and analysis techniques for formal validation and vulnerability detection, including static, dynamic, and symbolic execution approaches.
Extreme Privilege Escalation on Windows 8 - UEFI Systems
Explore extreme privilege escalation techniques on Windows 8/UEFI systems, uncovering vulnerabilities in firmware interfaces and demonstrating exploitation methods for elevated system access.
Revealing Embedded Fingerprints - Deriving Intelligence - USB Stack Interactions
Techniques for analyzing USB stack interactions to gather intelligence on embedded systems, including OS identification and vulnerability exploitation challenges.
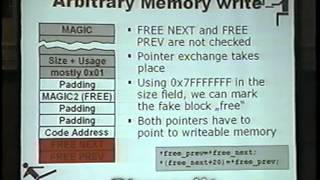
Design Issues and Software Vulnerabilities in Embedded Systems
Explore design flaws and software vulnerabilities in embedded systems, focusing on Windows 2003 environments and their security implications.