Dissecting the AMD Platform Security Processor
Explore AMD's Platform Security Processor: its role in system startup, runtime services, and memory access. Gain insights into reverse-engineering efforts and potential security implications.
The Wolf in SGX Clothing
Explore Intel SGX's security features, requirements, and potential vulnerabilities through demos, code analysis, and practical examples. Gain insights into enclave protection and potential attack vectors.
Trusted Execution Environments - A Technical Overview of Intel SGX, Arm TrustZone, and RISC-V PMP
Explore key trusted execution environments: Intel SGX, Arm TrustZone, and RISC-V PMP. Learn their architectures, security features, and implementation processes for robust data protection.
UEFI Secure Boot in U-Boot
Explore UEFI Secure Boot implementation in U-Boot, its benefits for embedded systems, and future plans. Learn about standardization efforts and improved OS distribution support.
The Open Enclave SDK - Confidential Computing with Trusted Apps
Explore Confidential Computing and Trusted Execution Environments with Open Enclave SDK, focusing on securing data in use and developing trusted applications across different TEEs.
Town Crier - An Authenticated Data Feed for Smart Contracts
Explore authenticated data feeds for smart contracts using Town Crier, leveraging Intel SGX for secure and confidential data delivery in decentralized environments.
What's New in Azure Confidential Computing
Explore Azure's latest advances in confidential computing, including VMs, containers, and a new platform service. Learn end-to-end data protection for healthcare, finance, and regulated industries.
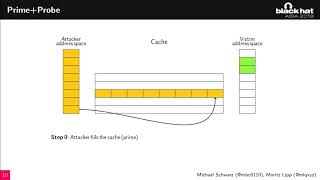
When Good Turns Evil - Using Intel SGX to Stealthily Steal Bitcoins
Explore how Intel SGX can be exploited to implement stealthy malware, extract secret RSA keys, and steal Bitcoins through cache attacks and other vulnerabilities in trusted execution environments.
Plundervolt - Flipping Bits from Software without Rowhammer
Discover Plundervolt: a software-based fault attack that threatens system security without physical access. Learn its mechanisms, potential impacts, and how it compares to Rowhammer.
CLKscrew - Exposing the Perils of Security-Oblivious Energy Management
Explore CLKSCREW attack: software-based fault attacks exploiting energy management vulnerabilities, enabling security breaches without physical access to devices or specialized equipment.
Cache Side Channel Attack - Exploitability and Countermeasures
Explore dangerous cache attacks, their characteristics, and real-world applications. Learn about exploitability, countermeasures, and key takeaways for protecting against these privacy-violating threats.
Confidential Computing in Cloud and Edge
Explore Confidential Computing in cloud and edge environments, focusing on Trusted Execution Environments, data protection, and scalable implementation solutions for enhanced security.
The Rise of Confidential Computing
Explore Trusted Execution Environments for secure data processing in public clouds, including architectures, runtimes, and tools for creating confidential computing services.
The Guard's Dilemma - Efficient Code-Reuse Attacks Against Intel SGX
Explores novel exploitation techniques against Intel SGX, demonstrating vulnerabilities in enclave code without requiring kernel privileges or crashes, even with existing randomization approaches.
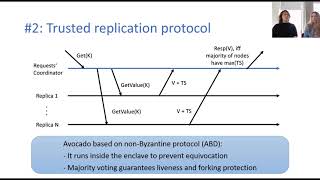
Avocado - A Secure In-Memory Distributed Storage System
Explore Avocado, a secure in-memory distributed storage system for untrusted cloud environments, offering strong security, fault-tolerance, consistency, and performance through innovative design and implementation.
FastKitten - Practical Smart Contracts on Bitcoin
Explore FastKitten, a framework for executing complex smart contracts on Bitcoin using trusted computing environments, offering efficiency and low costs for multi-round applications.
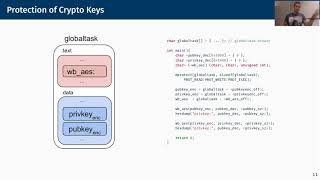
Unearthing the TrustedCore - A Critical Review on Huawei’s Trusted Execution Environment
Unveils critical security flaws in Huawei's TrustedCore, exposing vulnerabilities in trusted execution environments and demonstrating weaknesses in hardware-backed cryptography on mobile devices.
Apache Teaclave - An Open Source Universal Secure Computing Platform in Rust
Explore Apache Teaclave, a Rust-based secure computing platform using Intel SGX for privacy-sensitive data processing, supporting various tasks like machine learning and multi-party computation.
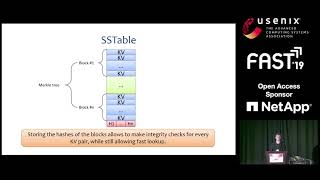
SPEICHER - Securing LSM-based Key-Value Stores Using Shielded Execution
Secure key-value storage system using shielded execution, providing confidentiality, integrity, and data freshness. Implements authenticated LSM data structure and asynchronous trusted counters for enhanced security on untrusted hosts.
Can You Trust Me Now? An Exploration Into the Mobile Threat Landscape
Comprehensive exploration of mobile security, examining hardware, software, and network components across platforms to uncover vulnerabilities and discuss protective measures for data and devices.
Hack In The Studio - Fireside Chat
Fireside chat with security experts Cristofaro Mune and Adam Laurie, discussing their extensive experience in hardware hacking, embedded systems security, and reverse engineering techniques.