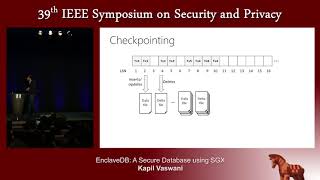
EnclaveDB: A Secure Database Using SGX
Explore EnclaveDB, a secure database engine using Intel SGX to protect sensitive data from malicious administrators and compromised systems, offering confidentiality, integrity, and freshness guarantees.
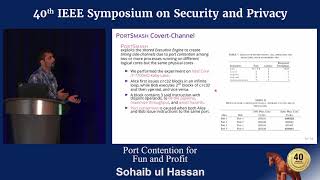
Port Contention for Fun and Profit
Explore SMT execution engine sharing as a side-channel leakage source, targeting ports to create a high-resolution timing side-channel for attacks on various architectures and applications.
Plundervolt - Software-Based Fault Injection Attacks against Intel SGX
Explore software-based fault injection attacks on Intel SGX, focusing on the Plundervolt technique that exploits voltage scaling interfaces to compromise enclave computations and cryptographic algorithms.
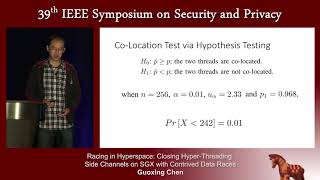
Racing in Hyperspace - Closing Hyper-Threading Side Channels on SGX
Explore techniques to mitigate Hyper-Threading side-channel vulnerabilities in Intel SGX enclaves using HYPERRACE, an LLVM-based tool that creates shadow threads and verifies physical-core co-location.
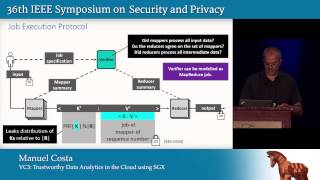
Trustworthy Data Analytics in the Cloud Using SGX
Explore trustworthy cloud-based data analytics using SGX technology. Learn about VC3, a system enabling secure MapReduce computations while preserving confidentiality and integrity of code and data.
Leaky Processors - Stealing Your Secrets With Foreshadow
Explore the Foreshadow vulnerability in modern processors and its implications for data security. Learn about potential exploits and mitigation strategies.
State of Intel SGX in Linux
Comprehensive overview of Intel SGX support in Linux, covering kernel interface, features, and confidential computing run-times. Explores the maturing SGX ecosystem and its status as a mainline kernel technology.
Introducing IO Devices into Trusted Execution Environments
Explore security and software changes for IO support in trusted execution environments, focusing on confidential computing and hardware-based TEEs like Intel SGX and TDX.
Improving Bootup Performance of Containers with Overlay Images in TEE Environments
Optimizing container bootup in TEE environments: Accelerating image downloads, reducing key negotiation overhead, and offloading image decryption for improved performance and security.
Pandora: Symbolic Validation of SGX
Explore symbolic validation techniques for Intel SGX, enhancing security in confidential computing environments.
BlindAI: Secure Remote ML Inference with Intel SGX Enclaves
Explore secure remote ML inference using Intel SGX enclaves, balancing security, privacy, and performance. Learn about BlindAI's open-source solution for confidential computing.
Trusted Computing with Rust and Intel SGX
Explore trusted computing using Rust and Intel SGX. Learn to run no_std code securely in the cloud, hidden from providers. Discover challenges and benefits of encrypted computation.
Container Runtime Support for SGX and TEE Environment
Explore Intel's container runtime support for SGX and TEE environments, enhancing security and confidentiality in cloud computing and edge deployments.
Securing Secrets in Distributed Systems Using Enclave Technology
Discover how Intel SGX technology and AppArmor safeguard cryptographic secrets across distributed ecosystems, with practical applications in 5G networks and StarlinkX use cases.
Systems & Networks Seminar - Andrew Bauman - Komodo: Using Verification to Disentangle Secure-Enclave Hardware from Software
Explores Komodo, an alternative to Intel SGX for secure enclaves, using verified software to implement isolated execution environments with improved flexibility and security guarantees.
Installing Hardware Wallet for Consortium Blockchain - Protecting Hyperledger Fabric Node Private Keys with Intel SGX
Learn to protect Hyperledger Fabric node private keys using Intel SGX technology. Explore modifications to Golang encryption library, bridging Fabric and Enclave, and implementing plugin bccsp in BaaS scenarios.
The Wolf in SGX Clothing
Explore Intel SGX's security features, requirements, and potential vulnerabilities through demos, code analysis, and practical examples. Gain insights into enclave protection and potential attack vectors.
Trusted Execution Environments - A Technical Overview of Intel SGX, Arm TrustZone, and RISC-V PMP
Explore key trusted execution environments: Intel SGX, Arm TrustZone, and RISC-V PMP. Learn their architectures, security features, and implementation processes for robust data protection.
Town Crier - An Authenticated Data Feed for Smart Contracts
Explore authenticated data feeds for smart contracts using Town Crier, leveraging Intel SGX for secure and confidential data delivery in decentralized environments.
What's New in Azure Confidential Computing
Explore Azure's latest advances in confidential computing, including VMs, containers, and a new platform service. Learn end-to-end data protection for healthcare, finance, and regulated industries.
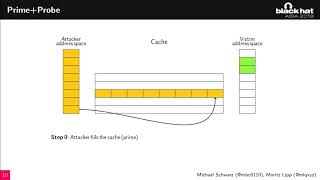
When Good Turns Evil - Using Intel SGX to Stealthily Steal Bitcoins
Explore how Intel SGX can be exploited to implement stealthy malware, extract secret RSA keys, and steal Bitcoins through cache attacks and other vulnerabilities in trusted execution environments.