When Confidential Containers Meet Arm Confidential Computing Architecture
Explore Confidential Containers' integration with Arm CCA, focusing on standardizing confidential computing for Kubernetes and leveraging TEE for enhanced container and data protection.
WASM and Confidential Computing - Securing FaaS Functions
Explore a zero-trust Serverless platform using Knative, WebAssembly, and Trusted Execution Environment to enhance security for sensitive cloud-based applications and data processing.
A WASM Runtime for FaaS Protected by TEE
Explore confidential computing with WASM runtime for FaaS protected by TEE. Learn about Inclavare, cloud-native containers, and how WASM addresses cross-platform issues in secure cloud environments.
Using WebAssembly to Run, Extend, and Secure Applications
Explore WebAssembly's evolution, security features, and applications beyond browsers. Learn to run, extend, and secure apps using WASM, WASI, and Trusted Execution Environments.
It's All About Trust - Why Confidential Computing Matters
Explore Confidential Computing's role in enhancing supply chain security, protecting sensitive data, and building trust in complex ecosystems. Learn about its implementation and open-source projects.
Device Attestation in Hardware TEE-Based Confidential Computing
Explore device attestation in confidential computing, focusing on TEE VMs verifying device authenticity for secure workload transfer and acceleration.
Confidential Computing and Privacy-Enhancing Technologies - The Landscape
Explore confidential computing and privacy-enhancing technologies for secure cloud adoption. Compare approaches, discuss open source's role, and see a demo using the Enarx project.
Confidential Computing in Azure Databricks
Explore Azure Databricks' integration with Confidential Computing, enhancing data security through hardware-based trusted execution environments and advanced VM features, with insights on future developments.
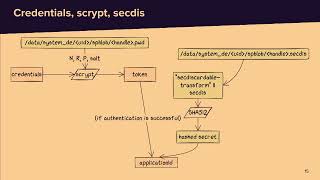
Dissecting the Modern Android Data Encryption Scheme
Explore Android data encryption, focusing on key generation, storage, and vulnerabilities. Learn about File-Based Encryption, TEE, Secure Element, and attack strategies using software vulnerabilities on Samsung A22 and Pixel 3a.
Securing Secrets in Distributed Systems Using Enclave Technology
Discover how Intel SGX technology and AppArmor safeguard cryptographic secrets across distributed ecosystems, with practical applications in 5G networks and StarlinkX use cases.
Towards the Hardened Cloud-Native Cornerstone: Container Runtime Protection
Explore advanced container runtime protection techniques, from kernel-aided to hardware-assisted solutions, addressing security risks and privacy concerns in cloud-native environments.
Systems & Networks Seminar - Andrew Bauman - Komodo: Using Verification to Disentangle Secure-Enclave Hardware from Software
Explores Komodo, an alternative to Intel SGX for secure enclaves, using verified software to implement isolated execution environments with improved flexibility and security guarantees.
Using OP-TEE as a Cryptography Engine
Explore OP-TEE's role as a cryptography engine for secure IoT data storage, covering platform setup, driver implementation, and integration with Linux and OpenSSL.
OpenFL: A Federated Learning Framework for Secure Collaborative Model Training
Explore OpenFL, a Python framework for federated learning that enables collaborative model training without sharing sensitive data. Learn its features, applications, and security benefits.
Protecting Your System from Security Threats - Linux Security Mechanisms
Comprehensive overview of Linux security mechanisms for embedded systems, covering encryption, secure boot, and integrity measures to protect against various attacks.
How ARM Systems are Booted - An Introduction to the ARM Boot Flow
Explore ARM system boot processes, from reset vector to Linux startup, covering ARM Trusted Firmware, CPU power management, and system services like PSCI and SCMI.
Shield Your Devices - The Strength of Open-Source Software and Hardware
Explore RISC-V software ecosystem and OP-TEE port, enhancing device security through open-source solutions. Learn about Trusted Execution Environments and their applications in various industries.
Installing Hardware Wallet for Consortium Blockchain - Protecting Hyperledger Fabric Node Private Keys with Intel SGX
Learn to protect Hyperledger Fabric node private keys using Intel SGX technology. Explore modifications to Golang encryption library, bridging Fabric and Enclave, and implementing plugin bccsp in BaaS scenarios.
Using Blockchain and Cryptography to Enable Privacy-preserving and Inclusive Financial Services
Explore blockchain and cryptography for privacy-preserving financial services. Learn about data renting, secure joint computation, and real-world applications in inclusive banking and targeted marketing.
The Road to Qualcomm Trust Zone Apps Fuzzing
Explore Trusted Execution Environment vulnerabilities in Qualcomm's TEE, reverse engineering techniques, and fuzzing methods for TrustZone apps in mobile device security research.
Fuzzing Embedded - Trusted Operating Systems Using AFL
Explore fuzzing techniques for Trusted Execution Environments using AFL, focusing on OP-TEE. Learn about challenges, coverage tracking, and creating initial inputs for effective embedded system security testing.