Integrating Security in Agile Projects - AppSec EU 2017
Practical guide on integrating comprehensive security programs into agile development, featuring a real-world case study and tips for organizations prioritizing security in their projects.
Do Certain Types of Developers or Teams Write More Secure Code?
Explore factors influencing secure code development, including team dynamics, developer experience, and human factors. Gain insights into improving software security practices.
Scaling Security through Context-Based Security Assessments
Streamlining security assessments through context-based automation, enabling efficient scaling and tailored workflows for product security teams in rapidly growing organizations.
Security Chaos Engineering - Turning the Tide in the War on Uncertainty in Cyber Security
Explore security chaos engineering to proactively discover system weaknesses, increase confidence in security mechanisms, and move from subjective assessment to objective measurement through continuous experimentation.
Topics of Interest: Developers Struggle with Application Security and How to Make It Better
Explore challenges in application security for developers and learn strategies to improve DevSecOps practices, drawing from real-world experiences at major tech companies.
Securing the Build and Deployment Pipeline - Challenges and Best Practices
Explore challenges in securing build/deployment environments for agile development and DevOps. Learn about potential vulnerabilities in automated processes and strategies to maintain code integrity.
Layered Threat Modeling: An Architectural Approach
Explore architectural threat modeling techniques to identify and mitigate security risks in complex systems, enhancing overall application and infrastructure protection.

vAPI: Vulnerable Adversely Programmed Interface - OWASP API Top 10
Explore and exploit API vulnerabilities using vAPI, a lab environment mimicking OWASP API Top 10 scenarios. Ideal for developers and penetration testers to understand and address common API security issues.
AppSec++ - Taking the Best of Agile, DevOps, and CI/CD into Your AppSec Program
Learn to optimize AppSec using Agile, DevOps, and CI/CD principles. Discover strategies for scaling security efforts, leveraging automation, and implementing open-source tools to enhance your application security program.
Building Your Own Large Scale Web Security Scanning Infrastructure
Learn to build, scale, and integrate a robust web security scanning infrastructure into your continuous delivery pipeline, with insights on customization and comparisons to existing solutions.
Security Automation in the Agile SDLC - Real World Cases
Explore real-world examples of implementing successful security automation in fast-paced development environments, focusing on agile methodologies, DevOps, and continuous integration for secure software delivery.
Continuous Security: Bringing Agility to the Secure Development Lifecycle
Bringing agility to secure development: Learn strategies for integrating continuous security practices into your development lifecycle, enhancing both speed and safety in software creation.
An SDLC for the DevSecOps Era
Explore an SDLC tailored for the DevSecOps era with insights on integrating security into modern development practices and organizational culture.
Everything is Terrible: Building, Configuring, and Securing Software - Three Perspectives
Explore perspectives on building, configuring, and securing software from developers, operations, and security experts. Learn strategies for collaboration, empathy, and optimizing workflows across teams.
Continuous Acceleration: Why Continuous Everything Requires a Supply Chain Approach
Explore the need for a supply chain approach in continuous development practices, emphasizing acceleration and efficiency in modern software security and delivery processes.
Bounties and the Software Development Life Cycle
Katie Moussouris explores bug bounties, vulnerability disclosure, and their integration into the software development lifecycle. She shares insights on organizational empathy, bounty program implementation, and improving application security.
Addressing Security Requirements in Development Projects
Learn effective strategies for integrating security requirements into development projects, covering artifact creation, requirement generation, filtering, and customization.
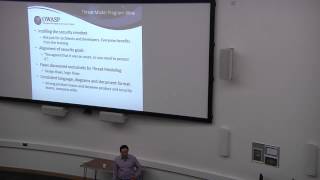
Threat Modeling - A Brief History and the Unified Approach at Intuit
Unified approach to threat modeling combining STRIDE and asset-based methods. Focuses on identifying assets, attacker profiles, and controls for software architecture and system deployments.
Introduction to the Newest Addition to the OWASP Top 10 - A9 Guidelines
Experts discuss the new OWASP A9 guideline on insecure open source libraries, offering insights on component usage, best practices, and real-world challenges in mitigating risks in agile development.
Threat Modeling Made Interactive - Using Poirot for Dynamic Security Analysis
Interactive demonstration of Poirot, a tool for modeling and analyzing system security during design phase, enabling real-time threat assessment and mitigation strategies.
AGL Instrument Cluster Expert Group Discussion
Explore AGL Instrument Cluster Expert Group's insights on functional safety, architecture, and communication mechanisms for automotive software development.