eBPF - Fueling New Flame Graphs & More
Explore eBPF's transformative impact on operating systems, performance tools, and flame graphs. Learn about its applications in major tech companies and its potential for solving complex performance issues.
From the Ground Up - How We Built the Nanos Unikernel
Explore the Nanos unikernel's architecture, security features, and memory allocation strategies. Learn about closures, concurrency, and future developments in this specialized operating system.
Sandboxing in Linux with Zero Lines of Code
Explore Linux sandboxing techniques without coding, focusing on process startup stages and practical examples. Learn to enhance security and control system calls effectively.
Inside the Linux Security Modules
Explore Linux Security Modules framework, architecture, and integration. Learn about security data fields, hooks, and configurations for enhanced kernel protection.
Zephyr RTOS Juicy Features Using Simple Evaluation Boards and Robots
Explore Zephyr RTOS features using evaluation boards and robots. Learn to write code, build applications, and implement device drivers for embedded systems and robotics projects.
Software Security Era - Past, Present, and Future
Explore the evolution of memory corruption exploitation, from early techniques to modern mitigations. Includes live demos of vulnerabilities and discusses the ongoing challenges in software security.
Ghost Tunnel 2.0 - Blue Ghost
Explore covert Bluetooth communication using Ghost Tunnel 2.0, enabling multiple secure tunnels for file transfer and command execution without detection or inspection by most protection systems.
Finding the Weak Link in Binaries
Comprehensive review of binary defenses across formats, OSs, and compilers. Learn to detect and understand modern protective mechanisms without source code access.
Exploiting a Limited UAF on Ubuntu 22.04 to Achieve LPE
Detailed exploration of exploiting a Linux kernel vulnerability in Ubuntu 22.04 to achieve local privilege escalation, focusing on advanced exploitation techniques and bypass methods.
Counterfeiting the Pipes with FakeNet 2.0 - Part 2
Learn to simulate networks for malware analysis using FakeNet 2.0. Capture network signatures, mimic protocols, and defeat malware through hands-on challenges with real-world samples.
Discovering 20 Year Old Vulnerabilities in Modern Windows Kernel
Explore how legacy components in Windows 10 can harbor decades-old vulnerabilities, focusing on printer drivers and their potential security implications.
Escaping Virtualized Containers
Explore container escape techniques and new sandboxing tools using unikernels, lightweight VMs, and userspace-kernels to enhance isolation between host and container OS.
Detecting -Un-Intentionally Hidden Injected Code by Examining Page Table Entries
Explore techniques for detecting hidden injected code through page table entry analysis, covering both intentional malware concealment and unintentional OS paging mechanisms.
Effortless, Agentless Breach Detection in the Enterprise - Token All the Things!
Discover innovative techniques for detecting network breaches using honeytokens. Learn about Canarytokens and new methods to set tripwires without agents or hardware, improving your network security.
Stop the Insanity and Improve Humanity - UX for the Win
Explore UX principles to enhance security tools, making them more user-friendly and effective for both experts and novices in the field of information security.

NrOS - Effective Replication and Sharing in an Operating System
Explores NrOS, a novel OS kernel using node replication for improved scalability and simplified development, outperforming Linux while maintaining sequential kernel simplicity.
Blue Note - How Intentional Acoustic Interference Damages Availability and Integrity in Hard Disk Drives and Operating Systems
Explores how acoustic interference can damage hard drives, causing data corruption and system failures. Presents findings on vulnerabilities and proposes mitigation strategies for legacy systems.
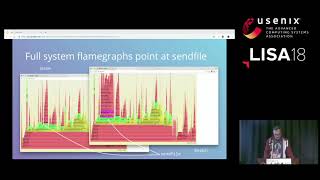
Debugging Linux Issues with eBPF
Explore eBPF for debugging Linux performance issues, focusing on a real-world case of CPU increase in Kafka after a Debian upgrade. Learn tools and techniques for operational engineers.
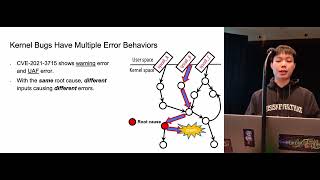
GREBE - Unveiling Exploitation Potential for Linux Kernel Bugs
Explore GREBE, a tool for assessing Linux kernel bug exploitability. Learn about its methodology, implementation, and effectiveness in identifying high-risk vulnerabilities.
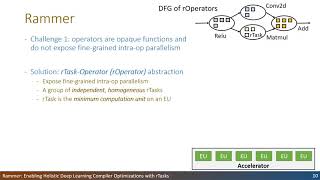
Rammer - Enabling Holistic Deep Learning Compiler Optimizations with rTasks
Optimizing DNN computation on hardware accelerators through novel abstractions and holistic scheduling, achieving significant performance improvements over existing compilers and libraries.
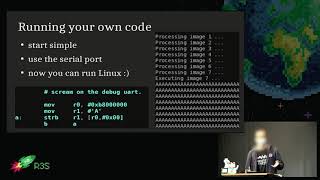
Porting Linux to Your Favorite Obscure Arm SoC
Aprenda a portar Linux para SoCs Arm obscuros: configuração, drivers, depuração de porta serial, devicetree, controladores de interrupção e temporizadores para executar versões modernas em hardware antigo.