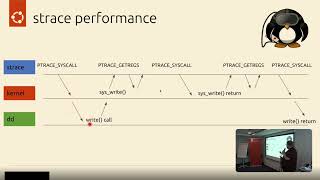
Bpftrace Recipes - 5 Real Problems Solved
Explore dynamic runtime tracing with bpftrace to solve real-world operational issues. Learn to write efficient kernel programs for analyzing and debugging complex system problems without modifying software or impacting performance.
Emulating NT Synchronization Primitives in Wine
Explore a proposed kernel driver solution to enhance Wine's performance by emulating NT synchronization primitives, potentially doubling speed for multithreaded applications like modern games.
Advancing Kernel Control Flow Integrity with eBPF
Explore eBPF's potential in enhancing kernel security through control flow integrity. Learn about challenges, implementation techniques, and performance optimization for improved kernel protection.
Sysarmor: Meta's eBPF Security Detection and Enforcement Tool
Explore Meta's Sysarmor: an eBPF-based security daemon for threat detection and rule enforcement in high-risk environments, featuring efficient in-kernel evaluation and innovative approaches to process and container monitoring.
DL Server: Scheduling SCHED_DEADLINE for Entire Schedulers
Exploring SCHED_DEADLINE for scheduling entire schedulers, focusing on CFS and FIFO task prioritization, deferrable servers, and implementation challenges in Linux kernel scheduling.
Overflowing the Kernel Stack with BPF - Security Implications and Mitigations
Exploring vulnerabilities in eBPF's kernel stack usage, demonstrating overflow scenarios through program attachment and nesting, and discussing mitigation strategies for runtime environment assumptions.
Evolving the BPF Type Format
Exploring enhancements to BPF Type Format: separating kernel BTF, explicit matching, standalone BTF, and auto-detecting features to improve adoption and functionality across systems.
Verifying the Verifier - eBPF Range Analysis Verification
Automated tool Agni checks eBPF verifier's range analysis correctness, extracts semantics from kernel source, and synthesizes programs to expose potential bugs in older kernel versions.
Callsite Trampolines for Memory Allocation Profiling
Exploring compiler support for instrumenting call sites to store additional data, focusing on memory allocation profiling and its implications for Linux kernel development.
BPF_LSM and fsverity for Binary Authorization
Flexible binary authorization solution using BPF_LSM and fsverity for enhanced system security. Combines file integrity checksums, secure signing, and access control enforcement.
BPF for Security and LSM Updates
Explore BPF LSM advancements, including static calls, xattr operations, and security applications. Learn about challenges and future developments in kernel-level security.
eBPF-based Kubernetes Security
Explore cutting-edge eBPF technology for enhancing Kubernetes security, offering advanced protection and monitoring capabilities for cloud-native environments.
Enhancing Observability in Cloud-Based Educational Linux Lab Environment
Explore eBPF-based solutions for enhancing observability in cloud-based Linux lab environments, focusing on real-time resource monitoring and user behavior insights with minimal performance impact.
Compute Express Link (CXL) - Overview and Linux Development Status
Explore Compute Express Link (CXL), a new interconnect specification, its features, and Linux community developments. Gain insights into CXL's potential and current progress in Linux integration.
Thermal Kernel-User Notification Issues with Netlink
Explores challenges with Netlink for thermal notifications in Linux, discussing issues like system freezes during event storms and increased memory usage, impacting system stability and performance.
DTrace and eBPF: New Challenges - Pitfalls and Solutions
Explore technical challenges and creative solutions in Linux kernel tracing, focusing on DTrace and eBPF implementation pitfalls and potential improvements for enhanced system observability.
16K Page Size Support in Android - Performance and Challenges
Explore Android's move to larger base page sizes, including performance benefits, current status, and challenges in implementing 16k page size support for mobile applications.
Simplifying Livepatch Callbacks, Shadow Variables, and State Handling
Propuesta para mejorar el manejo de callbacks, variables shadow y estados en livepatches de Linux. Unifica estos elementos, simplifica su uso y resuelve problemas de compatibilidad entre parches acumulativos.
Zephyr Project Growth, Long Term Support, and Linux Interoperability
Explore Zephyr's rapid growth, key features, and IoT ecosystem integration. Learn about LTS transitions and future prospects for Linux-Zephyr interoperability in various applications.
Hypervisor-Enforced Kernel Integrity for KVM
Enhancing Linux kernel security through KVM-based protection mechanisms, offering improved defense against vulnerabilities and discussing new features for mainline integration.
A move_pages() Equivalent for Physical Memory
Proposal for a syscall to migrate physical memory contents between NUMA nodes, exploring integration with mm/migrate.c and potential applications in tiering frameworks.