Worms That Turn - Nematodes and Neotodes
Explore the evolution of computer worms, from early nematodes to modern neotodes, and their impact on cybersecurity in this intriguing conference talk.
Project Calico Network Policies
Explore Project Calico's network policies for Kubernetes, enhancing security and control in cloud-native environments.
Network Security at Scale: L3 Through L7 at Splunk
Explore Splunk's multi-cloud network security architecture, from VPCs to Istio, addressing scalability, agility, and security challenges across L3 to L7 layers.
Identity Based Segmentation for Zero Trust Architecture
Explore Zero Trust Architecture implementation using identity-based segmentation, focusing on cloud-to-premises communication through DMZs with identity-aware proxies and service mesh.
Demystifying Zero-Trust for Cloud Native Technologies
Explore zero-trust principles for cloud-native environments, covering identity, policy, continuous assessment, and security. Learn implementation guidelines for protecting users, devices, networks, applications, and data.
Air Gap: A Short Introduction and Why It Isn't Complicated
Discover the simplicity of Air Gap technology in this concise introduction, demystifying its concepts and applications for easy understanding.
Vanquishing Vulnerabilities - Preparing for Critical CVEs
Prepare for critical vulnerabilities with tools and practices for container image scanning, policy enforcement, network control, runtime configurations, and behavior monitoring.
Unveiling the Hidden - Discovering RDP Vulnerabilities Using PDF Files
Innovative OSINT techniques reveal critical RDP vulnerabilities, including remote code execution and security bypasses, without conventional reverse engineering tools. Explore unconventional research methodologies and vulnerability analysis.
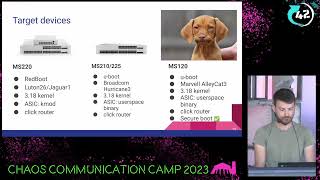
Defeating Planned Obsolescence for Cisco Meraki Switches - Open-Source Firmware Development
Explore open-source firmware development for Cisco Meraki switches, covering hardware insights, stock firmware analysis, and future prospects for extending device lifespan.
Introduction to Zero Trust Networking and Infrastructure Access with Twingate
Explore Zero Trust Networking and secure infrastructure access with Twingate. Learn why VPNs fall short for IaC and discover innovative solutions for DevOps and IT teams, including Kubernetes integration.
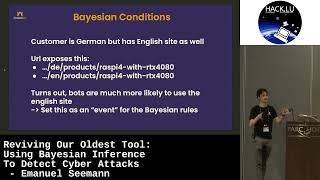
Using Bayesian Inference to Detect Cyber Attacks
Explore Bayesian inference techniques for detecting cyber attacks, enhancing your ability to identify and respond to security threats in real-time.
Open Wounds: The Last 5 Years Have Left Bluetooth to Bleed
Explore critical Bluetooth vulnerabilities from the past 5 years, their impact on device security, and potential mitigation strategies in this eye-opening cybersecurity analysis.
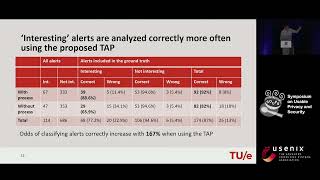
Synthesis and Evaluation of a Network Threat Analysis Process for Tier 1 SOC Investigations
Evaluation of a structured 4-stage threat analysis process for SOC tier-1 analysts, showing improved accuracy and discussing implications for security operations.
Envoy Gateway End User Threat Model Report: Raising Awareness of Gateway API Security
Explore Envoy Gateway's security through a threat-driven analysis, providing insights for confident deployment as an edge proxy in Kubernetes clusters.

ACME - Benefits of an Internet Security Protocol in Your Network
Explore the advantages of implementing ACME protocol for enhanced network security, focusing on its practical applications and impact on internet safety.
Remotely Exploiting the ClamAV Antivirus Engine - CVE-2023-20032 Case Study
Explore a case study on exploiting CVE-2023-20032 in ClamAV, demonstrating remote code execution and ASLR bypass techniques applicable to similar antivirus software vulnerabilities.
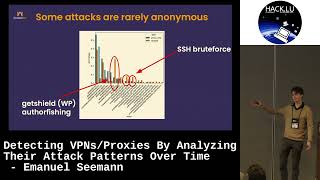
Detecting VPNs and Proxies by Analyzing Attack Patterns Over Time
Explore techniques for identifying VPNs and proxies through analysis of their attack patterns, enhancing network security and threat detection capabilities.
How NTLM Relay Ruins Your Exchange Servers
Uncovers a critical NTLM relay attack surface in Exchange Server, affecting mailbox security and potentially leading to RCE. Explores vulnerabilities, exploits, patches, and protection strategies for Exchange environments.
Lazarus Group's Undercover Operations in South Korea 2022-2023
Detailed analysis of Lazarus Group's recent cyber campaigns in South Korea, covering infiltration methods, lateral movement techniques, and data exfiltration strategies used by this sophisticated threat actor.
Bluetooth Sniffing: Privacy Implications and Unexpected Findings
Exploring Bluetooth sniffing implications: privacy, security, and societal impacts. Insights on device tracking, medical data, law enforcement, and potential vulnerabilities in various Bluetooth-enabled systems.
Design and Implementation of a Security Architecture for Critical Infrastructure Industrial Control Systems
Comprehensive security architecture for critical infrastructure, addressing nation-state cyber threats. Covers hardware roots of trust, secure boot, and integrity measures across various systems and networks.