Bug Bounty Recon: Bypassing Geographic DNS with Ensemble
Discover how Ensemble revolutionizes bug bounty hunting by bypassing GeoDNS limitations, enabling comprehensive scanning across multiple geographic regions through a distributed cluster of nodes and user-friendly web interface.
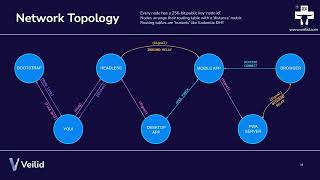
The Internals of Veilid - A New Decentralized Application Framework
Explore the architecture and capabilities of Veilid, an open-source P2P framework enabling secure messaging and decentralized applications through private routing, strong encryption, and cross-platform compatibility.
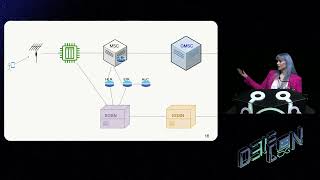
Evolution of Cellular Networks: From 2G to 5G - Understanding Attack Surfaces and Security
Explore the evolution of cellular networks from 2G to 5G, understanding network vulnerabilities, attack surfaces, and security mitigations across each generation of mobile telecommunications.
Smashing the State Machine: Advanced Web Race Condition Attacks
Discover advanced web race-condition attack techniques, from limit-overrun exploits to state machine manipulation, with practical methodologies and tools for identifying and exploiting vulnerabilities.
Unparalleled RDP Monitoring to Reveal Attackers' Tradecraft
Dive into advanced RDP attack monitoring techniques and threat actor behaviors through a unique D&D-themed analysis of cybersecurity tradecraft and defensive strategies.

Private Keys in Public Places - Finding and Exploiting Hidden Encryption Keys
Uncover techniques for finding hidden private keys, certificates, and encryption keys in firmware, with real-world examples from Netgear, Fortinet, and Dell's security vulnerabilities.
The Importance of Arts and Crafts in ThreatOps - Effective Visual Communication for Cybersecurity Analysis
Master effective visualization techniques for cybersecurity incidents and threat intelligence, enhancing your ability to communicate complex security concepts through clear, standardized diagrams.
Turning Virtual Wallets into Skimming Devices - Security Vulnerabilities in MPOS Solutions
Uncover security vulnerabilities in mobile payment systems and MPOS devices, exploring real-world examples of credit card skimming, Bluetooth tampering, and hardware exploitation techniques.
Malware Design: Abusing Legacy Microsoft Transports and Session Architecture
Explore advanced malware design techniques and covert communication frameworks, focusing on Windows architecture exploitation and maintaining persistent access while evading detection systems.
Leveraging macOS Networking Frameworks to Heuristically Detect Malware
Discover advanced techniques for detecting macOS malware through network monitoring, exploring low-level APIs, private frameworks, and user-mode extensions for comprehensive threat detection.
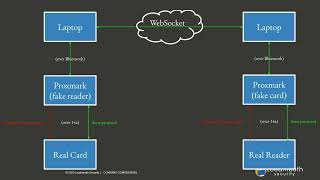
Unlocking Doors Through Long-Range Relay Attacks on Contactless Credentials
Discover how to execute long-range relay attacks on contactless credentials through ISO 14443A protocol vulnerabilities, including live demonstrations and practical mitigation strategies.
Exploiting Wireless Side Channels in EV Charging Systems - Security Vulnerabilities in CCS and NACS
Explore wireless security vulnerabilities in EV charging systems, focusing on CCS technology, eavesdropping risks, and potential attack vectors through power-line communication signals.
Hacking Power Management in Data Centers - Security Vulnerabilities and Exploits
Delve into data center power management security, exploring vulnerabilities in PDUs and DCIM systems while learning critical infrastructure protection strategies and attack vectors.
Spooky Authentication at a Distance - Post-exploitation Techniques for Windows Environments
Discover innovative post-exploitation techniques for proxying Windows authentication protocols remotely, enabling user impersonation and domain control without elevated privileges.
Defending KA-SAT: Analysis and Response to the 2022 Cyberattack
Delve into the forensic analysis and defense strategies of the 2022 KA-SAT network cyberattack, exploring malware deployment tactics, network-based attacks, and rapid incident response techniques used to protect satellite communications.
Breaking into Secure Facilities with OSDP - Vulnerabilities and Exploitation Techniques
Uncover critical vulnerabilities in OSDP security protocols and learn practical exploitation techniques for bypassing encrypted RFID systems through demonstrated pentesting tools and methodologies.
Death by 1000 Likes - Social Media Security Analysis at DEF CON
Explore how security researchers scraped r/defcon subreddit data to create an online version of the Wall of Sheep, revealing insights about information leakage in the security community.
Automatic Exploitation of TLS Certificate Validation Vulnerabilities
Explore TLS certificate validation vulnerabilities and their automated exploitation using certmitm, featuring real-world attacks on iOS and Windows 11 systems.
Nine Years of Overlooked MikroTik Pre-Authentication Remote Code Execution Vulnerabilities
Delve into RouterOS's overlooked attack surfaces and discover critical pre-auth RCE vulnerabilities that affected MikroTik devices for 9 years, with insights on detection methodology and security patterns.
Hacking PBX and UC Systems: Attack Surface Analysis and Vulnerability Discovery
Dive into enterprise PBX/UC system vulnerabilities, exploring attack surfaces, Java Runtime exploitation, PHP decryption, and shell access techniques in communication infrastructure.
Exploiting Cloud Connectivity to Compromise Network-Attached Storage Devices
Uncover critical security vulnerabilities in NAS devices through cloud connectivity exploitation, focusing on WD and Synology systems' authentication weaknesses and remote access vulnerabilities.