Private Resource Allocators and Their Applications
Introduces private resource allocators to prevent allocation-based side-channel attacks in systems like anonymous messaging, with various constructions offering different privacy guarantees and trade-offs in efficiency.
NetCAT - Practical Cache Attacks from the Network
Reverse engineering DDIO to demonstrate NetCAT, a network-based cache attack enabling remote keystroke timing attacks and covert channels, highlighting security risks in modern Intel processors.
Message Time of Arrival Codes - A Fundamental Primitive for Secure Distance Measurement
Explores secure Time-of-Arrival measurement through Message Time of Arrival Codes, addressing attacks on proximity verification systems and discussing performance-security tradeoffs in signal modulation techniques.
Staying Secure and Unprepared - Understanding and Mitigating the Security Risks of Apple ZeroConf
Explore security risks in Apple's ZeroConf systems, uncovering vulnerabilities in popular apps and services. Learn about innovative protection techniques, including voice-based certificate verification.
Key Confirmation in Key Exchange - A Formal Treatment and Implications for TLS 1.3
Formal treatment of key confirmation in key exchange protocols, focusing on TLS 1.3. Explores security definitions, implications for protocol design, and practical applications in cryptographic systems.
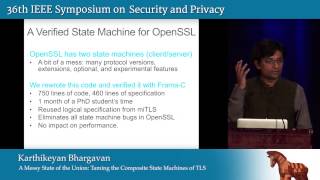
A Messy State of the Union - Taming the Composite State Machines of TLS
Explore critical security vulnerabilities in TLS implementations, including the FREAK flaw, and learn about a verified composite state machine for OpenSSL that addresses these issues.
How to Setup Your Terminal for Penetration Testing
Automate penetration testing methodology using Linux utilities and custom ZSH plugins. Learn to set up an efficient terminal environment for enhanced cybersecurity workflows.
HackTheBox Curling - Walkthrough
Comprehensive walkthrough for pwning Curling on HackTheBox, covering scanning, exploiting Joomla vulnerabilities, and gaining system access.
KRACK Attack Proof of Concept on Android and Linux Devices
Demonstration of KRACK Attack Proof of Concept on Android/Linux devices, including installation, configuration, and testing steps for this Wi-Fi security vulnerability.
LevelUp 0x04 - Blueprint for Becoming a Penetration Tester
Blueprint for aspiring pen testers: expert insights, career tips, and actionable steps to enter the field of ethical hacking and penetration testing.
LevelUp 0x04: Advanced Bug Bounty Techniques - Day 2
Explore advanced bug bounty techniques and strategies with industry experts in this comprehensive cybersecurity event focused on enhancing hacking skills and knowledge.
LevelUp 0x04 - Introduction to Ethical Hacking and Bug Bounty - Day 1
Explore cutting-edge cybersecurity insights and strategies at this free conference, featuring expert talks and discussions on the latest industry trends and challenges.
Bug Bounty Hunting Methodology - Jason Haddix from Bugcrowd's LevelUp
Comprehensive web hacking methodology covering reconnaissance, scanning, and exploitation techniques for bug bounty hunters and security researchers.
Log4Shell Vulnerability - Bugcrowd Security Flash
Explore the critical Log4Shell vulnerability, its impact, and mitigation strategies in this concise security briefing from Bugcrowd's expert.
Your Guide to Burp Suite - Setup and Usage in 30 Minutes
Learn to set up and effectively use Burp Suite for web security testing in under 30 minutes, covering essential features and functionalities.
Finding and Exploiting Hidden Functionality in Windows DLLs - LevelUpX Series 14
Explore hidden Windows DLL functionality, common bug patterns, and exploitation techniques for bug bounty hunters. Learn tools and methods to uncover vulnerabilities in web servers and network services.
Recon Sunday with Top HackerOne Paid Hackers - Dawgyg, Mayonaise, and cdl
Live hacking event featuring top-paid hackers Dawgyg, Mayonaise, and cdl discussing reconnaissance techniques and strategies for bug bounty hunting on HackerOne's platform.
OSCP, Deserialization Bugs, Shodan Tips, and Becoming an MVH - Interview with SMSecurity
Insightful discussion on OSCP certification, deserialization vulnerabilities, Shodan techniques, and achieving Most Valuable Hacker status, offering valuable insights for aspiring cybersecurity professionals.
Monitoring Endpoints, Binary Exploitation, and Continuous Recon - Security Discussion
Explore endpoint monitoring, binary exploitation, and continuous reconnaissance with insights from @Mrtuxracer. Gain valuable knowledge on advanced cybersecurity techniques and strategies.
Recon Methodology for Consistent High-Value Bug Bounties - Interview with Th3G3nt3lman
Discover effective recon methodologies for high-value bug bounties. Learn from @Th3G3nt3lman's experience in GitHub reconnaissance, tool usage, and collaboration strategies for successful hacking.
Developing crtndstry - A Tool for Finding Root Subdomains - Live Coding and Explanation
Live coding session demonstrating the creation of crtndstry, a tool for discovering root subdomains. Gain insights into the developer's thought process and learn practical cybersecurity techniques.