Christmas Hancitor Malware Campaign Analysis
Dive into a detailed analysis of the Christmas Hancitor malware campaign, exploring its infection chain, delivery methods, and technical characteristics.
Exploring IPFS Threats
Explore potential security vulnerabilities and threat landscapes within the InterPlanetary File System (IPFS) protocol through expert analysis and real-world examples.
SIERRA - Automating and Scaling Forensic Investigations at Siemens CERT
Discover how Siemens CERT automates and scales digital forensic investigations through SiERRA, exploring practical approaches to handling large-scale security incidents efficiently.
Better Breach Detection With Deception Inception - Using Honeypots
Discover advanced breach detection techniques through deceptive honeypot strategies and learn how to implement effective security measures for enhanced threat identification.
SOC Analyst's Arsenal - Essential Tools, Tips and Tricks for Effective Investigations
Master essential tools and investigative techniques for SOC analysis, featuring proven tips and tricks to enhance security incident response and threat detection capabilities.
Getting Ahead of the Bad Guys with Internet Scanning Data
Discover how to leverage internet scanning services like Shodan and BinaryEdge to identify adversarial infrastructure, detect threats early, and enhance defensive capabilities through practical hunting techniques and real-world examples.
Easy EASM - The Zero-Dollar Attack Surface Management Tool
Discover how to implement Easy EASM, a zero-cost tool for automated external asset discovery and monitoring, featuring daily Slack/Discord alerts and comprehensive asset tracking capabilities.
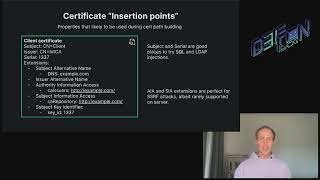
mTLS: When Certificate Authentication Goes Wrong - Security Implementation Vulnerabilities
Dive into novel attacks on mTLS authentication systems, exploring implementation vulnerabilities, exploitation techniques, and secure coding practices for certificate-based authentication.
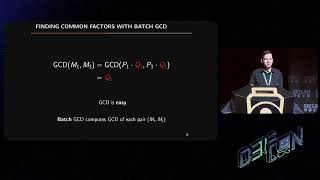
Assessing Security of Digital Certificates at Scale
Discover tools and techniques for identifying weak digital certificates at scale through network monitoring, scanning, and mathematical testing to detect security vulnerabilities in RSA public keys.
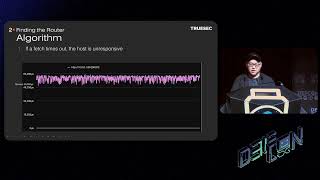
Clocks Have Ears - Timing and Browser-Based Local Network Port Scanner
Discover how browser-based timing attacks can be used for local network port scanning, exploring innovative security techniques and network vulnerability assessment methods.
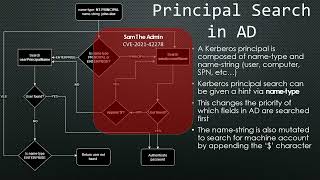
Abusing Mixed Vendor Kerberos Stacks - Exploiting Windows AD and Linux Authentication
Discover security vulnerabilities in mixed Kerberos environments and learn how to exploit weaknesses between Windows Active Directory and Linux/Unix systems for privilege escalation.
Inside Dash Cam Custom Protocols and Security Vulnerabilities
Delve into comprehensive security analysis of network-connected dash cams, exploring vulnerabilities in boot processes, custom protocols, and configuration systems across multiple international manufacturers.
Exposing Security Vulnerabilities in Large Off-Grid Solar Systems
Uncover critical security vulnerabilities in solar management systems and their potential impact on national infrastructure through real-world exploitation examples and risk analysis.
Compromising Electronic Loggers and Creating Truck-to-Truck Worm - Security Vulnerabilities in ELD Systems
Discover critical security vulnerabilities in Electronic Logging Devices (ELDs) and their implications for truck network security, from reverse engineering to proof-of-concept attacks and industry-wide security reforms.
Exploiting Security Vulnerabilities in Microhard Radio Equipment
Uncover critical security vulnerabilities in Microhard's radio equipment, including command injections and buffer overflows, while exploring implications for SCADA and utility systems.
HL7Magic: Medical Data Hacking and Security Testing Tool
Discover how to intercept and analyze HL7 medical device communications using HL7Magic, a new security testing tool designed to identify vulnerabilities in healthcare data transmission systems.
Ghost On The Wire
Explore cutting-edge virtual reality security concepts and challenges through expert insights from DEF CON 31's DCGVR Village presentation on digital vulnerabilities.
From Theory to Reality: Demonstrating SPARTA Techniques Through Ground Infrastructure Attacks
Discover how to exploit space mission vulnerabilities through ground infrastructure attacks, focusing on SPARTA techniques and man-in-the-middle exploits for spacecraft communications.
Finding Zero-Day Vulnerabilities in Vilo Home Routers - Security Research Process and Discoveries
Discover how student researchers uncovered 9 zero-day vulnerabilities in Vilo routers through hardware hacking, firmware analysis, and cloud infrastructure investigation, highlighting IoT security challenges.

Hacking Millions of Modems and Investigating Modem Security Vulnerabilities
Dive into a real-world investigation of modem vulnerabilities, ISP security flaws, and the concerning centralization of broadband infrastructure through a personal hacking incident analysis.
Dysfunctional Unity: Medical Device Security and Hospital Network Vulnerabilities
Explore critical vulnerabilities in medical devices and hospital networks, examining security challenges, SBOM misconceptions, and strategies for creating more secure healthcare environments.