A Practical Attack Against MDM Solutions
Unveiling spyphone attacks: A proof-of-concept technique bypassing mobile malware detection and MDM features, demonstrating vulnerabilities in mobile security and surveillance risks.

Uncovering Persistence with Autoruns and Security Onion
Discover techniques for identifying persistent threats using Autoruns and Security Onion. Learn to uncover hidden malware and enhance your network defense capabilities.
Defender-Pretender - When Windows Defender Updates Become a Security Risk
Explore Windows Defender's architecture, signature database, and update process. Learn about a critical 0day vulnerability affecting Windows and Microsoft 365 Defender, posing risks to enterprise machines.
Nothing but Net - Leveraging macOS's Networking Frameworks to Heuristically Detect Malware
Explore macOS network frameworks for malware detection, focusing on unauthorized access and traffic analysis techniques to enhance security on Apple systems.
Life Cycle and Detection of an Exploit Kit
Explore the lifecycle and detection methods of exploit kits, including their behavior, payload delivery, and evasion techniques. Learn about smart phishing and defensive strategies.
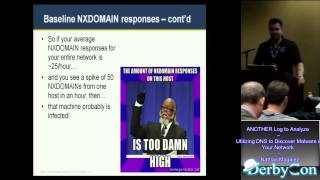
Utilizing DNS to Discover Malware in Your Network
Discover malware in your network using DNS logs. Learn defensive techniques, identify malicious traffic, and analyze anomalous domain names with practical tools and case studies.
Another Log to Analyze - Utilizing DNS to Identify Malware
Explore DNS logs to identify malware, analyze network traffic, and detect anomalous domain names. Learn defensive techniques and tools for effective malware detection and attribution.
Utilizing DNS to Detect Malware in Your Network
Explore DNS-based malware detection techniques, including packet captures, defensive strategies, and tools like dnstop and PassiveDNS. Learn to analyze network traffic for enhanced cybersecurity.
201 Ways to Identify Malware on a System
Comprehensive guide on malware detection techniques, covering various methods to identify and analyze malicious software on computer systems.
ZitMo NoM Clientless Android Malware Control
Explore clientless Android malware control techniques, focusing on ZitMo NoM, and learn about potential threats and defense strategies in mobile security.
Analyzing the Entropy of Document Hidden Code
Explore techniques for analyzing document hidden code entropy, including methodology, entropy calculation, and strategies to detect and decode malicious VBA in documents.
Credential Assessment Mapping Privilege Escalation at Scale
Explore credential assessment mapping and privilege escalation techniques for enhanced cybersecurity. Learn from major breaches and industry responses to improve defensive strategies.
The 3 Way16 Hardy Har Har Har Har File Collection and Analysis for Malware
Explore HAR file collection and analysis techniques for malware detection, focusing on innovative approaches to enhance cybersecurity and threat intelligence.
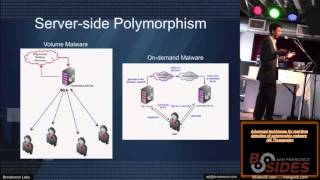
Advanced Techniques for Real Time Detection of Polymorphic Malware
Advanced techniques for real-time detection of polymorphic malware, focusing on challenges like volume and metamorphism. Explores optimization strategies and evaluates effectiveness of current methods.
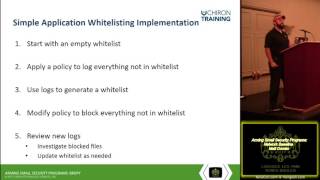
Arming Small Security Programs - Network Baseline - Matt Domko
Learn to establish network baselines for small security programs, covering malware detection, logging, and traffic analysis using tools like Bro and Security Onion.
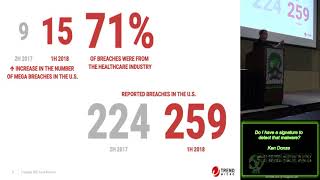
Do I Have a Signature to Detect That Malware
Explore malware detection techniques, signature-based approaches, and modern challenges in cybersecurity. Learn about monitoring processes, machine learning models, and sandbox customization for effective threat analysis.
Identify Malware on Compromised Files and URLs Using the PolySwarm Autopsy Plugin
Discover efficient malware detection using PolySwarm's Autopsy plugin. Learn to identify threats with hash lookups and file scans, leveraging 50+ specialized engines for enhanced cybersecurity.
Charla: Detección automatizada de archivos maliciosos en el repositorio PyPI
Detección automatizada de malware en PyPI: vectores de ataque, sistema de detección integrado, tipos de chequeos implementados y cómo combatir amenazas en el repositorio.
Bad Actors vs Our Community - Detecting Software Supply Chain Attacks
Explore techniques used by bad actors in software supply chain attacks and learn about a large-scale vetting system for detecting malware in Python packages.
Dynamic Image Scanning Through System Tracing
Explore dynamic scanning for detecting sophisticated malware through system tracing. Learn about behavioral patterns, open-source tools, and comparisons with static scanning and runtime security.
Tick Tock - Building Browser Red Pills from Timing Side Channels
Exploring browser-based red pills to detect virtual environments, their impact on web malware scanners, and potential mitigations for enhanced cybersecurity.