Fuzzing Closed Source Applications
Explore techniques for fuzzing closed source applications to uncover vulnerabilities and improve security. Learn practical approaches to test proprietary software without access to source code.
Fuzzing File Systems via Two-Dimensional Input Space Exploration
Explores innovative fuzzing technique for file systems, addressing challenges in input space exploration, operation generation, and bug reproduction. Introduces JANUS, a feedback-driven fuzzer with improved efficiency and reproducibility.
All Your -Data-base Are Belong To Us
Explore vulnerability research in office applications through fuzzing, code review, and reverse-engineering. Learn to discover and exploit zero-days, with insights on binary exploitation for curious researchers.
Into the Core - In-Depth Exploration of Windows 10 IoT Core
Explore Windows 10 IoT Core internals, security features, attack surfaces, and assessment methods. Learn to secure IoT devices and understand their role in the evolving Internet of Things landscape.
Hunting Windows Desktop Window Manager Bugs
Exploring Windows Desktop Window Manager vulnerabilities, focusing on DirectComposition UserSpace. Covers architecture, attack surfaces, and specific CVEs, offering insights into bug hunting techniques and security implications.
Beyond the Tip of the Iceberg - Fuzzing Binary Protocol for Deeper Code Coverage
Explore advanced fuzzing techniques for binary protocols, enhancing code coverage and uncovering vulnerabilities in network applications and file systems.
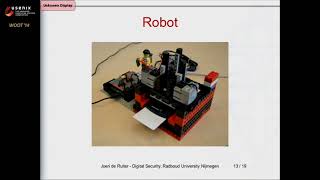
Automated Reverse Engineering Using Lego
Innovative use of Lego robots for automated reverse engineering of smartcard readers, revealing security vulnerabilities through state machine learning and fuzzing techniques.
UTOPIA - Automatic Generation of Fuzz Driver Using Unit Tests
Explore automatic fuzz driver generation using unit tests with UTOPIA, enhancing software testing efficiency and effectiveness for improved security and reliability.
Fuzzing the Native NTFS Read-Write Driver - NTFS3 - in the Linux Kernel
Explore advanced fuzzing techniques for the NTFS3 driver in Linux, focusing on context-aware methods to efficiently identify vulnerabilities in this complex subsystem.
Fuzzing - Finding Your Own Bugs and 0days
Aprenda a criar e usar um fuzzer para encontrar bugs e vulnerabilidades, incluindo técnicas para escrever exploits e obter acesso a sistemas. Demonstrações práticas incluídas.
Fuzzing Javascript Engines for Fun and Pwnage
Discover methods for finding vulnerabilities in Javascript Engines through fuzzing techniques, including crash classification, parallel fuzzing, and custom pattern generation for enhanced web browser security.
Fuzzing the Windows Kernel
Explore Windows kernel fuzzing architecture, from test-case generation to crash collection. Learn about distributed fuzzing design for effective scaling in this insightful presentation on kernel security.
When Fuzzing Meets SAP Network Services
Exploring fuzzing techniques for SAP network services, overcoming challenges in performance, protocol complexity, and crash reproduction to discover critical vulnerabilities in custom network protocols.

Fuzzing and Exploiting Virtual Channels in Microsoft Remote Desktop Protocol for Fun and Profit
Explore coverage-based fuzzing of RDP client virtual channels, targeting complex functionalities like Sound, Graphics, USB, and Filesystem to uncover potential vulnerabilities and crashes.
OpenStack API Security Testing Automation in Action
Automated security testing framework for OpenStack API, integrating with Agile and CI/CD. Demonstrates Rackspace's approach to detect vulnerabilities efficiently, improving consistency and auditability.
T-Fuzz - Fuzzing by Program Transformation
Innovative fuzzing technique that removes input checks to explore deeper code paths, improving bug discovery in software. Combines program transformation with symbolic execution for effective results.
Angora - Efficient Fuzzing by Principled Search
Innovative fuzzing technique combining mutation-based speed with high-quality input generation, outperforming existing fuzzers in bug detection and branch coverage through advanced constraint-solving methods.
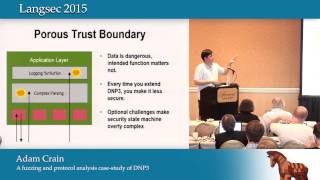
A Fuzzing and Protocol Analysis Case-Study of DNP3
Explores vulnerabilities in DNP3, a key SCADA protocol for power systems, revealing design flaws and implementation gaps. Discusses fuzzing results, CVEs, and analyzes the protocol's security addendum.
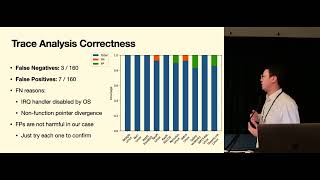
IRQDebloat - Reducing Driver Attack Surface in Embedded Devices
Explore techniques to reduce attack surfaces in embedded device drivers through IRQ debloating, binary analysis, and fuzzing. Learn about challenges, implementation, and evaluation methods.
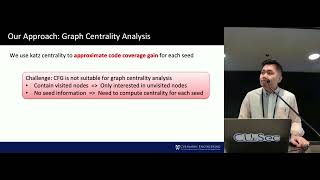
K-Scheduler - Effective Seed Scheduling for Fuzzing with Graph Centrality Analysis
Explore effective seed scheduling for fuzzing using graph centrality analysis, enhancing software testing efficiency and vulnerability detection.
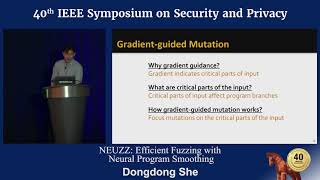
NEUZZ - Efficient Fuzzing with Neural Program Smoothing
Innovative fuzzing technique using neural networks to approximate program behavior, enabling more efficient bug discovery and higher code coverage in software testing.