Fuzzing in Go
Explore Go 1.18's built-in Fuzzing capability for automated randomized testing. Learn to implement Fuzzing, detect security flaws, and enhance defense-in-depth for internet-exposed services.
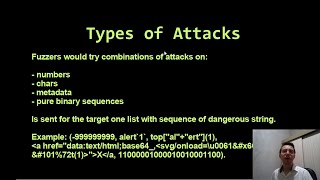
Fuzzing - Finding Your Own Bugs and Zero-Days
Master the art of fuzzer creation and vulnerability discovery, exploring buffer overflow exploitation techniques with hands-on demonstrations and practical exploit development strategies.
QuickShell: Remote Code Execution Attack Chain Analysis in Quick Share
Uncover critical security vulnerabilities in Google's Quick Share protocol, including an RCE attack chain, HTTPS MITM techniques, and protocol analysis for both Windows and Android platforms.
Snapshot Fuzzing with WTF Fuzzer - Techniques and Implementation
Master snapshot fuzzing with WTF Fuzzer. Configure Hyper-V, use Windbg and Bdump.js for snapshotting, develop harnesses, and fuzz C programs. Enhance your software security skills through hands-on practice.
Generating Conforming Programs with Xsmith
Explore Xsmith, a Racket library for efficient fuzz testing of programming languages. Learn to create conforming programs for differential testing with minimal code, finding bugs in various language implementations.
Fuzzing the Erlang Ecosystem
Explore Erlfuzz, an open-source tool for generating random Erlang programs to test compilers and tools. Learn its workings, bug detection techniques, and applications in the Erlang ecosystem.
How to Fuzz Your Way to Android Universal Root: Attacking Android Binder
Entdecken Sie Techniken zur Ausnutzung von Android Binder-Schwachstellen für Root-Zugriff durch Fuzzing-Methoden und Sicherheitsanalyse.
Perun: Keep Your Project's Performance Under Control
Explore Perun, an open-source tool for managing project performance. Learn to detect issues, analyze changes, and generate inputs to uncover potential vulnerabilities.
High-Assurance Go Cryptography
Explore techniques for ensuring safety and bug-free implementation of cryptography in Go, including testing, fuzzing, static analysis, formal proofs, and code generation. Learn about safe interfaces and readability in standard libraries.
Uncover Unknown Bugs With Fuzzing in Go
Explore Go's built-in fuzzing support to detect security vulnerabilities early in development. Learn how to implement fuzz testing for safer, more robust code in production environments.
Security Threat Model Analysis and Protection Practice in Edge Computing
Análisis de modelos de amenazas y prácticas de protección en computación de borde, incluyendo auditoría de seguridad de KubeEdge, iniciativas de mejora y cumplimiento SLSA L3 para fortalecer la seguridad en escenarios de edge computing.
Fuzzing at Mach Speed - Uncovering IPC Vulnerabilities on MacOS
Explore advanced fuzzing techniques to uncover IPC vulnerabilities in MacOS, enhancing system security and revealing potential exploits in inter-process communication.
Design is Testability - Understanding Software Testing Through Design Principles
Explore software design's impact on testability, linking design concepts to testing strategies for effective automated testing in continuous integration systems.
A Walking Tour of Wasm-Tools - Understanding WebAssembly Binary Tools
Explore the powerful wasm-tools CLI suite for manipulating, debugging, and testing WebAssembly binaries, enhancing your ability to work with and understand Wasm projects effectively.
RustSan - Retrofitting AddressSanitizer for Efficient Sanitization of Rust
Discover how RustSan enhances memory error detection in Rust programs through efficient sanitization techniques, improving performance while maintaining robust security guarantees for unsafe code blocks.
Towards Generic Database Management System Fuzzing
Discover how BUZZBEE framework revolutionizes database security testing by effectively fuzzing both SQL and NoSQL systems, revealing vulnerabilities and achieving superior code coverage compared to existing solutions.
Fuzzing BusyBox - Leveraging LLM and Crash Reuse for Embedded Bug Unearthing
Discover innovative techniques for enhancing embedded system security through LLM-powered fuzzing and crash reuse, focusing on BusyBox vulnerability detection and software testing optimization.
A Binary-level Thread Sanitizer - Why Sanitizing on the Binary Level is Hard
Explore the challenges and solutions of binary-level thread sanitization through BINTSAN, a novel approach for detecting data races in Linux x86-64 targets without source code access.
HYPERPILL: Fuzzing for Hypervisor Bugs by Leveraging the Hardware Virtualization Interface
Discover a groundbreaking approach to hypervisor security testing through HYPERPILL - a universal fuzzing framework that identifies vulnerabilities across major hypervisors using hardware virtualization interfaces.
Head First Reporting of Linux Kernel CVEs: Practical Use of the Kernel Fuzzer
Discover how to identify and report Linux kernel vulnerabilities using syzkaller fuzzer, with practical examples and step-by-step guidance on submitting findings to the Security community.
Head First Reporting of Linux Kernel CVEs - Practical Use of the Kernel Fuzzer
Discover practical techniques for finding Linux kernel vulnerabilities using syzkaller fuzzer, from initial testing to successful CVE reporting and submission to the security community.