SATCOM Terminals - Hacking by Air, Sea, and Land
Exposé des vulnérabilités critiques dans les terminaux de communication par satellite, permettant des attaques à distance sur les systèmes maritimes, aériens et terrestres. Démonstration technique incluse.
Hacking Video Conferencing Systems
Explore vulnerabilities in high-end videoconferencing systems, focusing on Polycom HDX devices. Learn about firmware analysis, device rooting, and remote exploitation techniques for H.323 protocol.
Untwining Twine
Explore the analysis and exploitation of Twine, a consumer IoT device, through reverse engineering, traffic capture, and firmware analysis. Learn techniques for understanding embedded systems.
Homemade Hardware Keylogger - PHUKD Hybrid
Explore hardware keyloggers, their pros and cons, and learn to build your own using Arduino. Covers PS2 and USB versions, payloads, and Bluetooth options.
Scrutinizing WPA2 Password Generating Algorithms in Wireless Routers
Scrutinizing WPA2 password generation algorithms in wireless routers, revealing vulnerabilities, backdoors, and security flaws in various router brands. Highlights methods for obtaining firmware and exploiting weaknesses.
Reversing and Exploiting Embedded Devices - Walking the Software and Hardware Stack
Explore embedded device security through reverse engineering and exploitation techniques, covering software analysis, hardware examination, and practical debugging methods.
Demonstrating the HRES Process
Explore embedded device security, network pin tests, and hardware research. Learn about firmware analysis, intelligence gathering, and lateral movement in IoT systems.
Embedding Security in Embedded Systems
Explore embedded system security challenges in IoT devices, from cameras to smart buildings. Learn about vulnerabilities, coordinated disclosure, and best practices for securing interconnected systems.
If You Can't Open It, You Don't Own It
Exploring hardware vulnerabilities and their impact on C++ systems, this talk delves into side-channel attacks, physical penetrations, and supply chain risks, offering insights for securing modern C++ designs.
Ghost in the Wireless - iwlwifi Edition
Explore Intel Wi-Fi chip vulnerabilities through reverse-engineering, uncovering firmware exploits and code execution risks in complex features like Wake-on-WLAN and TDLS.
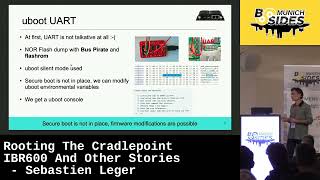
Rooting the Cradlepoint IBR600 and Hardware Security Stories
Dive into hardware security analysis and rooting techniques for Cradlepoint IBR600 routers, exploring vulnerabilities and practical exploitation methods for network devices.
Inside Dash Cam Custom Protocols and Security Vulnerabilities
Delve into comprehensive security analysis of network-connected dash cams, exploring vulnerabilities in boot processes, custom protocols, and configuration systems across multiple international manufacturers.
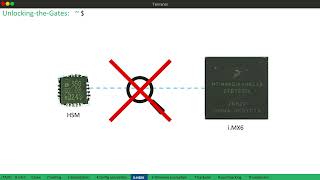
Unlocking the Gates: Hacking Industrial Remote Access Solutions
Dive into the vulnerabilities of industrial VPN gateways, exploring security flaws in remote access solutions and learning techniques to identify and understand potential system compromises.
VDA Shenanigans: Attacking and Defending Vehicle Diagnostics Adapters
Dive into vehicle diagnostics adapter security through hardware reverse engineering, firmware analysis, and defensive strategies for automotive systems protection.
Finding Zero-Day Vulnerabilities in Vilo Home Routers - Security Research Process and Discoveries
Discover how student researchers uncovered 9 zero-day vulnerabilities in Vilo routers through hardware hacking, firmware analysis, and cloud infrastructure investigation, highlighting IoT security challenges.
Generating Software Bill of Materials Through Hardware Hacking - A Case Study of Bob the Minion Router
Dive into hardware hacking techniques for extracting firmware and generating Software Bill of Materials (SBOM) from a WiFi router, exploring vulnerability discovery through practical disassembly methods.
New Isn't Always Novel - Finding Basic Vulnerabilities in Enterprise Software
Discover how basic vulnerabilities in enterprise software led to a successful Pwn2Own contest entry, featuring a command injection exploit in Lexmark printers and practical security insights.

Private Keys in Public Places - Finding and Exploiting Hidden Encryption Keys
Uncover techniques for finding hidden private keys, certificates, and encryption keys in firmware, with real-world examples from Netgear, Fortinet, and Dell's security vulnerabilities.

Beginner's Guide to Hacking IoT Devices - Building Your First IoT Security Testing Lab
Discover practical IoT hacking techniques, from selecting beginner-friendly devices to building an affordable toolkit under $100. Learn common vulnerabilities and methods to gain device access using simple tools and tactics.
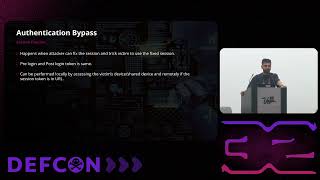
Understanding Authentication Bypass Vulnerabilities in Industrial VPN Gateways
Dive into industrial VPN gateway vulnerabilities through detailed analysis of security flaws, session hijacking risks, and hardware security bypass techniques in remote access systems.
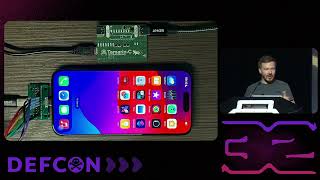
Hacking Apple's USB-C Controller: From JTAG Access to Code Execution on iPhone 15
Dive into advanced hardware hacking techniques to exploit Apple's ACE3 USB-C controller, using reverse engineering, side-channel analysis, and fault injection to gain code execution access on iPhone 15.