Smart Vacuum Cleaners as Remote Wiretapping Devices - Easterhegg - 2019
Exploración de vulnerabilidades en aspiradoras inteligentes Neato Botvac Connected, incluyendo extracción de firmware y ejecución remota de código, con implicaciones para la privacidad y seguridad del hogar.
How I Hacked My City - DefCamp 2016
Explore urban hacking through a real-world case study of Tel Aviv's open WiFi network, uncovering vulnerabilities and demonstrating practical exploitation techniques.
Bluetooth - Does It Spark Joy?
Explore Bluetooth firmware reverse engineering, security insights, and bug-finding techniques in this deep dive into wireless technology vulnerabilities.
Old New Things - An Examination of the Philips TriMedia Architecture
Explore the Philips TriMedia architecture, examining its history, features, and potential vulnerabilities through firmware analysis and hardware exploration.
Are You Sure - You Are Alone? Pwning IoT-CCTV Devices!
Explore IoT-CCTV device vulnerabilities, learn exploitation techniques, and understand the potential impact on security and privacy in this eye-opening presentation.
Unifying RF Fuzzing Techniques under a Common API - Introducing unfAPI
Explore unified RF fuzzing techniques with a common API, enhancing wireless security testing across various protocols and standards.
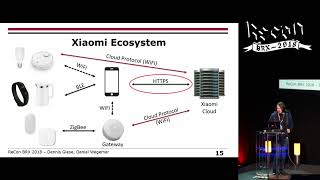
Reversing IoT - Xiaomi Ecosystem
Explore Xiaomi IoT ecosystem security, firmware extraction, and cloud communication. Learn to modify devices, implement new functions, and gain independence from proprietary cloud services.
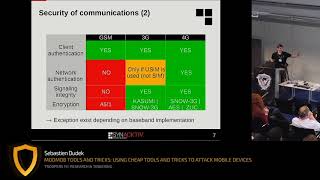
Modmob Tools - Home Made Tools to Test Mobile Devices and Monitor Networks
Explore homemade tools for testing mobile devices and monitoring networks, covering interception techniques, firmware analysis, and hardware auditing for enhanced security understanding.
A Black-Box Security Evaluation of the SpaceX Starlink User Terminal
Exploración de seguridad del terminal Starlink: vulnerabilidades, ataques de inyección de fallas y acceso root. Análisis de la red Starlink y sus implicaciones para futuras investigaciones.
ECOS Offensive Security Research Logbook
Explore eCos RTOS security, from firmware analysis to exploitation and persistence. Learn techniques for cable modem research, including memory corruption, shellcode development, and implant creation.
Stealing a Mobile Using Wormholes
Explore mobile network vulnerabilities, SIM card access techniques, and baseband firmware analysis. Learn about "wormholes" in smartphones and their potential for identity theft and unauthorized authentication.
Introduction to Reverse Engineering
Explore techniques used by crackers to bypass security, access firmware, and find vulnerabilities in hardware and software. Learn to protect your products from reverse engineering.
Scalable Graph-based Bug Search for Firmware Images
Scalable graph-based approach for efficient bug detection in firmware images, improving vulnerability search speed and accuracy for IoT devices.
Owning the Smart Home with Logitech Harmony Hub
Explore reverse engineering of Logitech's Harmony smart home hub, uncovering vulnerabilities and discussing their implications for device security and potential exploitation.
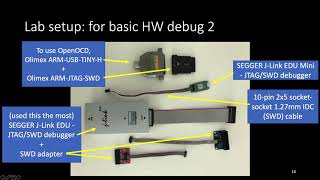
Finding New Bluetooth Low Energy Exploits via Reverse Engineering Multiple Vendors' Firmwares
Explore Bluetooth Low Energy vulnerabilities through firmware reverse engineering, uncovering remote code execution exploits at the protocol's lowest levels without authentication or pairing.
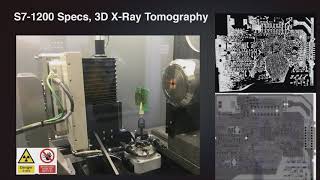
Doors of Durin - The Veiled Gate to Siemens S7 Silicon
Exploración detallada de la seguridad del PLC Siemens S7-1200, analizando su hardware, firmware y procesos de arranque para identificar vulnerabilidades y posibles vectores de ataque en sistemas de automatización industrial.

Exploiting Qualcomm WLAN and Modem Over The Air
Explore Qualcomm WLAN and Modem vulnerabilities, focusing on firmware exploitation, isolation breaches, and over-the-air control techniques. Gain insights into real-time debugging and mitigation strategies.
Security Research on Mercedes-Benz - From Hardware to Car Control
Explore Mercedes-Benz car security research, from hardware analysis to gaining control. Learn about attack surfaces, reverse engineering, and cloud control in modern connected vehicles.
Reversing the Year - Let’s Hack IoT, Ransomware and Evasive Payloads
Explore IoT vulnerabilities, ransomware tactics, and security control bypasses through live demonstrations and hands-on hacking of devices like CCTV cameras and firmware.
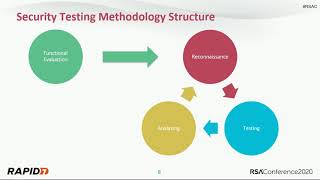
Building a Comprehensive IoT Security Testing Methodology
Comprehensive methodology for IoT security testing, covering functional evaluation, reconnaissance, testing phases for various components, and analysis. Equips testers with skills for enterprise and consumer IoT ecosystems.
Embedded Device Vulnerability Analysis Case Study Using Trommel
Comprehensive methodology for embedded device vulnerability analysis, covering firmware, web app, mobile app, and hardware. Includes case study and TROMMEL tool introduction.