
Siglent SSA3032X Spectrum Analyzer Review and Experiments
Comprehensive review of Siglent SSA3032X Spectrum Analyzer, covering features, experiments, and advanced options. Includes RF basics and practical demonstrations for beginners and professionals.
A Journey Finding Pre and Post-Auth D-Link Router Zero-Days
Explora el proceso de descubrimiento y explotación de vulnerabilidades 0-day en routers D-Link, desde obtener acceso al firmware hasta identificar y explotar fallos de seguridad para lograr ejecución remota de código.

Toniebox Reverse Engineering: Open-Source Alternatives for Children's Audio Player
Einblick in Reverse Engineering der Toniebox: Technische Details, Datenschutzprobleme und Open-Source-Alternativen wie TeddyBench und TeddyCloud für mehr Kontrolle und Funktionalität.
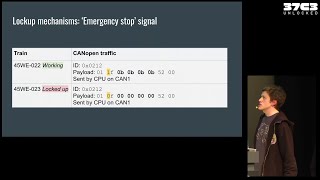
Breaking "DRM" in Polish Trains - Reverse Engineering Train Control Systems
Découvrez comment une équipe a déjoué un système de sécurité suspect dans des trains polonais en panne, mêlant ingénierie inverse et analyse technique du système de contrôle ferroviaire.
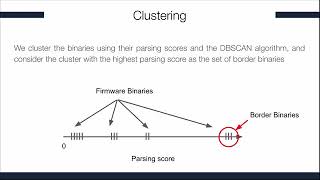
KARONTE - Detecting Insecure Multi-Binary Interactions in Embedded Firmware
Explore KARONTE, an innovative tool for detecting security vulnerabilities in embedded firmware through multi-binary interaction analysis, enhancing IoT device protection.
Heapster- Analyzing the Security of Dynamic Allocators for Monolithic Firmware Images
Explore Heapster's innovative approach to analyzing dynamic allocators in monolithic firmware, enhancing security through advanced identification and evaluation techniques.
iPhone Baseband Research and Reversing - Security Insights and Techniques
Explore iPhone baseband internals, research techniques, and tools for firmware analysis, reversing, and exploitation. Gain insights into Qualcomm baseband architecture and vulnerabilities.
Hacking Internet of Things for Bug Bounties - Aditya Gupta, LevelUp 2017
Discover techniques for finding vulnerabilities in IoT devices, covering firmware, hardware, and radio components. Learn to perform attack surface mapping on commercial smart devices.
Debugging Electronics - You Can’t Handle the Ground Truth!
Strategies for efficient electronics troubleshooting, covering tools, infrastructure, and techniques to quickly identify and fix issues in firmware, circuits, and mechanical components.
Malware Detection and Firmware Analysis Lab
Explore malware detection techniques and firmware analysis methods, including file comparison, key capture, and firmware extraction.
Live Breaking into Encrypted 3D Printer Firmware
Hands-on workshop on breaking encrypted 3D printer firmware, covering techniques like frequency analysis, known-plaintext attacks, and ARM architecture exploitation using tools such as Matplotlib and SciPy.
Reverse Engineering an EV Charger - Zaptec Pro Analysis
Dive into the reverse engineering process of a popular EV charger, exploring firmware analysis, custom bootloader creation, and potential security improvements in this insightful presentation.
IoT and OT Firmware Security Analysis with EMBA - From Firmware to Exploit
Automated firmware analysis for IoT and OT devices using EMBA, an open-source tool that detects vulnerabilities, identifies exploits, and supports penetration testing of embedded systems.
Analyzing Cellular Basebands with FirmWire
Explore FirmWire, an open-source platform for analyzing cellular basebands. Learn about baseband vulnerabilities, emulation techniques, and how to uncover security flaws in LTE and GSM stacks.
Extracting Information from Automotive Internet Units
Techniques for extracting and analyzing firmware from automotive internet modules, focusing on Qualcomm MDM-based units. Covers extraction methods, image analysis, and file system exploration.
Pwning IoT Devices Through Their Applications - From AppSec to IoT Security
Explore IoT device vulnerabilities through application security techniques, from firmware analysis to code review, leading to six new CVEs and insights on responsible disclosure.
Finding Vulnerabilities in IoT Firmware
Learn techniques for identifying vulnerabilities in IoT device firmware, enhancing your cybersecurity skills to protect against potential exploits in smart devices and embedded systems.
Large-scale Security Analysis of IoT Firmware
Explore automated security analysis techniques for IoT firmware, uncovering vulnerabilities and potential threats in connected devices at scale.
CustomProcessingUnit: Reverse Engineering and Customization of Intel Microcode
Explore Intel microcode reverse engineering and customization techniques, uncovering CPU vulnerabilities and enhancing processor functionality.
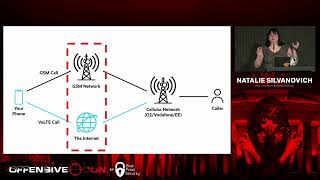
How to Hack Shannon Baseband from a Phone
Explore techniques for hacking Shannon baseband from a phone, uncovering vulnerabilities and potential exploits in mobile communication systems.
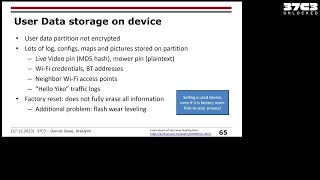
Reversing Robots and Bypassing Security: Hacking Vacuum and Lawn Robots
Explore reverse engineering and security vulnerabilities in Ecovacs robots, uncovering potential privacy risks and methods to gain root access for custom software implementation.