IoT Hacking 101 - Reverse Engineering the Xiaomi Ecosystem
Explore IoT hacking and reverse engineering techniques focused on the Xiaomi ecosystem, covering hardware methods, ecosystem analysis, and key findings in cybersecurity.
Defense Through Offense: Microcontroller Security in Meta's First Generation of Smart Glasses
Explore microcontroller security in Meta's smart glasses, focusing on defense strategies through offensive techniques and real-world applications.
ACE up the Sleeve: Hacking into Apple's New USB-C Controller
Explore Apple's USB-C controller vulnerabilities and hacking techniques with expert Thomas Roth in this cutting-edge cybersecurity presentation.
Attacking the Samsung Galaxy A Boot Chain
Explore Samsung Galaxy A* boot chain vulnerabilities and attack techniques for enhanced mobile security understanding.
One SMS to Root Them All: Exposing Critical Threats in Connected Devices
Explore critical vulnerabilities in connected devices through SMS exploitation, uncovering potential threats to millions of users worldwide.
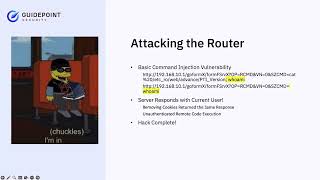
The Route to Success: Hacking a Router to Its End of Life
Explore the process of hacking a Trendnet travel router, from vulnerability hunting to exploit development. Learn methodologies and tools for both newcomers and veterans in IoT security.
IoT Firmware Analysis
Explore IoT firmware analysis techniques with Bogdan Glazov, Senior Security Researcher. Learn about vulnerabilities, hacking methods, and cybersecurity strategies in the rapidly evolving IoT landscape.
Getting Physical with USB Type-C - Windows 10 RAM Forensics and UEFI Attacks
Explore embedded microcontrollers in modern devices, focusing on the Surface Aggregator Module. Learn about security, firmware updates, and potential hardware implants in this deep dive into low-level system architecture.
Hackable Security Modules - Reversing and Exploiting a FIPS 140-2 Lvl 3 HSM Firmware
Exploring vulnerabilities in Hardware Security Modules (HSMs) through firmware analysis and reverse engineering of the TMS320C64x DSP architecture, with focus on the Utimaco SecurityServer.
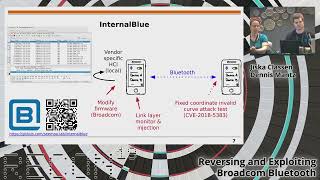
Reversing and Exploiting Broadcom Bluetooth
Insights into reverse engineering Broadcom Bluetooth firmware, including InternalBlue framework, patching techniques, and discovered vulnerabilities CVE-2018-19860 and CVE-2019-6994.
Fuzzware - Automating & Scaling Fuzzing For Firmware
Automated firmware testing using Fuzzware: emulate and fuzz embedded systems without hardware. Discover vulnerabilities in network stacks and scale security analysis for diverse devices.
Hacking Automatically - Applying Program Analysis to IoT
Discover how program analysis can uncover vulnerabilities in IoT devices. Learn about firmware analysis challenges, memory corruption patterns, and see 20 real-world examples of security flaws identified through automated techniques.
Introduction to IoT Reverse Engineering
Introduction to firmware reverse engineering for IoT devices, focusing on information gathering, emulation environment setup, and analysis techniques. Includes a practical example using a home router.
Dissecting Broadcom Bluetooth
Explore Broadcom Bluetooth firmware vulnerabilities and modifications using InternalBlue framework. Learn about security risks, pairing behavior alterations, and a remote exploit affecting popular devices.
Wallet.fail
Comprehensive analysis of security vulnerabilities in popular cryptocurrency hardware wallets, demonstrating architectural, physical, and software flaws through live hacking demonstrations and detailed explanations.
A Deep Dive Into Unconstrained Code Execution on Siemens S7 PLCs
Explore unconstrained code execution on Siemens S7 PLCs, revealing bootloader vulnerabilities and security implications. Learn about the special access feature and its potential for exploitation or forensic use.
Uncover, Understand, Own - Regaining Control Over Your AMD CPU
Explore AMD's Platform Security Processor: firmware analysis, functionality insights, and security implications. Learn to extract, replace, and observe PSP components, gaining control over your AMD CPU.
Cisco ASA Episode 2 - Striking Back - Internals and Mitigations
Explore Cisco ASA internals, reverse engineering techniques, and custom tools for exploit development. Gain insights into vulnerability analysis and mitigation strategies for network security professionals.
Secrets Of The Motherboard - Shit My Chipset Says
Explore motherboard intricacies, security features, and hidden functionalities. Uncover potential exploits, design pitfalls, and challenges in hardware security through chipset analysis and datasheet discoveries.
Look at ME! - Intel ME Investigation
Investigación detallada del Intel Management Engine, explorando su funcionamiento, implicaciones de seguridad y desafíos para desarrolladores y investigadores en el análisis de firmware propietario.
Identifying Multi-Binary Vulnerabilities in Embedded Firmware at Scale
Unveiling embedded firmware vulnerabilities through multi-binary analysis. Learn about Karonte, a novel static analysis tool that tracks inter-binary interactions to detect security flaws in IoT devices.