Discovering and Understanding the Security Hazards in the Interactions between IoT Devices, Mobile Apps, and Clouds on Smart Home Platforms
Exploring security vulnerabilities in smart home platforms through reverse engineering and phantom device testing, revealing unexpected state transitions and potential attacks.
Breaking Secure Bootloaders
Explore techniques to bypass secure bootloaders, including signature verification vulnerabilities, memory analysis, and firmware update exploits. Learn to identify and exploit weaknesses in modern device protection mechanisms.
Reversing a Japanese Wireless SD Card - From Zero to Code Execution
Discover how to reverse engineer a wireless SD card's firmware using open-source tools, uncovering its architecture and operating system to achieve code execution.
Analyzing and Fuzzing for Qualcomm Hexagon Processor
Explore techniques for analyzing and fuzzing Qualcomm Hexagon processors, overcoming challenges in firmware analysis, emulation, and hardware-dependent targets for enhanced security research.
Identifying Multi-Binary Vulnerabilities in Embedded Firmware at Scale
Explore techniques for identifying vulnerabilities in embedded firmware, focusing on multi-binary analysis, dynamic and static approaches, and scalable solutions for IoT device security.
When IoT Attacks - Hacking a Linux-Powered Rifle
Explore the security vulnerabilities of a Linux-powered precision rifle, including reverse engineering, attack surfaces, and implications of network-connected firearms.
Abusing Over-The-Air Client Provisioning
Uncovers vulnerabilities in major phone brands' network settings, allowing attackers to manipulate user data. Demonstrates attack flows and discusses vendor mitigations for these security risks.
Extracting an ELF From an ESP32
Detailed exploration of extracting ELF files from ESP32 firmware images, covering binary format analysis, conversion processes, and tools for reverse engineering IoT device firmware.
Ground Truth - 18 Vendors, 6000 Firmware Images, 2.7 Million Binaries, and a Flaw in the Linux-MIPS Stack
Presentation of data from analysis of 6000+ firmware images, revealing trends in software hardening and a critical flaw in Linux/MIPS stack affecting security across embedded devices.
What's the DFIRence for ICS?
Explore digital forensics for industrial control systems, focusing on embedded devices in critical infrastructure. Learn data collection and analysis techniques for RTUs in electric substations.
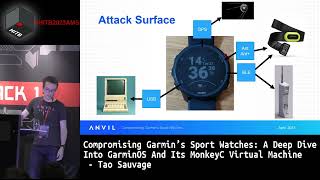
A Deep Dive Into GarminOS And Its MonkeyC Virtual Machine
Explore GarminOS and MonkeyC VM, uncovering critical vulnerabilities in Garmin devices. Learn about reverse engineering, virtual machine internals, and exploiting low-level security flaws in smart fitness technology.
Attacking IoT Speakers
Exploring vulnerabilities in IoT speakers, focusing on Sonos and Bose systems. Covers configuration flaws, diagnostic tools, API issues, and device location. Discusses broader implications for IoT security.
Hunting for Backdoors in IoT Firmware at Unprecedented Scale
Explore advanced techniques for detecting hidden vulnerabilities in IoT firmware at scale, enhancing cybersecurity practices for the rapidly expanding Internet of Things ecosystem.
Advanced SOHO Router Exploitation
Explore advanced techniques for exploiting SOHO routers, including firmware analysis, vulnerability discovery, and ARM/MIPS exploit development. Learn about 0-day vulnerabilities and post-exploitation concepts for household routers.
ARM IoT Firmware Extraction and Emulation Using ARMX
Hands-on workshop on extracting and emulating ARM IoT firmware using ARMX. Covers firmware extraction, unpacking, file system analysis, and device emulation. Practical experience with real IoT devices and tools.
BLEEDINGBIT - Your APs Belong to Us
Explore zero-day vulnerabilities in BLE chips, allowing unauthenticated network penetration. Learn about BLEEDINGBIT, its impact on enterprise APs, and potential attack scenarios.
Apple Neural Engine Internal - From ML Algorithm to HW Registers
Explore the inner workings of Apple's Neural Engine, from machine learning algorithms to hardware registers, with insights into FaceID's neural network and SEP firmware security.
EFIxplorer - Hunting for UEFI Firmware Vulnerabilities at Scale with Automated Static Analysis
Discover automated static analysis techniques for identifying UEFI firmware vulnerabilities at scale, addressing the lack of systemic approaches in x86-based systems research.
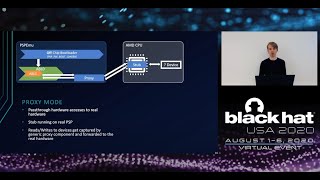
All You Ever Wanted to Know about the AMD Platform Security Processor and Were Afraid to Emulate - Inside a Deeply Embedded Security Processor
Explore AMD's Platform Security Processor: its role in system bootstrapping, security features, and proprietary nature. Gain insights into this embedded ARM core within x86 CPUs.
OEM Finder - Hunting Vulnerable OEM IoT Devices at Scale
Discover a tool for identifying vulnerable OEM IoT devices across thousands of images, revealing security risks in both supplier and vendor firmware distributions.
Pwning the Nerf Gun
Reversing and hijacking a remote-controlled Nerf tank gun through hardware, firmware, and RF analysis. Includes live demonstration of taking control and potentially shooting the conference organizer.