Growing the Community of AI Hackers with Generative Red Team Testing
Dive into the groundbreaking world of AI security testing, exploring red team methodologies, algorithmic bounties, and practical strategies for evaluating Large Language Models beyond basic exploits.
Retro Exploitation - Vintage Computing as a Vulnerability Research Playground
Explore vulnerability research and exploit development through vintage computing, focusing on the Commodore Amiga platform and practical demonstrations of retro software exploitation techniques.
CAN Injection and Vehicle Security: Investigation of Modern Car Theft Techniques
Dive into an auto security researcher's investigation of modern car theft techniques, focusing on CAN bus exploitation, vehicle security vulnerabilities, and potential protective measures.
Hacking Power Management in Data Centers - Security Vulnerabilities and Exploits
Delve into data center power management security, exploring vulnerabilities in PDUs and DCIM systems while learning critical infrastructure protection strategies and attack vectors.
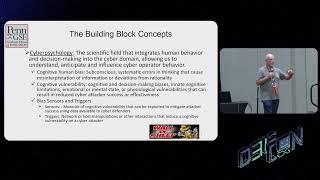
Pwning the Pwners with Mindware - Using Cyberpsychology and AI for Defensive Strategy
Discover how cyberpsychology and AI can empower defenders to exploit human vulnerabilities in cyber attacks, turning defense into an offensive advantage through psychological tactics.

Advanced ROP Framework - Pushing Return-Oriented Programming to Its Limits
Discover advanced return-oriented programming techniques with ROP ROCKET framework, featuring syscall bypassing, cross-architecture exploitation, and innovative bad byte handling for enhanced security testing.
Contactless Overflow Code Execution Vulnerabilities in Payment Terminals and ATMs
Uncover critical NFC payment terminal vulnerabilities and their exploitation through contactless attacks, including ATM jackpotting techniques and firmware manipulation across major payment systems worldwide.
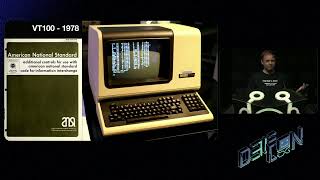
Terminally Owned - 60 Years of Terminal Escape Code Vulnerabilities
Explore terminal security vulnerabilities across platforms, from ASCII's escape character origins to modern exploit techniques, revealing critical remote code execution risks and defense strategies.
Social Engineering and Security Awareness in Virtual Reality
Dive into a thought-provoking keynote address from renowned security expert Jayson Street at DEF CON 31's DCGVR Village, exploring cutting-edge cybersecurity insights and industry perspectives.
Grand Theft Actions - Abusing Self-Hosted GitHub Runners for Supply Chain Attacks
Dive into critical security vulnerabilities in GitHub Actions, exploring real-world attacks on self-hosted runners and learning how to prevent supply chain compromises in major open-source projects.
Incubated ML Exploits: Backdooring Machine Learning Pipelines with Input Handling Bugs
Explore machine learning pipeline vulnerabilities and learn to identify, exploit, and defend against model backdoors through input handling bugs and systematic security approaches.
Top War Stories from Bug Bounty Hunting - High-Severity Exploits and Discoveries
Dive into real-world bug bounty hunting experiences, exploring high-severity vulnerabilities worth $10k-$60k, from simple RCE exploits to complex PII leakages, with detailed technical insights and lessons learned.
Exploiting Bluetooth Vulnerabilities: From Car Systems to Bank Account Security
Discover how to identify and exploit Bluetooth vulnerabilities in modern vehicles and flight systems, using BlueToolkit framework for testing, with practical tips and new attack vectors for security research.
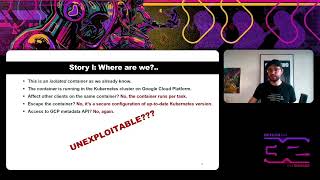
Exploiting the Unexploitable - Advanced JavaScript Vulnerability Chains in Kibana
Dive into advanced exploitation techniques for JavaScript vulnerabilities, focusing on Prototype Pollution attacks and RCE chains through real-world Kibana Bug Bounty examples and defense strategies.
Behind Enemy Lines: Going Undercover to Breach LockBit Ransomware Operations
Delve into a gripping firsthand account of infiltrating LockBit ransomware syndicate, uncovering operational tactics, leadership dynamics, and the successful unmasking of its notorious leader LockBitSupp.
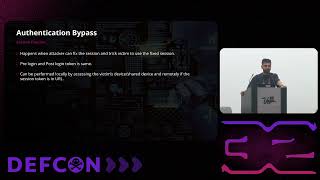
Understanding Authentication Bypass Vulnerabilities in Industrial VPN Gateways
Dive into industrial VPN gateway vulnerabilities through detailed analysis of security flaws, session hijacking risks, and hardware security bypass techniques in remote access systems.
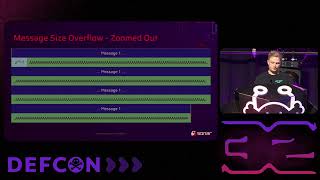
SQL Injection Isn't Dead: Smuggling Queries at the Protocol Level
Explore advanced SQL injection techniques through protocol-level query smuggling, revealing how attackers can bypass security measures and exploit database connections for authentication breaches and data theft.

The Darkest Side of Bug Bounty - Understanding Problems and Solutions in Bug Bounty Programs
Uncover the hidden challenges, secrets, and realities of bug bounty programs through expert insights on navigating relationships between hunters, clients, and platforms.
The Hack, the Crash and Two Smoking Barrels - Automotive Cybersecurity Challenges
Dive into automotive cybersecurity challenges through real-world stories and demonstrations, exploring vehicle architecture vulnerabilities and industry practices while witnessing live ECU hacking and security testing scenarios.
Reflections on a Decade in Bug Bounties - From Novice to Seasoned Hunter
Gain insights into the evolution of bug bounty hunting through a decade-long journey, from basic vulnerability reporting to crafting critical impact chains, with perspectives from both hunter and triage sides.
Xiaomi Mobile Security Vulnerabilities - Regional Exploit Analysis and Pwn2Own Competition
Delve into the behind-the-scenes journey of exploiting Xiaomi 13 Pro at Pwn2Own Toronto 2023, exploring regional security variations and the challenges of mobile device exploitation.