
Counter Deception: Defending Yourself in a World Full of Lies
Discover practical strategies to detect and defend against digital deception across network layers, from electromagnetic spoofing to false narratives, while developing critical skills to discern truth in our interconnected world.
Don't Let Your Permissions Be Hijacked - Preventing Permission Exploitation in SQL Server
Discover techniques to prevent malicious users from exploiting power user permissions through permission hijacking, ensuring robust database security.
ActiveRecord::Encryption - Stop Hackers from Reading Your Data
Learn to encrypt data in Rails applications using ActiveRecord::Encryption. Explore implementation strategies, potential pitfalls, and real-world successes from GitHub's experience.

OWASP Top Ten - Understanding and Mitigating Critical Web Application Security Risks
Explore critical web application security risks, learn to identify and mitigate vulnerabilities, and integrate OWASP ZAP with Selenium for enhanced protection.

Automated Scanning and Vulnerability Assessment of Web Applications
Leverage tools and frameworks to identify security loopholes, perform penetration testing, and ensure web application resilience against potential attacks.
CyberMirage: AI DeepFake LIVE Demo
Witness a groundbreaking AI DeepFake LIVE demo showcasing the viral CyberMirage technology. Explore cutting-edge cybersecurity implications with seasoned expert Brandon Kovacs at HackMiami XI.
Live Hacking Your Web App: Exploiting Your Open Source Dependencies
Explore web app vulnerabilities through live hacking, focusing on exploiting open source dependencies. Learn to identify and mitigate security risks in your applications.
Age of Industrialized AI - Challenges and Solutions for LLMs in Production
Explore the challenges and solutions for integrating LLMs into software, addressing hallucinations, security risks, and future developments in AI infrastructure.
Bypassing macOS Privacy Mechanisms - The Final Chapter
Explore macOS privacy vulnerabilities, bypass techniques, and Apple's security improvements. Learn about new exploits and mitigations in recent macOS versions through demos and expert insights.
Fuzzing at Mach Speed - Uncovering IPC Vulnerabilities on MacOS
Explore advanced fuzzing techniques to uncover IPC vulnerabilities in MacOS, enhancing system security and revealing potential exploits in inter-process communication.
Decoding 8 Real-World Cloud Identity Breaches
Dissection of 8 real cloud breaches exploiting insecure identities, revealing insights and mitigation strategies for common IAM vulnerabilities in cloud environments.
Continuous Security with HackerOne Bug Bounty - Cyber Defense Done Right
Leverage the world's largest ethical hacker community for proactive, continuous testing of digital assets. Custom-tailored bug bounty programs connect you with top security researchers to uncover novel vulnerabilities in your systems.
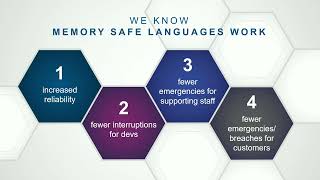
Smashing the Stack: Making Memory-Unsafe Code Less Exploitable - RSA Conference 2023
Explore memory-unsafe code vulnerabilities, their historical impact, and practical mitigations. Learn why this critical issue persists and how developers can enhance software security.
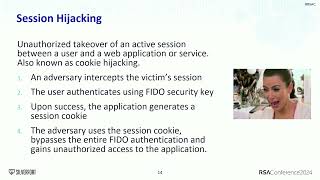
Bypassing Modern Authentication Methods for SSO - A Beginner's Guide
Explore passwordless authentication weaknesses, WebAuthn fundamentals, and attack tactics to bypass authentication. Learn credential theft from federation providers and get mitigation suggestions.
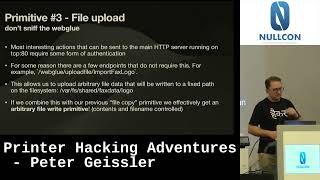
Printer Hacking Adventures - Exploiting Network Vulnerabilities
Explore printer vulnerabilities and exploit chains for Canon and Lexmark models. Learn about firmware analysis, debugging closed systems, and network security implications of office printers.
Capture The Flag - Developing a Cybersecurity Mindset for Developers
Hands-on cybersecurity challenge applying dev skills in a hacking context. Develop a security mindset to create more secure applications through an engaging Capture The Flag experience.
Hacker Panel - What Hackers Can Tell You About AI Security
Gain insights from top hackers on AI security vulnerabilities, threats, and best practices to protect AI systems from malicious attacks.
The Art of Bypassing Web Application Firewalls - Live Demos
Explore hands-on techniques for bypassing modern web application firewalls. Learn to customize methods and payloads through practical labs, enhancing your skills in WAF evasion and web security.
CompTIA Security+ Exam Practice Questions - Part 2
Comprehensive practice session for CompTIA Security+ exam, covering social engineering, cryptography, authentication, cloud security, and device vulnerabilities with detailed explanations and strategies.
Are You Botching the Security of Your AngularJS Application
Discover AngularJS's built-in security features and learn how to leverage them effectively. Explore protection against XSS, CSP implementation, and CSRF prevention for safer web applications.
Demonstrating Binary Exploitation
Explore binary exploitation through live demonstrations, vulnerability analysis, and prevention techniques. Learn about memory corruption, stack overflow, and real-world examples like the Exim mail server exploit.