Popular Web Attacks - XSS, CSRF, SSRF, SQL Injection, MIME Sniffing, Smuggling and More
Comprehensive overview of common web attacks, including XSS, CSRF, SSRF, SQL injection, and more. Practical examples and explanations enhance understanding of web security vulnerabilities.
Server Side Request Forgery
Learn to identify, exploit, and mitigate Server-Side Request Forgery vulnerabilities. Covers external and internal SSRF, bypassing blacklists, and includes practical demonstrations and real-world examples.
Bug Bounty Hunting Methodology - Jason Haddix from Bugcrowd's LevelUp
Comprehensive web hacking methodology covering reconnaissance, scanning, and exploitation techniques for bug bounty hunters and security researchers.
H@cktivitycon 2020 - Graphing Out Internal Networks with CVE-2020-13379 - Unauthed Grafana SSRF
Discover and exploit a critical SSRF vulnerability in Grafana, impacting thousands of companies. Learn methodology, see a live demo, and explore reporting and mass-exploitation experiences.
Learning Server Side Request Forgery Basics Using Portswigger's Web Security Academy
Explore Server Side Request Forgery (SSRF) basics through hands-on practice with Portswigger's Web Security Academy, enhancing your web security skills and understanding of this critical vulnerability.

What is Server-Side Request Forgery - SSRF?
Explore Server-Side Request Forgery (SSRF): its definition, potential impacts, and importance in web security. Learn to identify and mitigate this critical vulnerability.

Learn to Hack WebApps - SSRF (Server-Side Request Forgery)
Explore server-side request forgery (SSRF) vulnerabilities in web applications, understanding attack techniques and mitigation strategies for enhanced cybersecurity.
Piercing the Veil - Server Side Request Forgery Attacks on Internal Networks
Explore esoteric SSRF entry points, internal service vulnerabilities, and mitigation strategies in ethical hacking and bug bounty programs.
A New Era of SSRF - Exploiting URL Parser in Trending Programming Languages
Explore a new SSRF exploit technique targeting URL parsers in popular programming languages. Learn about protocol smuggling, fuzzing tools, and discover vulnerabilities in widely-used libraries.
API-Induced SSRF - How Apple Pay Scattered Vulnerabilities Across the Web
Explore API security vulnerabilities, focusing on Apple Pay's impact, with live demos and actionable strategies for improving defensive programming practices.

SSRF PWNs - New Techniques and Stories
Découvrez de nouvelles techniques d'attaques SSRF, leurs impacts sur la sécurité des applications web et des exemples concrets d'exploitation, présentés par deux experts en sécurité informatique.
Edge Side Include Injection - Abusing Caching Servers into SSRF and Transparent Session Hijacking
Explore Edge Side Include injection, a web attack vector exploiting caching servers. Learn how this legacy technology can lead to SSRF and session hijacking vulnerabilities in modern web infrastructure.
The 3 Way Bypass Surgery - Abusing Content Delivery Networks with Server Side Request Forgery - SSRF
Explore advanced techniques for bypassing security measures using Server Side Request Forgery (SSRF) and Content Delivery Networks (CDNs) in this comprehensive cybersecurity presentation.

Finding 0days in Enterprise Web Applications
Explore techniques for finding 0-day vulnerabilities in enterprise web applications, focusing on HCL Digital Experience, Solarwinds Web Help Desk, and Sitecore's Experience Platform.

Viral Video - Exploiting SSRF in Video Converters
Exploiting SSRF vulnerabilities in video converters using HLS playlists, potentially leading to critical security breaches in cloud-based services. Includes demonstration of attacks on major platforms.
The Road Towards 365 Bugs in Microsoft Office 365
Discover vulnerabilities in Microsoft 365 applications, including cross-tenant privacy leaks, SQLi, CSRF, SSRF, and XSS. Learn bug hunting techniques and tips for testing new Office 365 features.
When TLS Hacks You
Explore how TLS features can be exploited for attacks, focusing on Server-Side Request Forgery. Learn about a novel, cross-platform method to leverage TLS for targeting internal services.
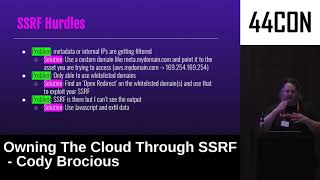
Owning the Cloud Through SSRF
Explore cloud security vulnerabilities through SSRF attacks, focusing on metadata exploitation, CVE examples, and advanced techniques like DNS rebinding for comprehensive cloud protection.

SSRF vs Business Critical Applications
Explore SSRF vulnerabilities in business-critical applications, focusing on SAP systems. Learn about XXE Tunneling and its potential to bypass security restrictions, with practical examples and attack scenarios.
Understanding CSRF and SSRF Web Security Vulnerabilities - Demo and Examples
Explore CSRF and SSRF web security vulnerabilities through practical demonstrations, understanding attack mechanisms, key differences, and essential prevention strategies for robust application security.
Realistic Web CTF Walkthrough - JWT, API Hacking, SSRF, and SQLi
Walkthrough of NahamCon2024 Mission showcasing JWT tricks, API hacking, SSRF, and SQLi. Learn advanced web security techniques and bug bounty strategies from an experienced hacker.