Applications and Cloud Hackers, Oh My!
Explore cloud security challenges, application vulnerabilities, and hacking techniques with experts Andrew Hay and Matt Johansen in this insightful BSidesLV presentation.
Occupy Burp Suite - Informing the 99% of What the 1%'ers Are Knowingly Taking Advantage Of
Explore advanced web application security testing techniques using Burp Suite, uncovering vulnerabilities and exploits often overlooked by standard security practices.
Return Oriented Programming, an Introduction
Explore Return Oriented Programming (ROP) exploitation technique, its mechanics, and practical examples for executing code in non-executable stack contexts.

The Insecurity of OAuth 2.0 in Frontends
Explore XSS threats in OAuth 2.0 frontends, assess real-world attacker capabilities, and learn effective defense strategies for securing your applications against advanced attacks.
Attacking and Defending Mobility and IoT on the Enterprise Network
Exploring modern mobile and IoT security challenges, this talk examines current enterprise defenses, demonstrates their shortcomings, and offers practical solutions for improving security in the evolving threat landscape.
A Tale of Two Sides of 2FA
Explore the complexities of two-factor authentication, its implementation challenges, and best practices for enhanced security in applications. Learn from real-world examples to protect users effectively.
The Rise of Software Supply-Chain Attacks - How Secure is Your .NET Application
Explore software supply chain vulnerabilities in .NET applications, from infrastructure to CI/CD pipelines. Learn to identify and mitigate security risks across the development lifecycle.
Analysis of and Lessons from the Xz-Utils Vulnerability - What Might Come Next
Delve into the technical analysis of the xz-utils vulnerability incident, exploring the combined attack techniques, social engineering aspects, and future implications for open-source software security.

How to Be an Ethical Hacker in 2025 - A Comprehensive Guide to Cybersecurity Skills
Master the path to ethical hacking with comprehensive guidance on foundational IT skills, networking, Linux, programming, and advanced security concepts, including web applications and wireless hacking techniques.
Multi-Step Initial Access Strategies: Desperate Infection Chains - Part 2
Explore modern infection chain techniques and multi-step strategies used by threat actors for initial access, focusing on post-MOTW era tactics and file format exploitation.
Demystifying Thread Call Stack Spoofing - Advanced Techniques for Stack Manipulation
Dive into advanced thread stack spoofing techniques, combining stack frames forging with ROP and JOP to achieve stealthy module execution and call stack manipulation.
Identifying and Securing Psychologically Vulnerable Users
Explore psychological traits that make users vulnerable to security threats and learn data-driven strategies to enhance organizational security and red team effectiveness.
Hackers in Jurassic Park: When Attackers Find a Way
Explore real-world cybersecurity breaches through engaging hacking stories, drawing parallels with Jurassic Park to understand how attackers penetrate seemingly secure digital systems.
Social Engineering Attack: How to Rob a Bank Over the Phone
Dive into a real-world social engineering case study where an expert demonstrates how he gained unauthorized access to a bank's systems through sophisticated phone manipulation techniques.
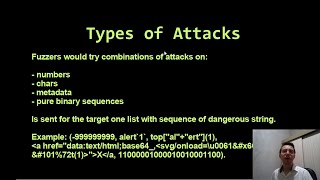
Fuzzing - Finding Your Own Bugs and Zero-Days
Master the art of fuzzer creation and vulnerability discovery, exploring buffer overflow exploitation techniques with hands-on demonstrations and practical exploit development strategies.
Open Source Intelligence Gathering for Security Testing - Recon 101
Master essential OSINT techniques and reconnaissance tools to efficiently gather critical intelligence about organizational infrastructure and potential security vulnerabilities without active network engagement.
Bug Bounty Recon: Bypassing Geographic DNS with Ensemble
Discover how Ensemble revolutionizes bug bounty hunting by bypassing GeoDNS limitations, enabling comprehensive scanning across multiple geographic regions through a distributed cluster of nodes and user-friendly web interface.
Building Scalable Reconnaissance Systems with AWS Serverless Architecture
Discover how to build a scalable, cost-effective reconnaissance framework using AWS serverless architecture for cybersecurity and bug bounty hunting, featuring automated workflows and efficient resource management.
New Isn't Always Novel - Finding Basic Vulnerabilities in Enterprise Software
Discover how basic vulnerabilities in enterprise software led to a successful Pwn2Own contest entry, featuring a command injection exploit in Lexmark printers and practical security insights.
Social Engineering and Real-Time Malware Attack Strategies - War Stories
Explore real-world social engineering tactics in targeted malware attacks, where attackers use direct communication and psychological manipulation to achieve successful system compromises.
Hacking War Stories: From Prison Systems to Tech Companies - A Series of Unfortunate Events
Dive into real-world hacking adventures, from prison systems to major tech companies, exploring identification, exploitation techniques, and potential impact across different organizational contexts.