
Beginner Bug Bounty Course - Web Application Hacking
Learn web application hacking and bug bounty hunting techniques, from basic recon to advanced exploits like SQL injection and XSS, using popular tools and platforms for hands-on practice.
Bug Bounty
Comprehensive guide to bug bounty hunting, covering methodologies, tools, and techniques for identifying vulnerabilities in web applications and networks.
Revealing SSNs and Hacking Reddit: A Bug Bounty Journey
Descubre cómo identificar vulnerabilidades IDOR y aplicarlas en bug bounty. Aprende de experiencias reales en la búsqueda de fallos de seguridad en plataformas populares.
Rompiendo los Miedos - Mi Camino Hacia la Crítica y el Bug Bounty
Descubre cómo superar miedos en bug bounty y aprende sobre un reporte público de vulnerabilidad IDOR en Reddit que permitía cambiar enlaces de usuarios sin su conocimiento.
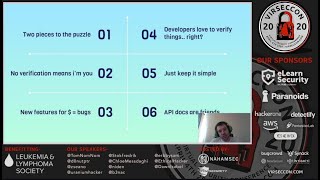
Unique Mindset - Hacking Techniques and Favorite Findings
Explore zseano's unique hacking mindset through real-world examples, favorite findings, and insights on identifying critical vulnerabilities in web applications.
Bad API, HAPI Hackers!
Explore API hacking methodology, from information gathering to privilege escalation. Learn techniques for testing vulnerabilities, automating processes, and uncovering critical security flaws in web applications.
Bugcrowd University - Broken Access Control Testing
Learn white hat hacking techniques for identifying and exploiting broken access control vulnerabilities, including IDOR, path traversal, and logic flaws, to enhance your bug bounty hunting skills.
Hunting IDOR with Z-winK - Part 2
Dive deeper into hunting Insecure Direct Object Reference (IDOR) vulnerabilities for significant rewards. Learn advanced techniques and strategies from expert Z-winK in this follow-up presentation.

Owning Cody's First Blog - RCE on Hacker101 and Hacking on FFH from BugBountyNotes.com - IDOR
Explore IDOR and LFI/RCE vulnerabilities through hands-on hacking exercises on Hacker101 and BugBountyNotes.com platforms, enhancing your web security skills and bug bounty hunting techniques.
Using BurpSuite's Intruder for Bug Hunting and CTF Challenges
Learn to use BurpSuite's Intruder for bug hunting and solving CTF challenges, focusing on IDOR, XSS, and LFI/RCE vulnerabilities.