Caido - Web Application Security Testing Tool Overview and Demonstration
Explore Caido, a powerful web application testing tool. Learn its workflows, bypass techniques, and scripting capabilities to enhance your cybersecurity toolkit and improve penetration testing skills.

Spring Security - CSRF Token Protection - Lecture 31
Explore Cross-Site Request Forgery protection in Spring Security, enhancing web application security against unauthorized actions and data manipulation.
Don't Make These 10 SQL Mistakes
Avoid common SQL pitfalls: optimize queries, prevent injections, design efficient tables, handle NULL values, use transactions, and understand joins for better database performance.
AI and Disinformation Campaigns: Impacts and Prevention
Explore AI's role in global disinformation campaigns, their long-term impacts, and strategies for individuals to combat misinformation in the digital age.
Realistic Web CTF Walkthrough - JWT, API Hacking, SSRF, and SQLi
Walkthrough of NahamCon2024 Mission showcasing JWT tricks, API hacking, SSRF, and SQLi. Learn advanced web security techniques and bug bounty strategies from an experienced hacker.
Application Security from Start to Finish
Comprehensive guide to integrating security throughout the development process, covering secure environments, dependency management, vulnerability scanning, and advanced testing techniques.
Exploring a New Class of Kernel Exploit Primitive
Uncover innovative kernel exploit techniques using limited primitives, focusing on turning seemingly benign bugs into powerful attack vectors for code execution and privilege escalation.
The Aftermath of a Social Engineering Pentest - Are We Being Ethically Responsible?
Explore ethical challenges and solutions in handling social engineering pentest aftermath, focusing on responsibility, consequences, and improving security culture.
I Am Whoever I Say I Am - Infiltrating Identity Providers Using a 0-Click Exploit
Explore unauthenticated remote code execution in popular IAM solutions, covering past attacks, audit approaches, and vulnerability chaining for infiltrating identity providers.
Cracking the Lens - Targeting HTTP's Hidden Attack-Surface
Explore hidden attack surfaces in modern web infrastructure, focusing on transparent systems for performance and analytics. Learn to identify and exploit overlooked vulnerabilities.
Exploiting USB-IP in Linux
Explore USB/IP vulnerabilities in Linux, including buffer overflow and data injection. Learn about architecture, protocol, and security implications of this USB device sharing framework.
Cross the Wall - Bypass All Modern Mitigations of Microsoft Edge
Explore techniques to bypass ASLR, DEP, and CFG exploit mitigations in Microsoft Edge on Windows 10, even with arbitrary address read/write capabilities.
Delegate to the Top - Abusing Kerberos for Arbitrary Impersonations and RCE
Explore Kerberos delegation vulnerabilities in Windows networks, learning techniques for unauthorized impersonation and remote code execution. Gain insights into potential security risks and mitigation strategies.
How I Used to Rob Banks
Ethical hacker shares thrilling tales of bank heists, revealing security flaws through lockpicking, social engineering, and digital exploits. Learn valuable lessons on improving organizational defenses.
CatPhish Automation - The Emerging Use of Artificial Intelligence in Social Engineering
Explore how advanced AI is being incorporated into fraudulent scams and phishing attacks, and its implications for future cybersecurity threats.
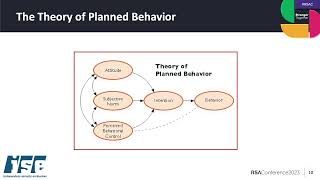
Protecting the Organization - The Psychology of Social Engineering
Explore the psychological aspects of social engineering attacks and learn effective strategies to safeguard your organization against human-targeted security vulnerabilities.
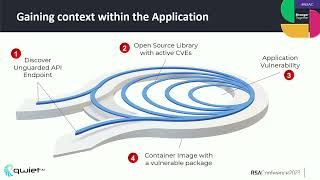
Hacking Exposed - Hacking the Sec into DevOps
Live demonstration of vulnerabilities in source code, showcasing security challenges in DevOps and exploring practical solutions for integrating robust security measures into development processes.
Social Engineering with AI: From Traditional Attacks to Next-Generation Techniques
Discover how AI tools transform social engineering tactics, from crafting sophisticated phishing to conducting vishing operations, while learning both offensive techniques and defensive strategies for modern security awareness.
Unraveling the Threads of USPS Smishing and Fighting Back - Reverse Engineering SMS Phishing Kits
Dive into the technical investigation of USPS-themed SMS phishing attacks, exploring vulnerability exploitation, reverse engineering techniques, and methods to combat scammer operations targeting US consumers.
Password Cracking 201 - Beyond the Basics
Advanced techniques for password cracking, exploring methods beyond basic approaches. Enhance your cybersecurity skills and learn to identify vulnerabilities in password systems.
Mirror Mirror - Reflected PDF Attacks Using SQL Injection
Explore advanced SQL injection techniques for exploiting PDF vulnerabilities, focusing on reflected attacks and their potential impact on web application security.